Appliances / Keel ntfy
Keel ntfyntfy 2.11
Keel release 19.0-6 · image debian-13-keel-ntfy_19.0-6_amd64.tar.zst
ntfy is a server that sends a message to a phone. This layer is the alert server of Keel Linux for one site (handbook decision 0063). It is built on the web layer.
Install
LXC template, for Proxmox VE
debian-13-keel-ntfy_19.0-6_amd64.tar.zst
sha256 42ebc5588d6916b913cd922b1d4534c2d2ac99594972215bfa8e6e99686c429b
With the Keel index
keel-pve gets the signed index of the Keel templates and checks the template against it. The Templates dialog of the Proxmox web interface does not show Keel templates. Install keel-pve from the Keel archive, suite trixie-testing, as its README says. Then run these commands on the Proxmox node:
keel-pve update
keel-pve download local keel-ntfy
With the file
- Download the template, its
.sha512and its.sha512.asc. - Check the signature. Then check the digest.
- Copy the template to
/var/lib/vz/template/cache/on the Proxmox node.
curl -fLO https://mirror.keellinux.org/images/debian-13-keel-ntfy_19.0-6_amd64.tar.zst -O https://mirror.keellinux.org/images/debian-13-keel-ntfy_19.0-6_amd64.tar.zst.sha512 -O https://mirror.keellinux.org/images/debian-13-keel-ntfy_19.0-6_amd64.tar.zst.sha512.asc
curl -fLO https://archive.keellinux.org/keel-images-keyring.asc
sqv --keyring keel-images-keyring.asc debian-13-keel-ntfy_19.0-6_amd64.tar.zst.sha512.asc debian-13-keel-ntfy_19.0-6_amd64.tar.zst.sha512
sha512sum -c debian-13-keel-ntfy_19.0-6_amd64.tar.zst.sha512
cp debian-13-keel-ntfy_19.0-6_amd64.tar.zst /var/lib/vz/template/cache/
If sqv prints E71DB9C3CA6AC18075395CC3ED3A709C4F3E2F3C, the signature is good. It also prints "Missing key" for the main key of the project. This is expected.
Make the container
pct create 200 local:vztmpl/debian-13-keel-ntfy_19.0-6_amd64.tar.zst --hostname ntfy \
  --unprivileged 1 --features nesting=1 \
  --net0 name=eth0,bridge=vmbr0,ip6=auto
Start the container and log in on its console as root. The first boot asks its questions there.
ISO, for a virtual or a real machine
debian-13-keel-ntfy_19.0-6_amd64.iso
sha256 657e7d26409d5b6b4e484cac71f37c783a1e78d0ded07769c8570332869c3ed9
curl -fLO https://mirror.keellinux.org/images/debian-13-keel-ntfy_19.0-6_amd64.iso -O https://mirror.keellinux.org/images/debian-13-keel-ntfy_19.0-6_amd64.iso.sha512 -O https://mirror.keellinux.org/images/debian-13-keel-ntfy_19.0-6_amd64.iso.sha512.asc
curl -fLO https://archive.keellinux.org/keel-images-keyring.asc
sqv --keyring keel-images-keyring.asc debian-13-keel-ntfy_19.0-6_amd64.iso.sha512.asc debian-13-keel-ntfy_19.0-6_amd64.iso.sha512
sha512sum -c debian-13-keel-ntfy_19.0-6_amd64.iso.sha512
Boot the machine from the ISO and install. The first boot of the installed system asks the same questions as the template.
The first boot
The questions of the first boot, of all the modes and roles. A node asks only those of its mode and role (the guides below show each one):
- Root Password password
- ntfy domain
- ntfy password password
- System Notifications
No password is copied between nodes: only the invite lines (decision 0076).
Services
nginx, ntfy, ssh, webmin, postfix, cron, monit
Addresses the commissioning checked
https://127.0.0.1/v1/healthhttp://127.0.0.1/v1/healthhttps://127.0.0.1/keel-healthhttp://127.0.0.1/keel-healthhttps://127.0.0.1:12321/
Screenshots
open /v1/health
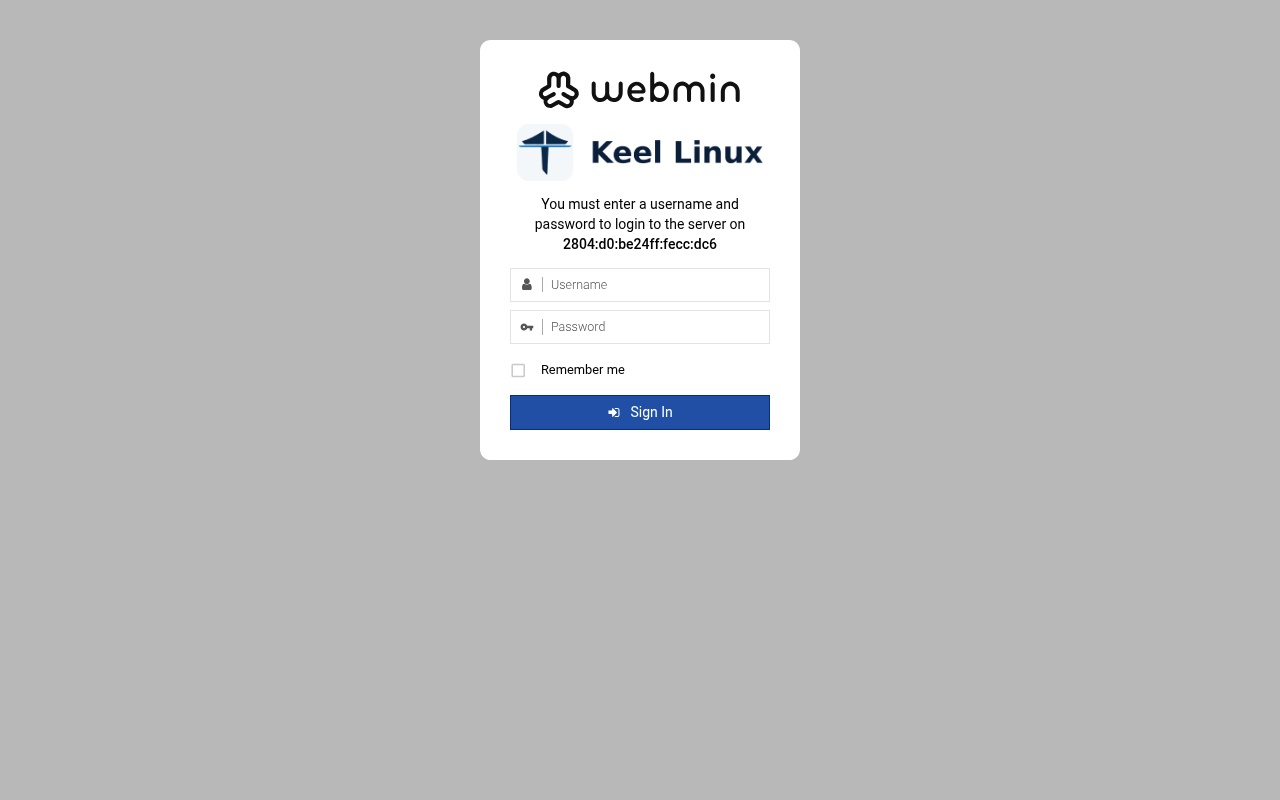
user root, the root secret
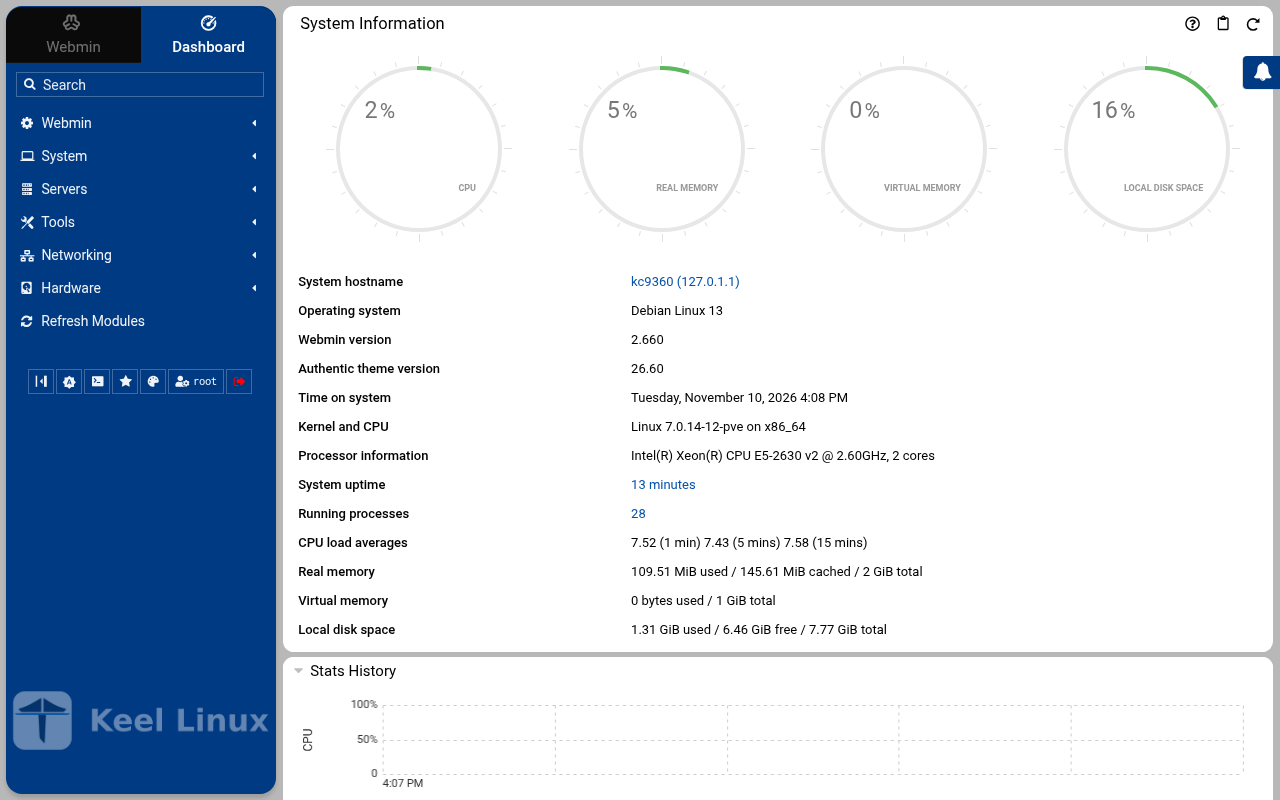
after the login: the page the login opened
Installation modes
Each column is one machine. Each row is one screen, in the order the machine showed it, with what the operator typed or chose. A secret is named, never shown.
Simple: one node
the LXC template, answered on the console (br1)
- 1
root password
the screen, as text
Connected to tty 1
Type <Ctrl+a q> to exit the console, <Ctrl+a Ctrl+a> to enter Ctrl+a itself
press Enter within 5 s to answer first-boot questions
Keel Linux Configuration Console KC9360 appliance services                                                    < Quit >         Web:https://[2804:710:d0:5:be24:11ff:fecc:dc6]Webmin:     https://[2804:710:d0:5:be24:11ff:fecc:dc6]:12321SSH/SFTP:   root@2804:710:d0:5:be24:11ff:fecc:dc6 (port 22) Keel Linux Configuration Console KC9360 appliance services                                  < Quit >       Web:https://[2804:710:d0:5:be24:11ff:fecc:dc6]Webmin:     https://[2804:710:d0:5:be24:11ff:fecc:dc6]:12321SSH/SFTP:   root@2804:710:d0:5:be24:11ff:fecc:dc6 (port 22)
Debian GNU/Linux 13 kc9360 tty1
kc9360 login: root
Password:
Keel Linux ntfy 19.0-trixie-amd64
IPv6 Web:  https://[2804:710:d0:5:be24:11ff:fecc:dc6]
IPv6 SSH:  root@2804:710:d0:5:be24:11ff:fecc:dc6
Welcome to kc9360, Keel Linux 19.0 (Debian 13/Trixie)
System information for Tue Nov 10 15:55:36 2026 (UTC+0000)
System load:  7.53              Memory usage:  10.3%
Processes:    33                Swap usage:    0.0%
Usage of /:   11.6% of 7.78GB   Networking not configured
This system is not initialized yet: run keel-init to set it up.
For Advanced commandline config run:    confconsole
For more info see: https://github.com/Keel-Linux/confconsole
Linux kc9360 7.0.14-12-pve #1 SMP PREEMPT_DYNAMIC PMX 7.0.14-12 (2026-08-11T11:05Z) x86_64
=== Keel Linux - First boot configuration
Root Password
Please enter new password for the root account.
Choose how to set this password:
Generate  A strong random password (recommended)
Manual    Type my own password
<  OK  >Generate  A strong random password (recommended)Manual    Type my own password
Keel Linux - First boot configuration
Root Password
Please enter new password for the root account.
Password Requirements
- must be at least 8 characters long
- must contain characters from at least 3 of the
following categories: uppercase, lowercase, numbers,
symbols
<  OK  >x
typed:
(the root secret) - 2
root password
the screen, as text
********
Keel Linux - First boot configuration
Root Password
Confirm password
Password Requirements
- must be at least 8 characters long
- must contain characters from at least 3 of the
following categories: uppercase, lowercase, numbers,
symbols
<  OK  >x
typed:
(the root secret) - 3
ntfy domain
the screen, as text
********
Keel Linux - First boot configuration
kc9360.pop.coop
Domain name
xxx The name this machine is reached by, with its domain,    xx for example blog.example.org. It becomes the hostname,   xx the name /etc/hosts answers for this machine, and the    xx domain a TLS certificate is requested for in             xx confconsole.xxxx Leave the field empty to keep the name the machine has.  xxxx Fully qualified domain name:x
<Apply>x
>fqdn: /etc/keel/instance.yaml already declares the name, not written
=== Keel - First boot configuration
kc9360.pop.coop
ntfy domain
xxx Enter the public name of this ntfy server, for example   xx ntfy-br1.example.org. The server answers onxx https://NAME.x
<Apply>x
typed:
ntfy.example.org - 4
ntfy password
the screen, as text
ntfy.example.org
Keel - First boot configuration
ntfy password
Enter the password of the ntfy administrator account.
Choose how to set this password:
Generate  A strong random password (recommended)
Manual    Type my own password
<  OK  >Generate  A strong random password (recommended)Manual    Type my own password
Keel - First boot configuration
ntfy password
Enter the password of the ntfy administrator account.
Password Requirements
- must be at least 8 characters long
- must contain characters from at least 3 of the
following categories: uppercase, lowercase, numbers,
symbols
<  OK  >x
typed:
(the app secret) - 5
ntfy password
the screen, as text
********
Keel - First boot configuration
ntfy password
Confirm password
Password Requirements
- must be at least 8 characters long
- must contain characters from at least 3 of the
following categories: uppercase, lowercase, numbers,
symbols
<  OK  >x
typed:
(the app secret) - 6
alert email
the screen, as text
********>user admin added with role admin
changed password for user admin
changed role for user admin to admin
user publisher added with role user
changed password for user publisher
changed role for user publisher to user
granted write-only access to topic *
user publisher (role: user, tier: none)
- write-only access to topic *
ntfy serves https://ntfy.example.org: administrator 'admin', publisher 'publisher', token in /etc/keel/secrets/ntfy_publish_token
keelfirstboot mode: simple, the one mode ntfy allows, was NOT recorded: /etc/keel/instance.yaml was NOT changed: the values would not make a valid description.
$ keel spec validate --no-secret-files --spec /etc/keel/instance.yaml.paxb4bpe.keelcli-new
Error: /etc/keel/instance.yaml.paxb4bpe.keelcli-new: app.options.base_url: required by ntfy, which gives no default
keel validate: exit 3, the spec is valid YAML but fails validation; every error is listed above
keelfirstboot role: no installation.mode yet: the role follows the mode, and keel-init asks both
keelfirstboot cloud: Keel Cloud is not available yet: no key is asked, and this node runs standalone. It is offered once /etc/keel/cloud-endpoint names the service.
=== Keel Linux - First boot configuration
System Notifications and Critical Security Alerts
Enable local system notifications (root@localhost) to be
forwarded to your regular inbox. Notifications include
security updates and system messages.
Email:
<Enable>        < Skip >x
typed:
admin@example.org - 7
web: health
typed:
open /v1/health - 8
web: webmin
typed:
user root, the root secret - 9
web: webmin-after
typed:
after the login: the page the login opened
the ISO in a virtual machine (br1)
- 1
installer-boot
- 2
installer-boot
- 3
partitioning
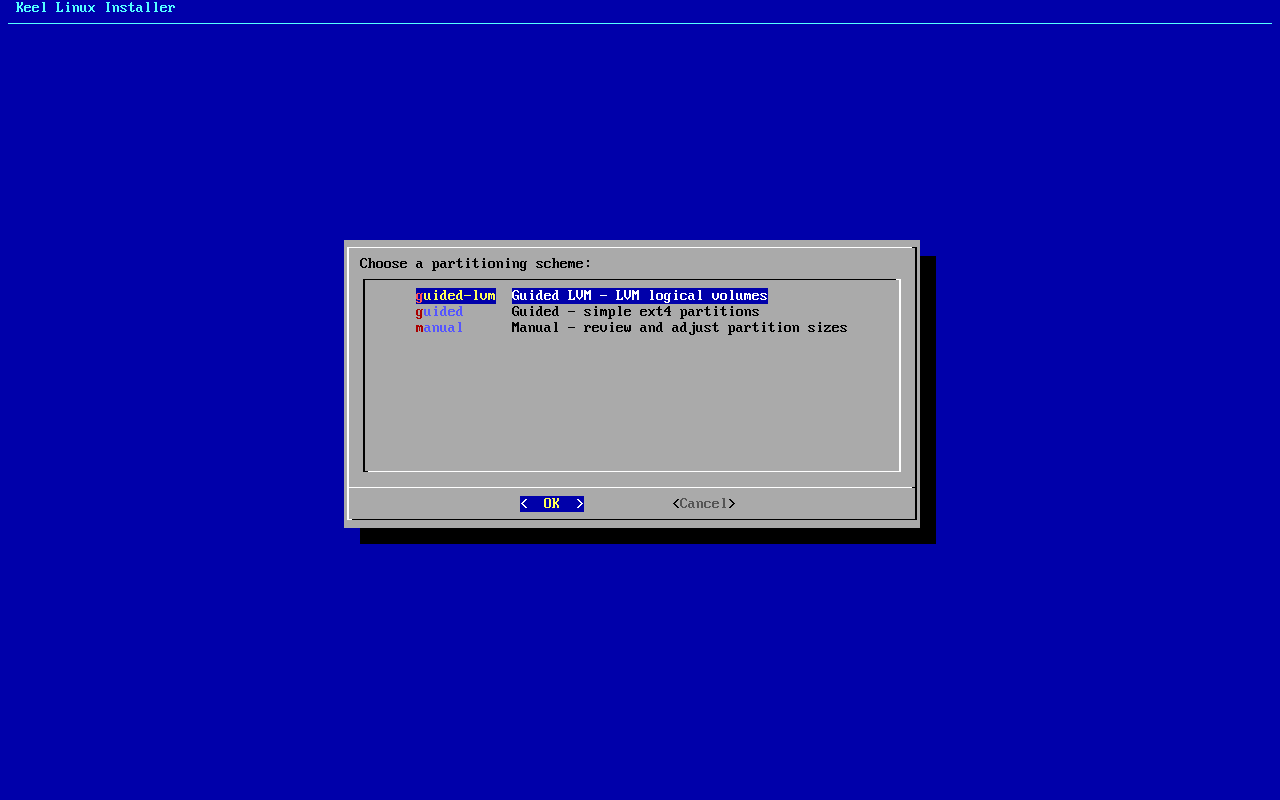
typed:
<ret> - 4
separate boot
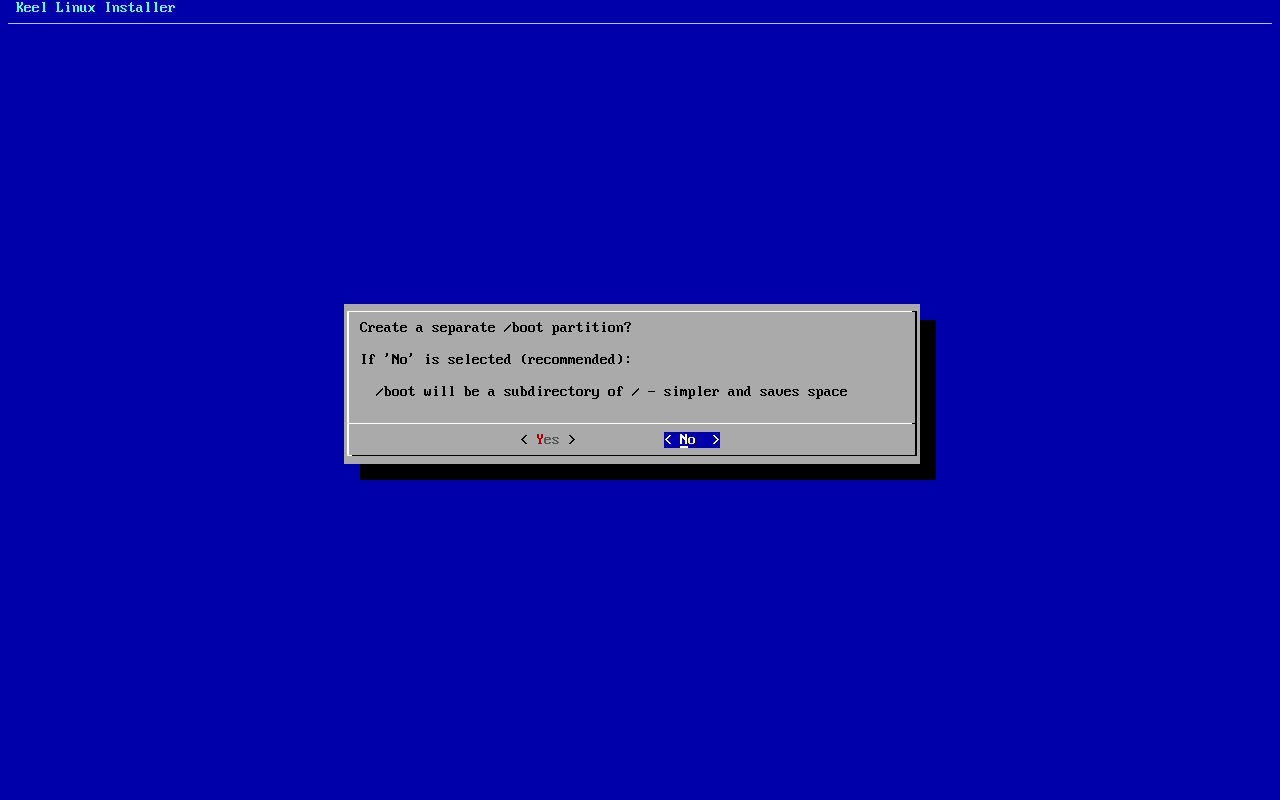
typed:
n - 5
scheme
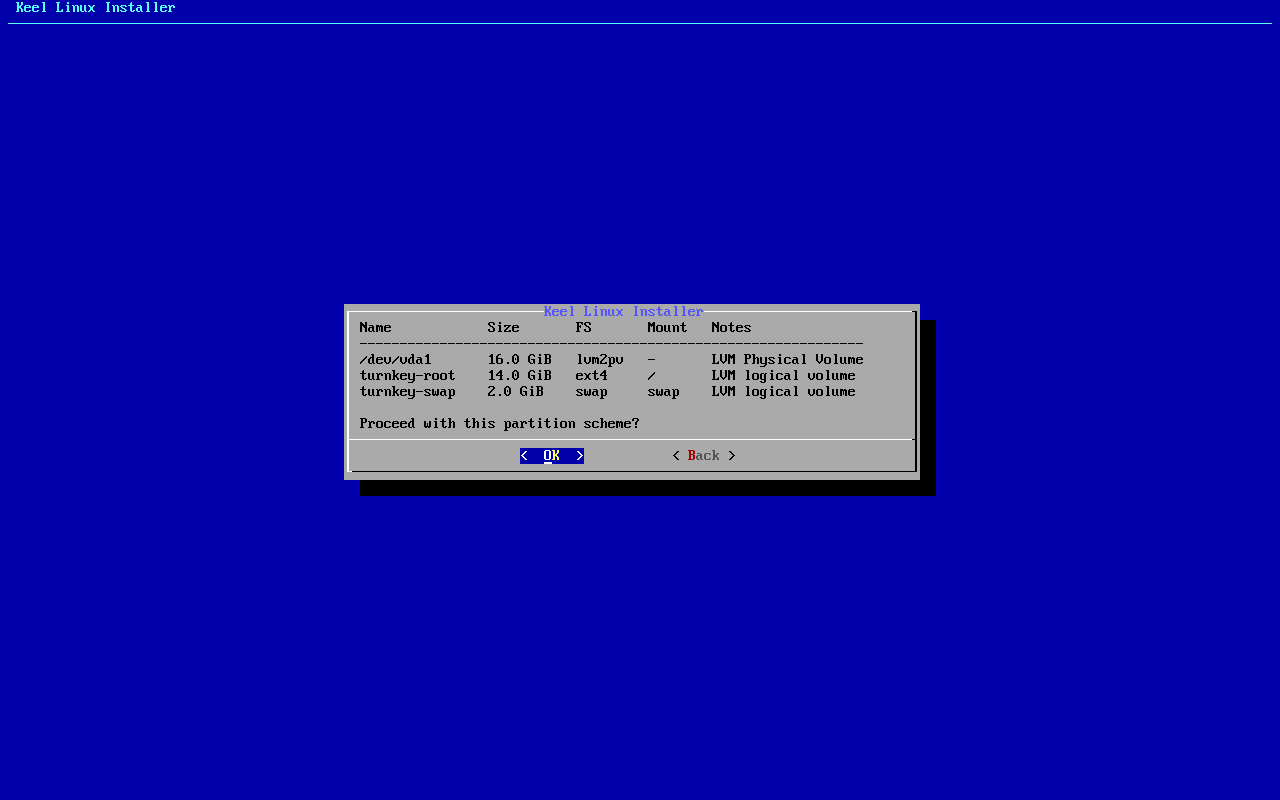
typed:
<ret> - 6
erase
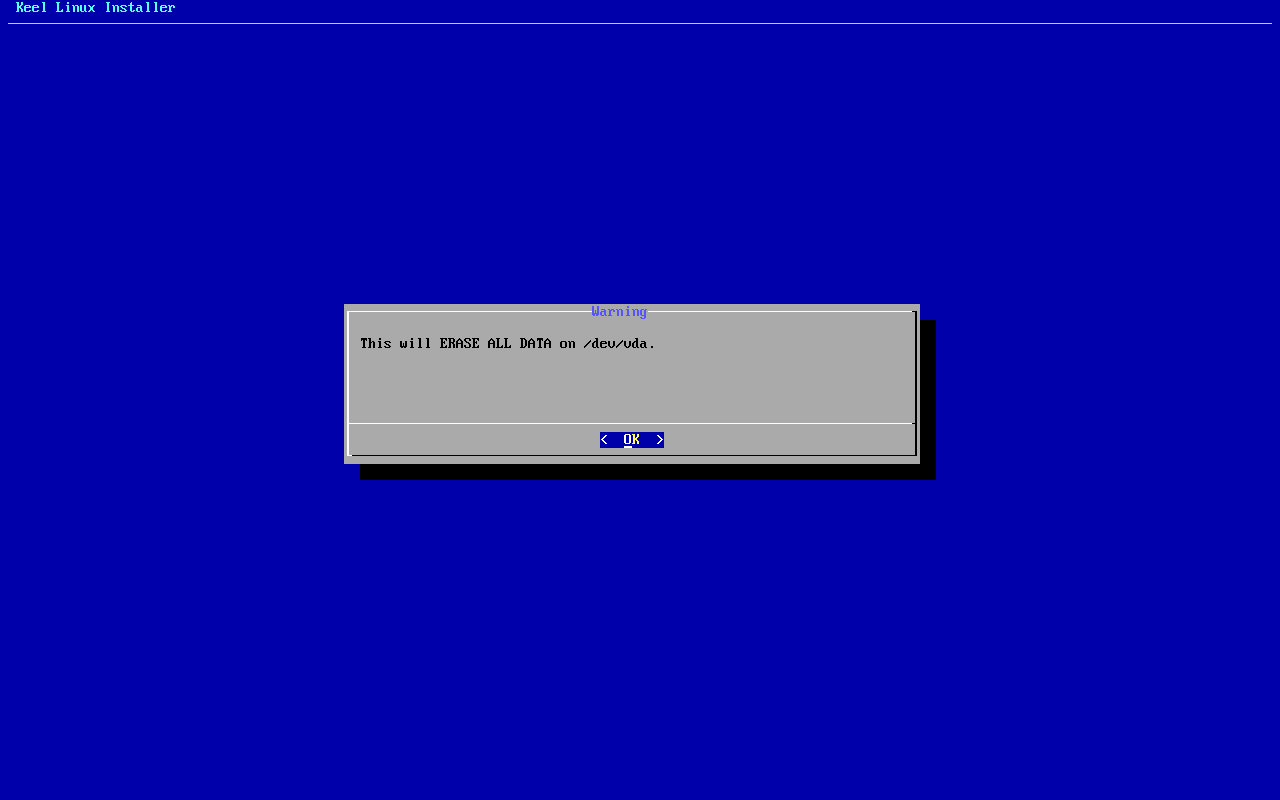
typed:
<ret> - 7
begin
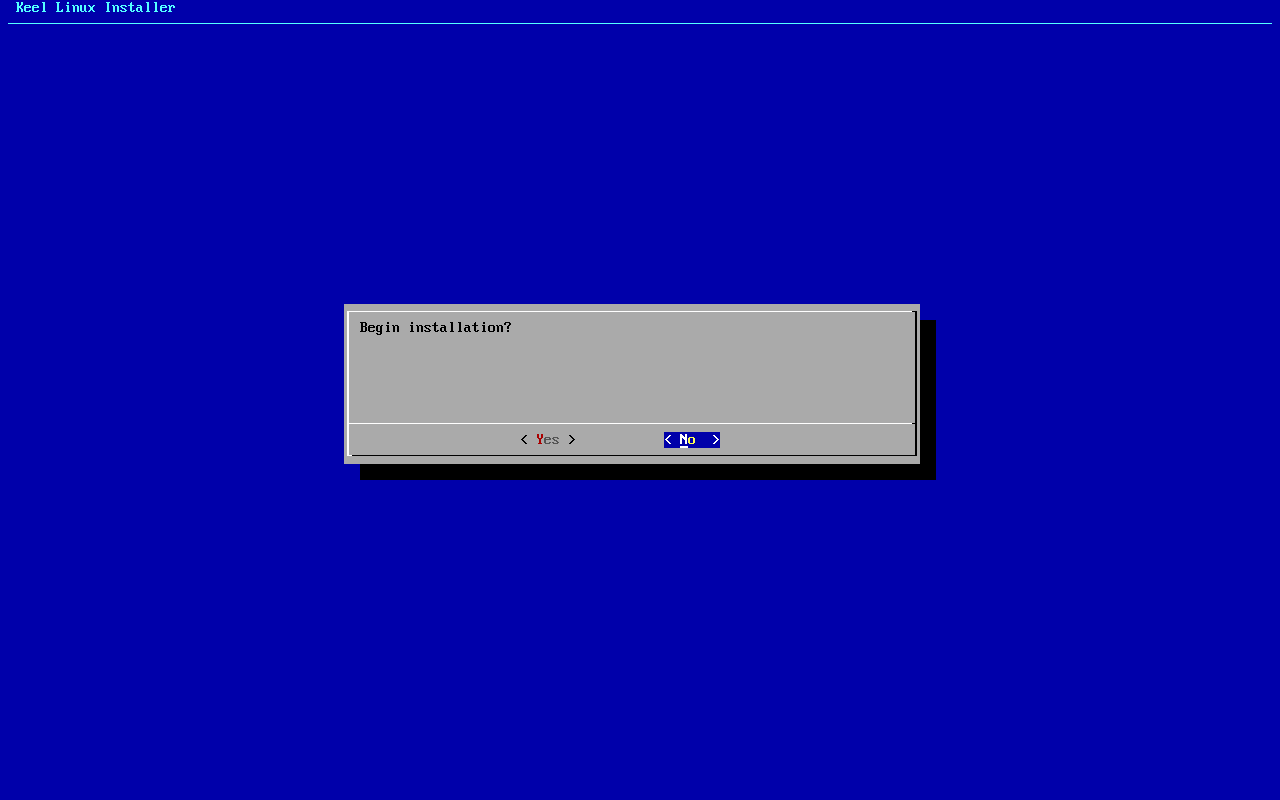
typed:
y - 8
installer-wait
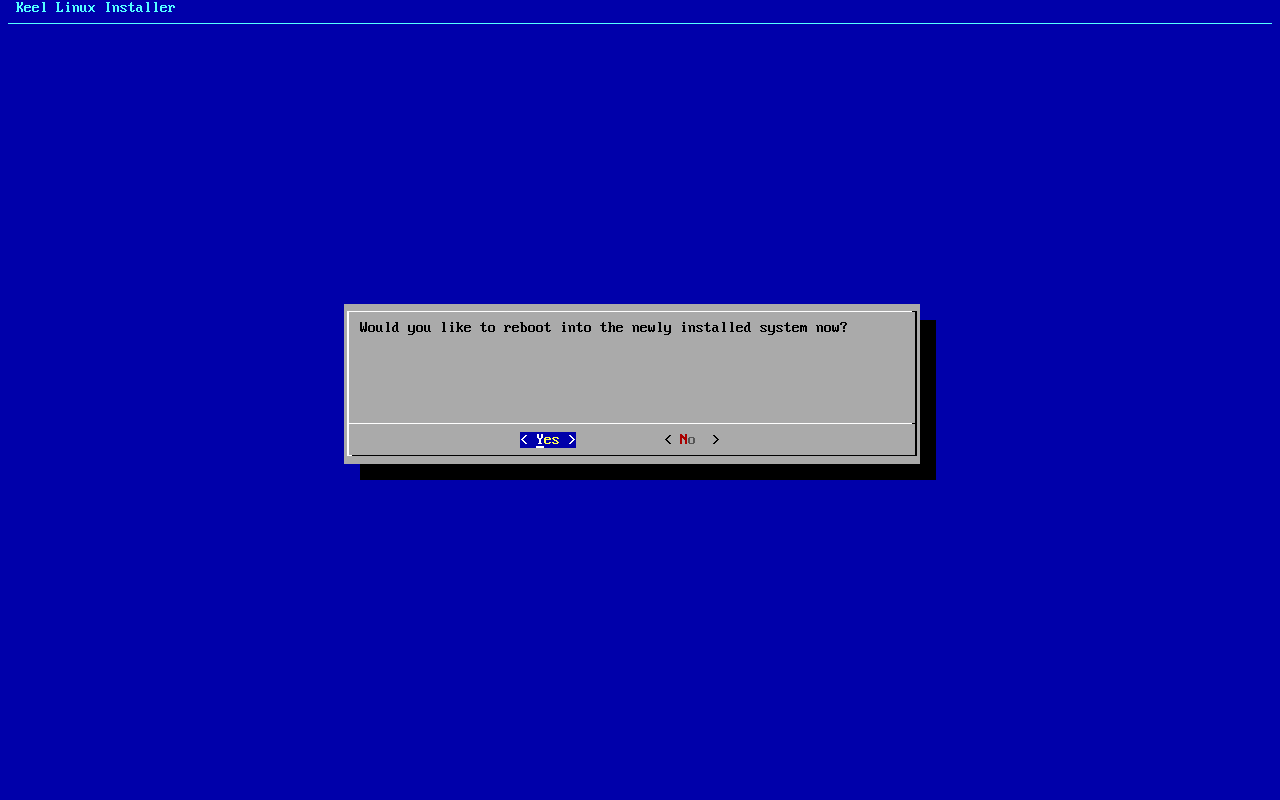
- 9
reboot
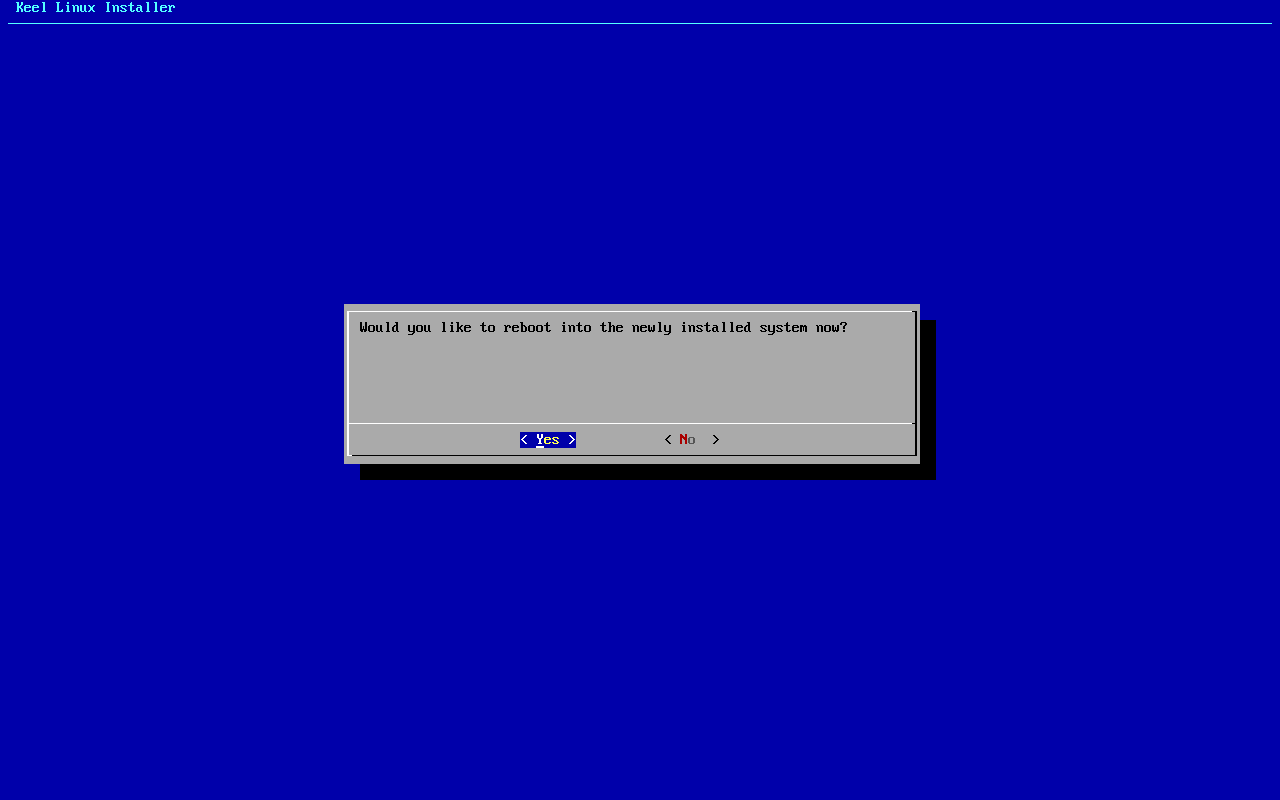
typed:
y - 10
medium
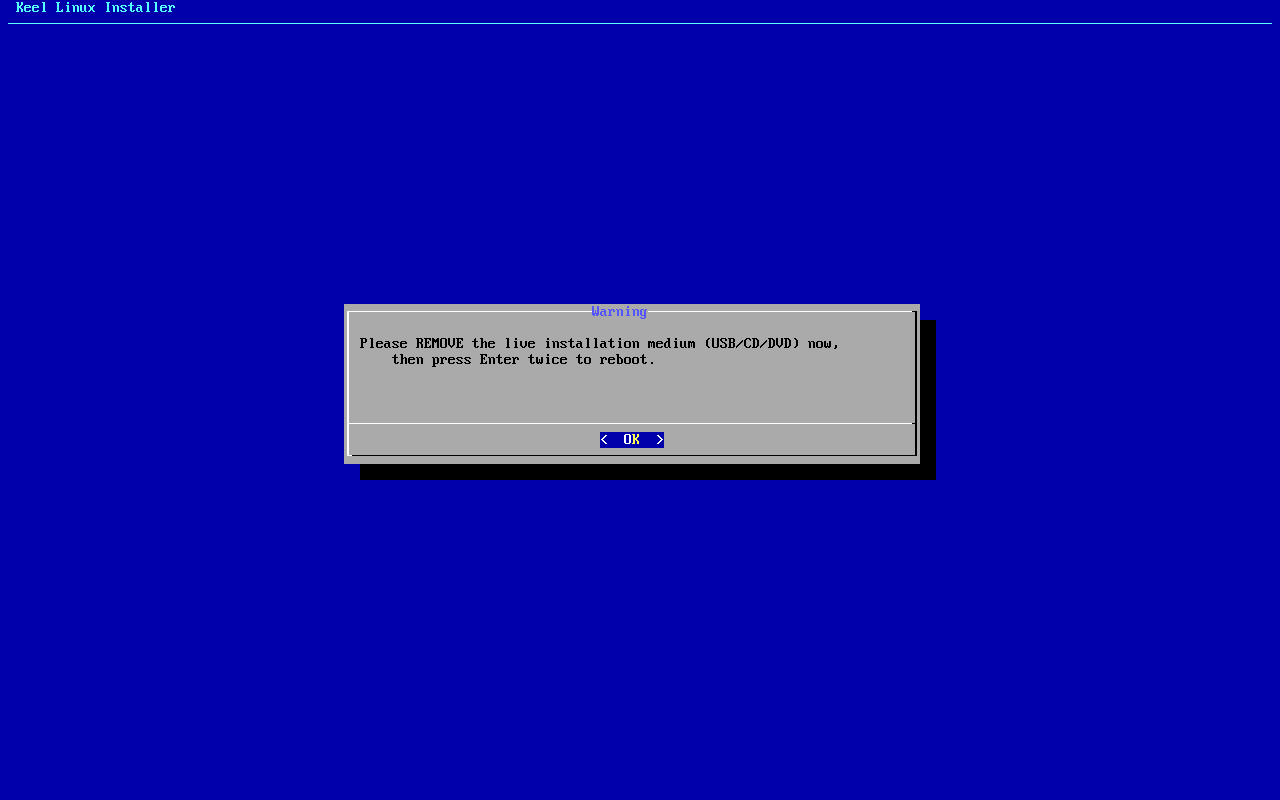
typed:
<ret><ret> - 11
root password-menu
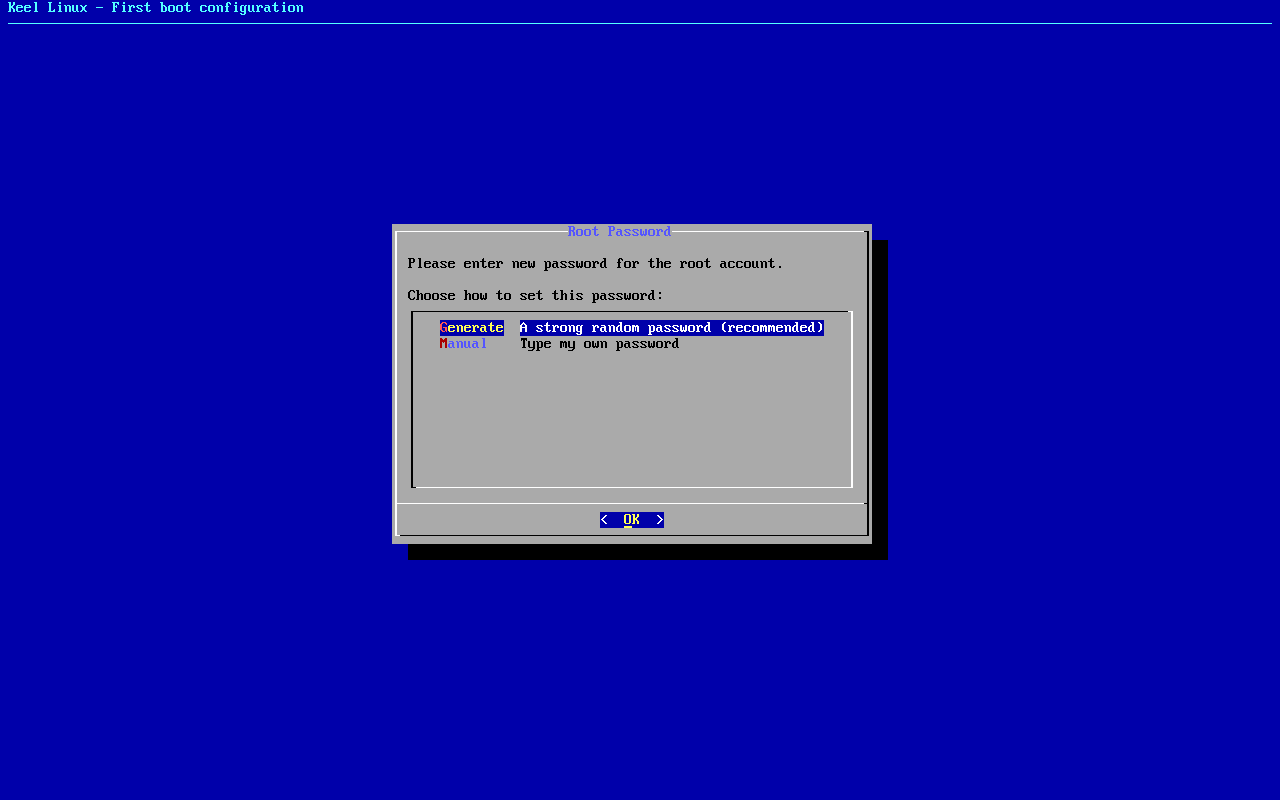
typed:
m<ret> - 12
root password
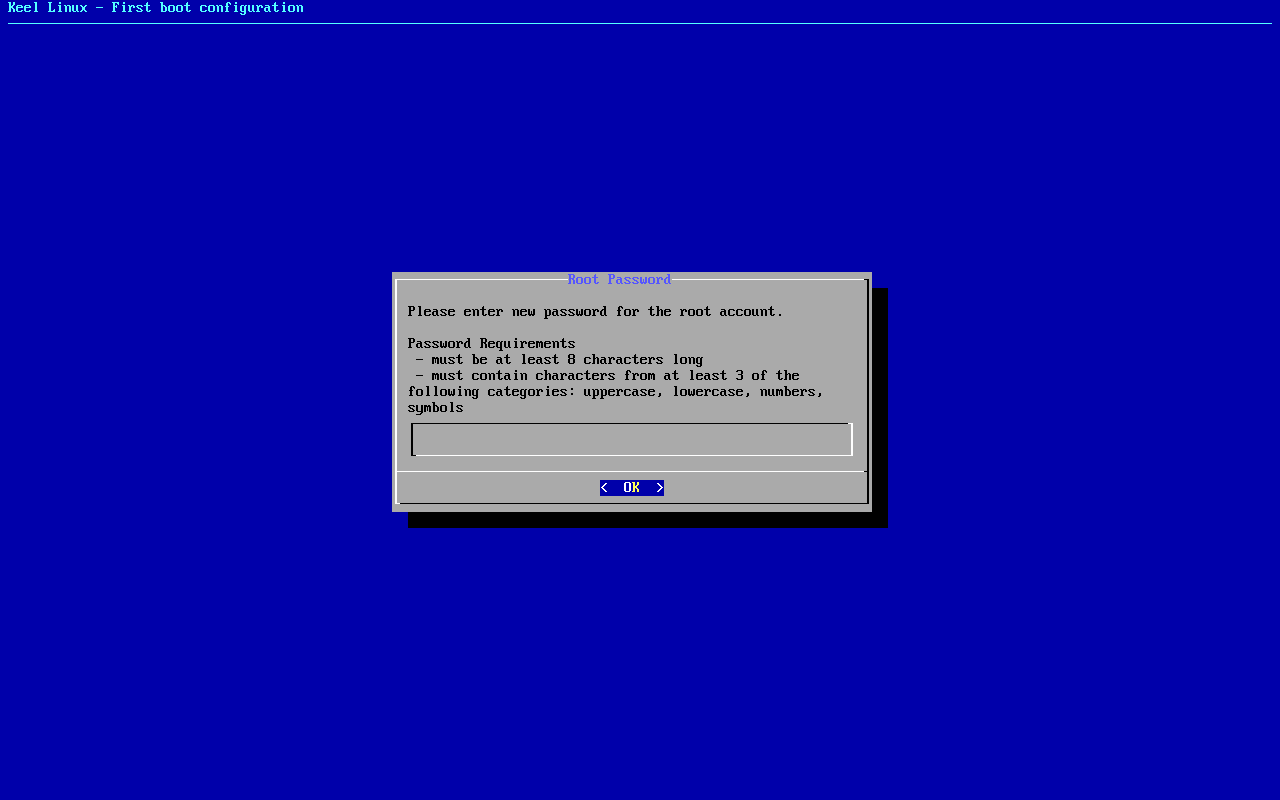
typed:
(the root secret)<ret> - 13
root password
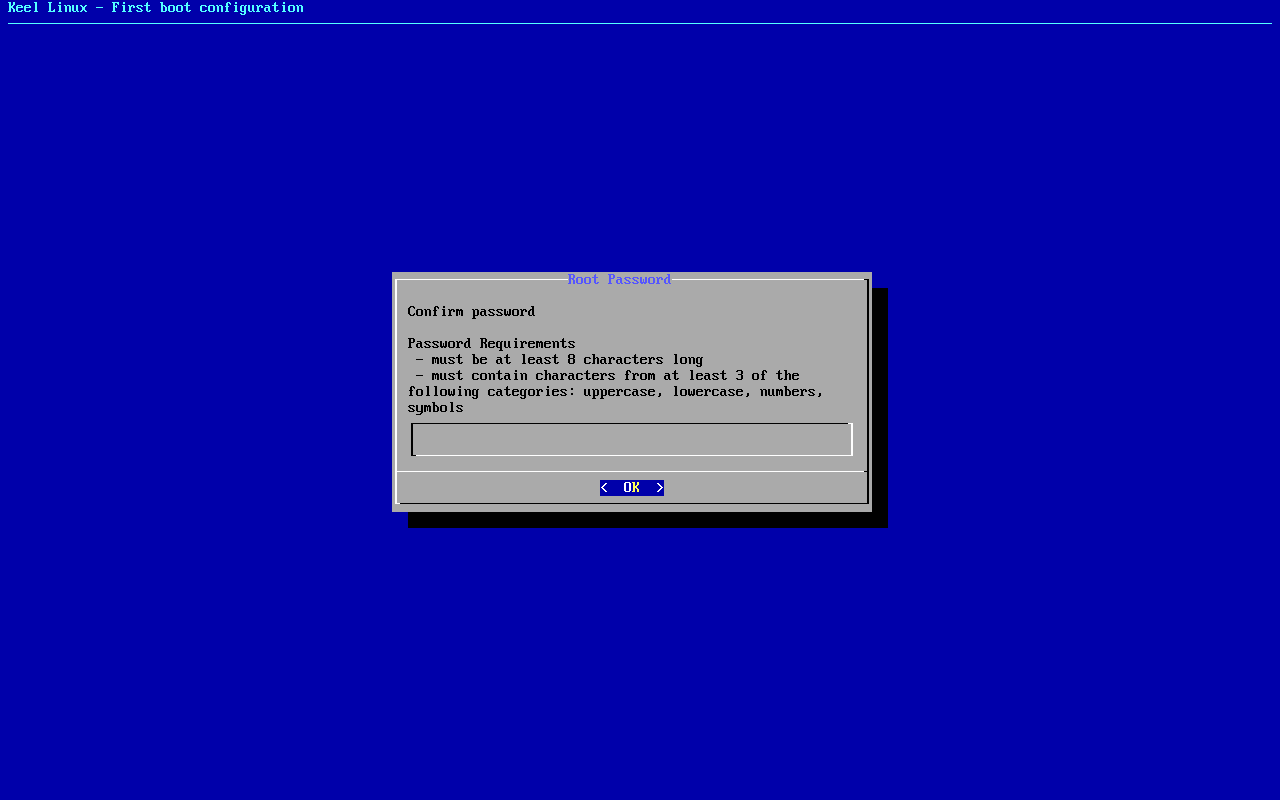
typed:
(the root secret)<ret> - 14
firstboot-screen
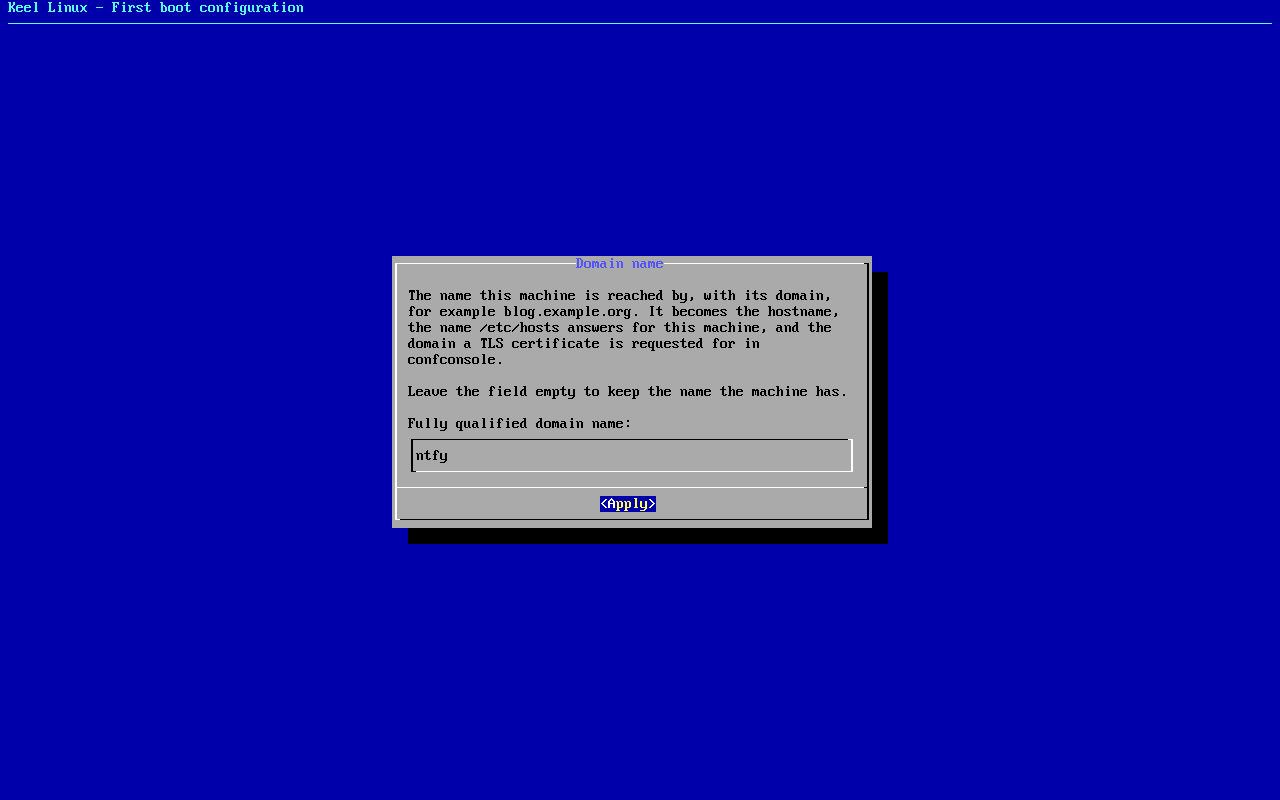
typed:
<ret> - 15
firstboot-screen
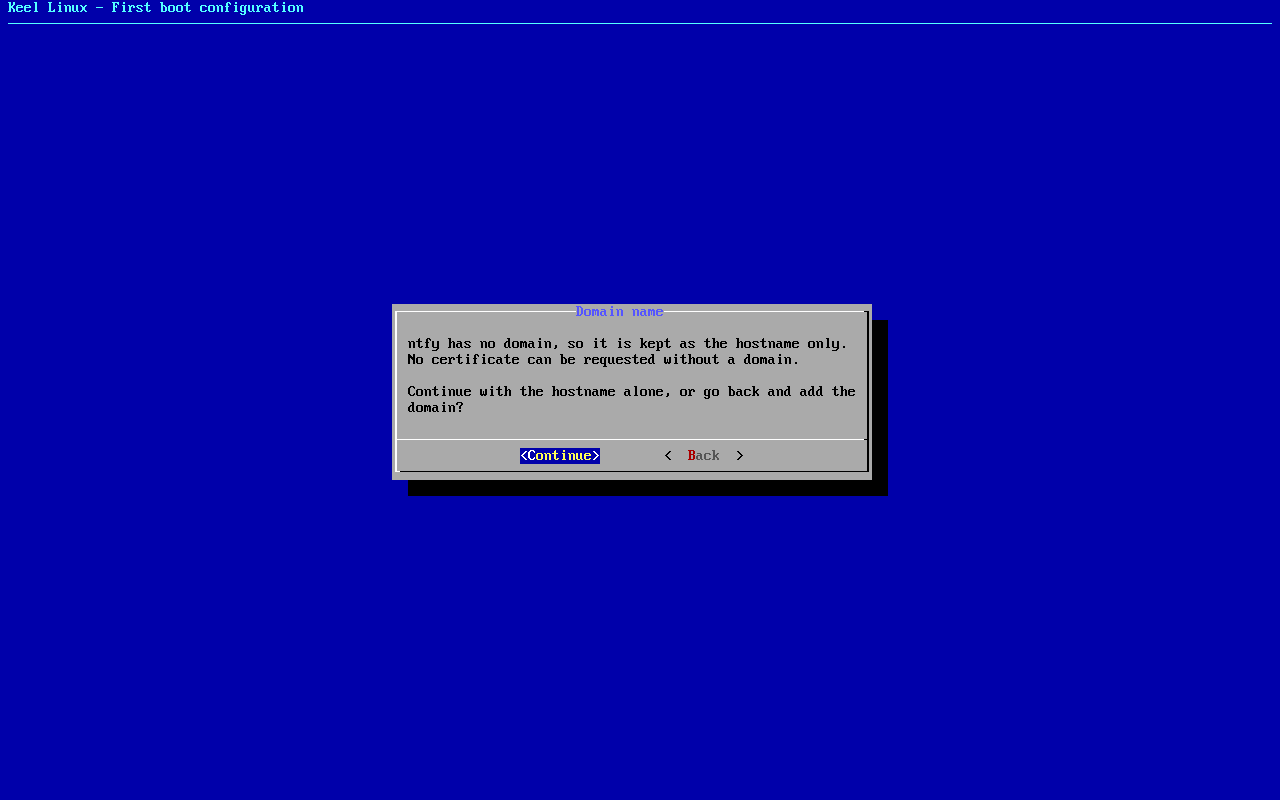
typed:
<ret> - 16
ntfy domain
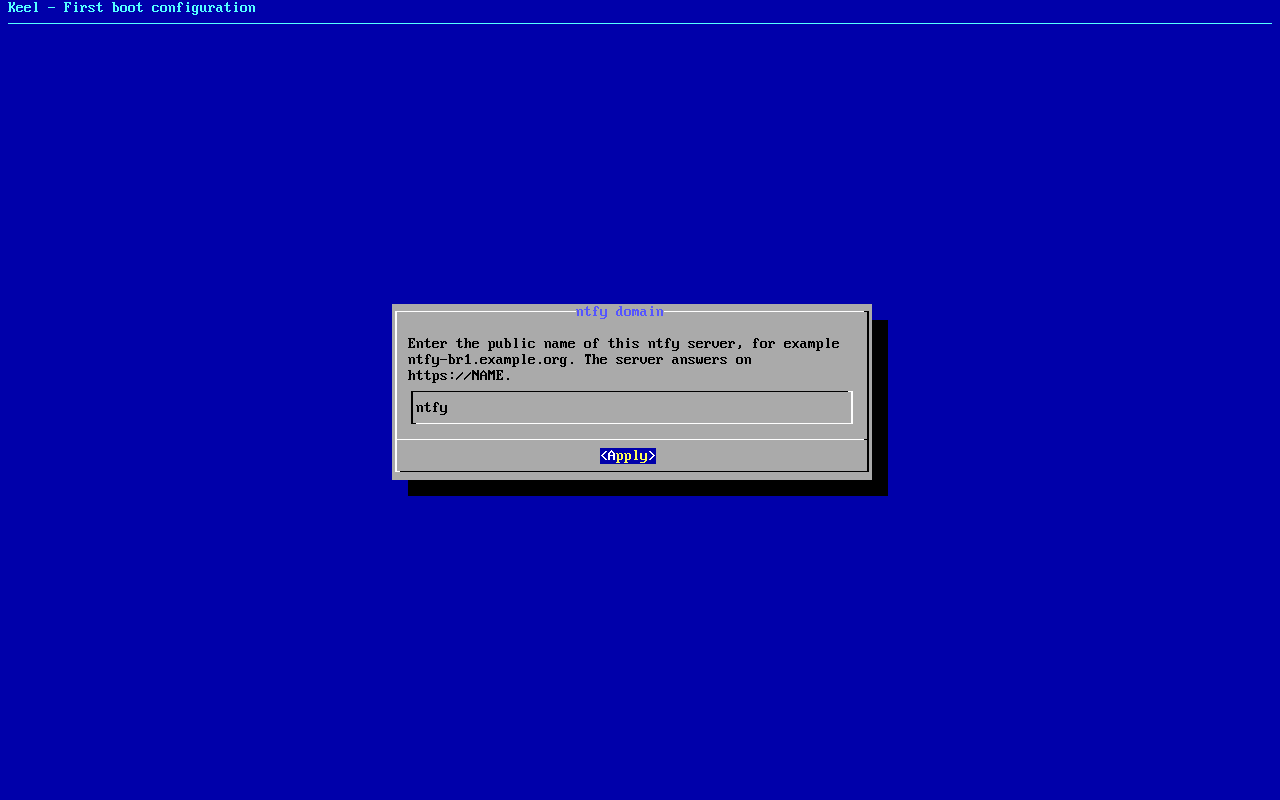
typed:
ntfy.example.org<ret> - 17
ntfy password-menu
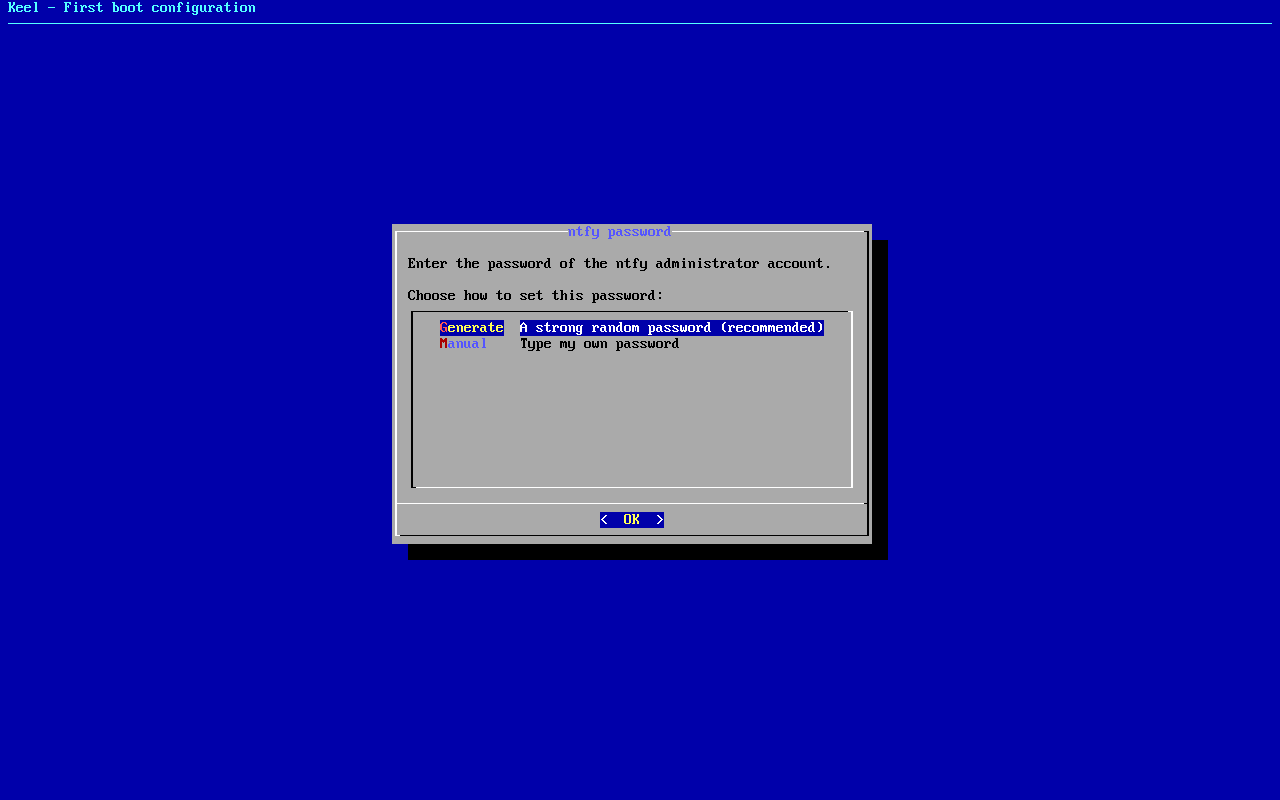
typed:
m<ret> - 18
ntfy password
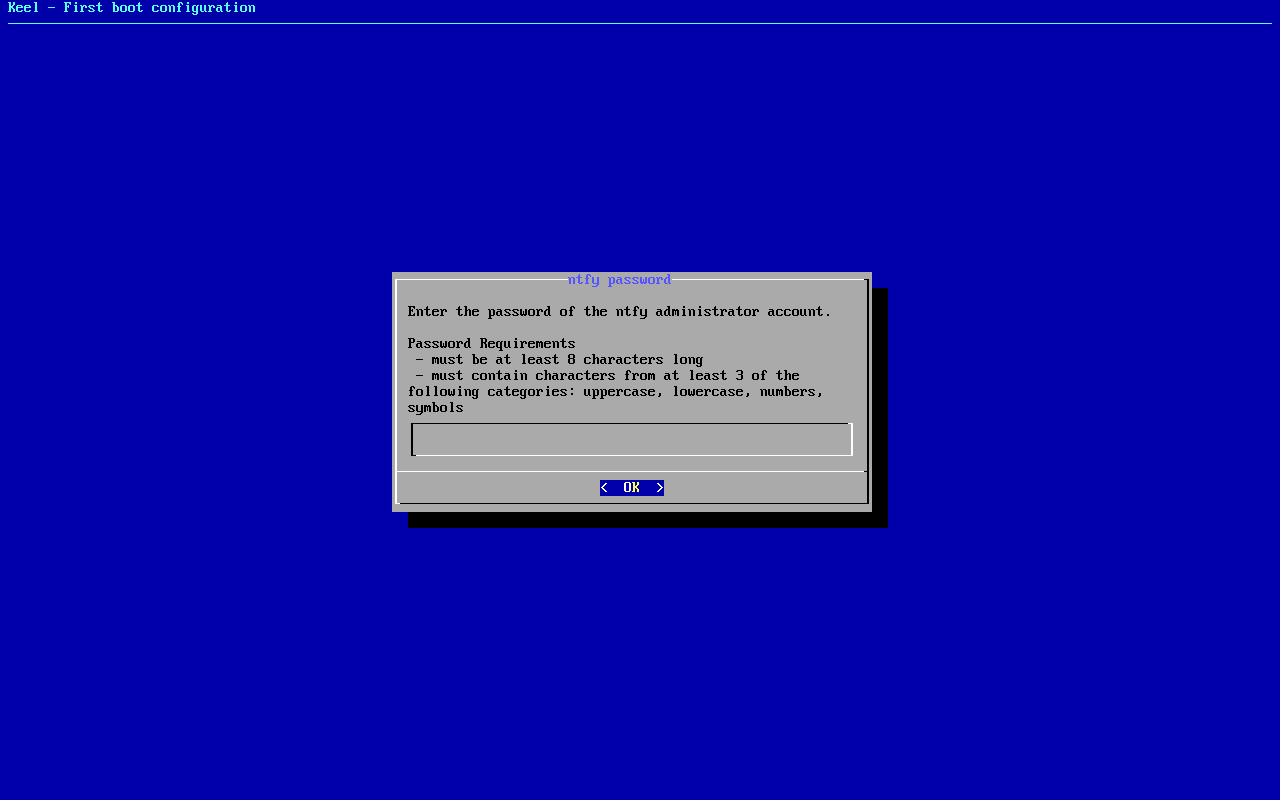
typed:
(the app secret)<ret> - 19
ntfy password
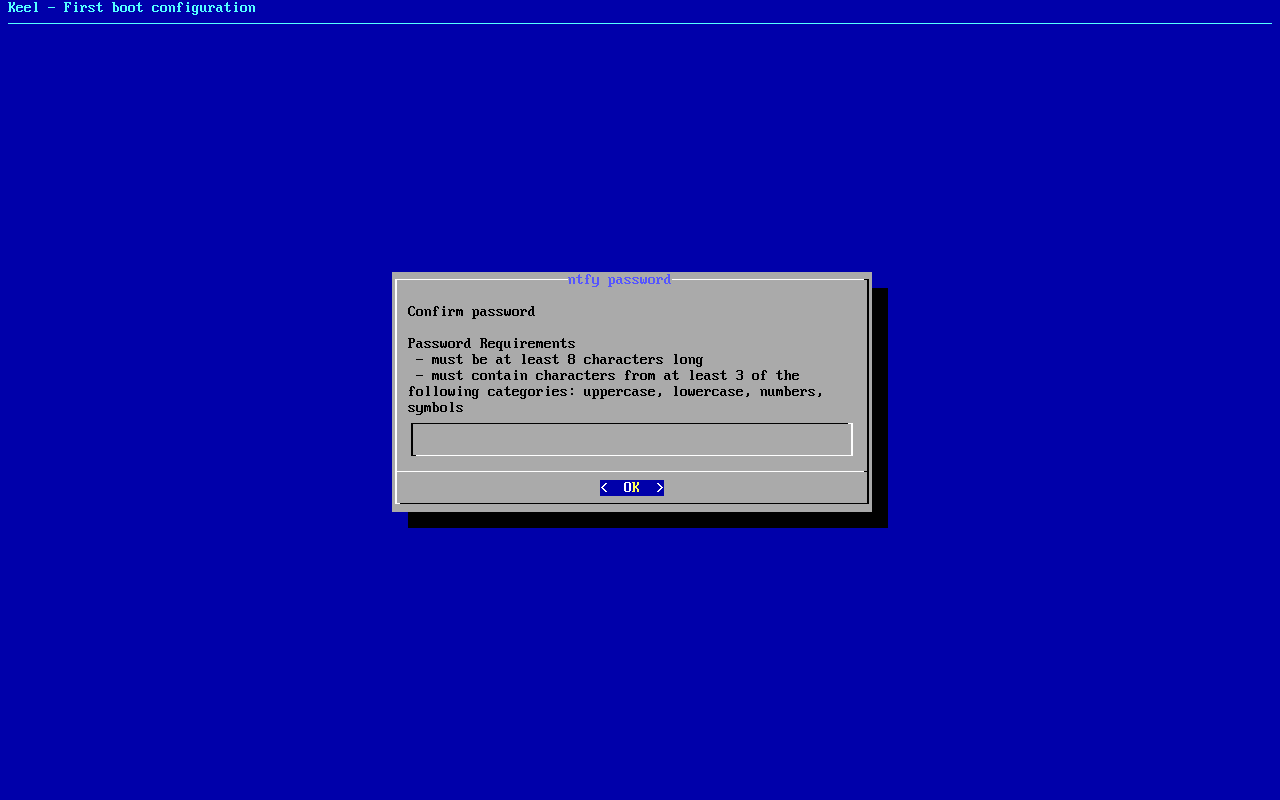
typed:
(the app secret)<ret> - 20
alert email
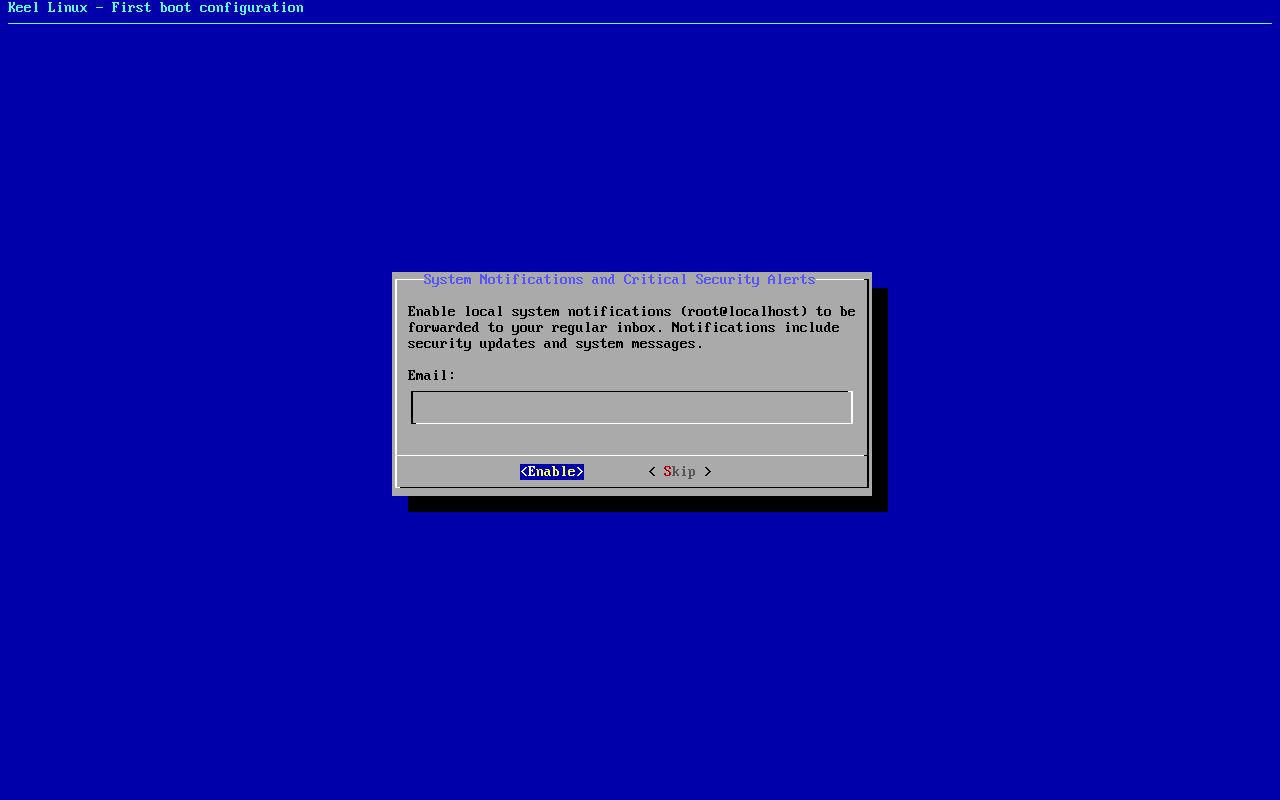
typed:
admin@example.org<ret> - 21
firstboot-screen
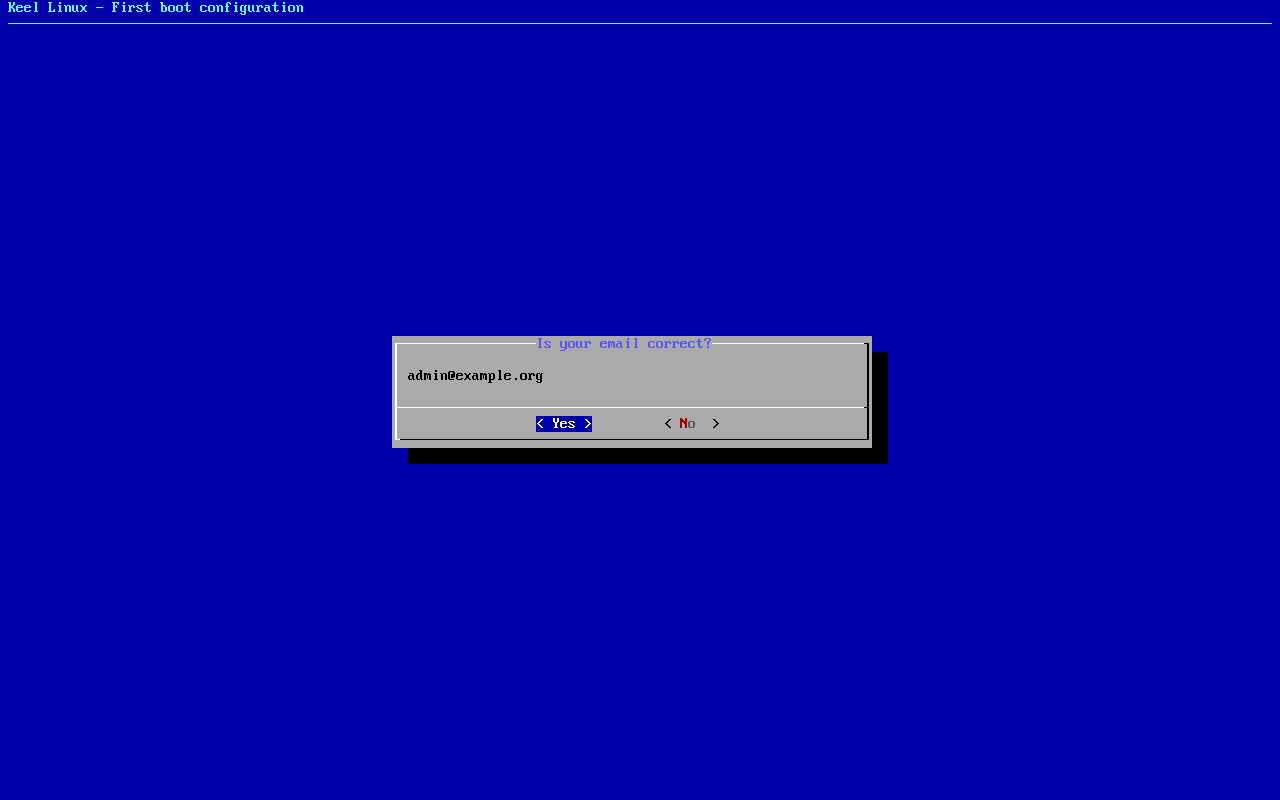
typed:
<ret> - 22
firstboot-screen
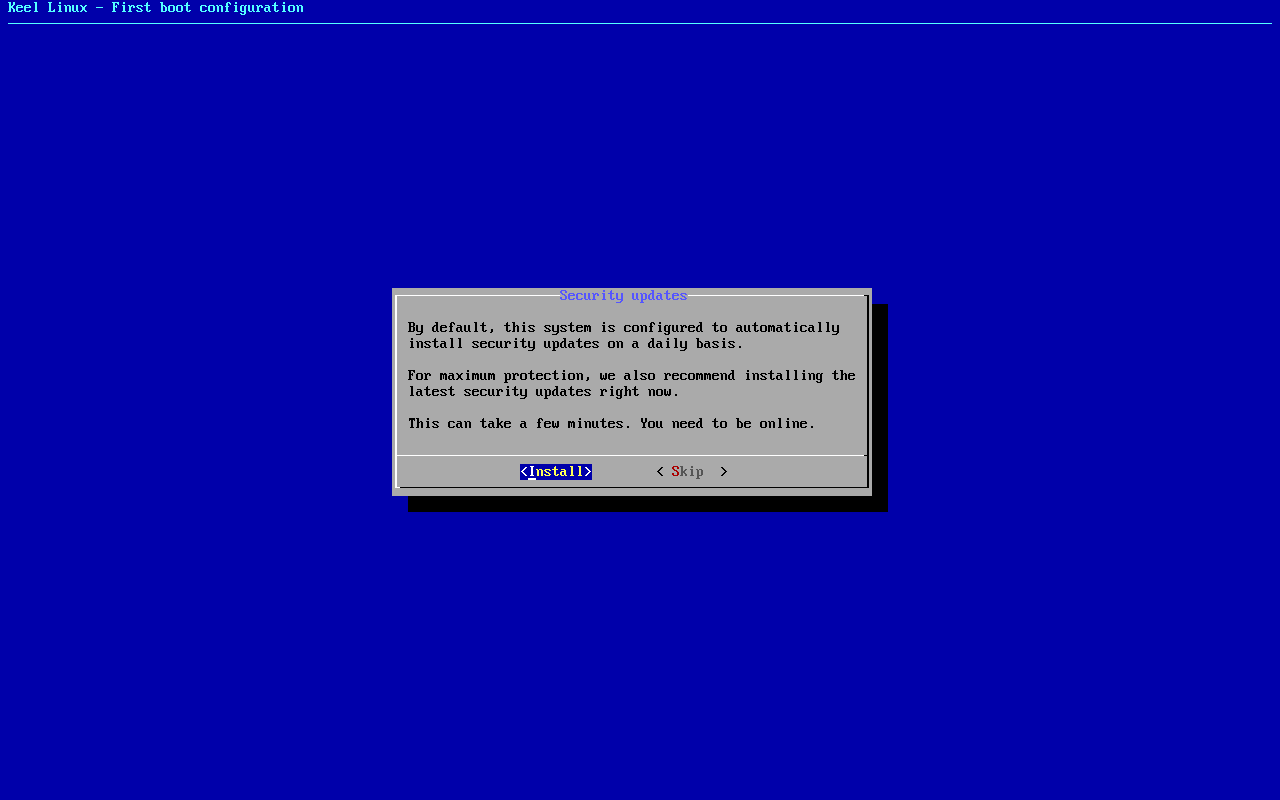
typed:
<ret> - 23
firstboot-end
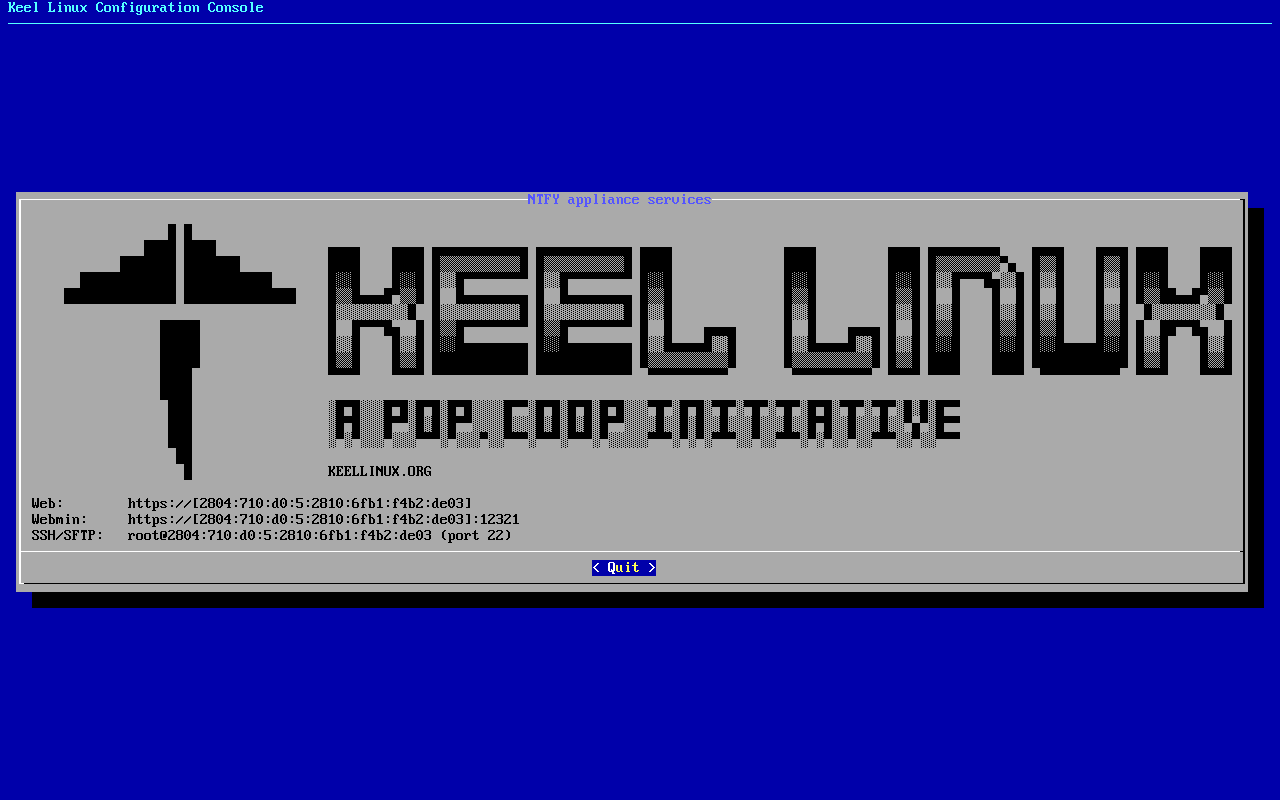
- 24
web: health
typed:
open /v1/health - 25
web: webmin
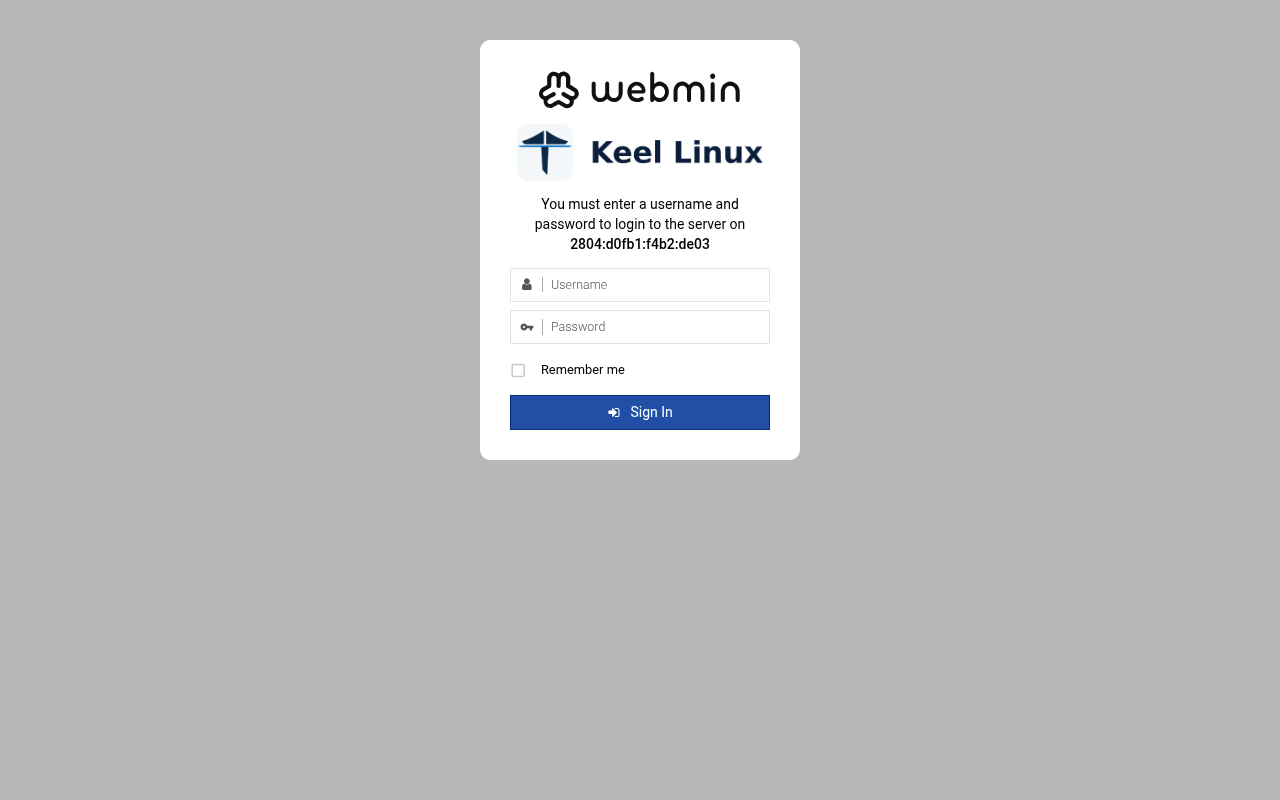
typed:
user root, the root secret - 26
web: webmin-after
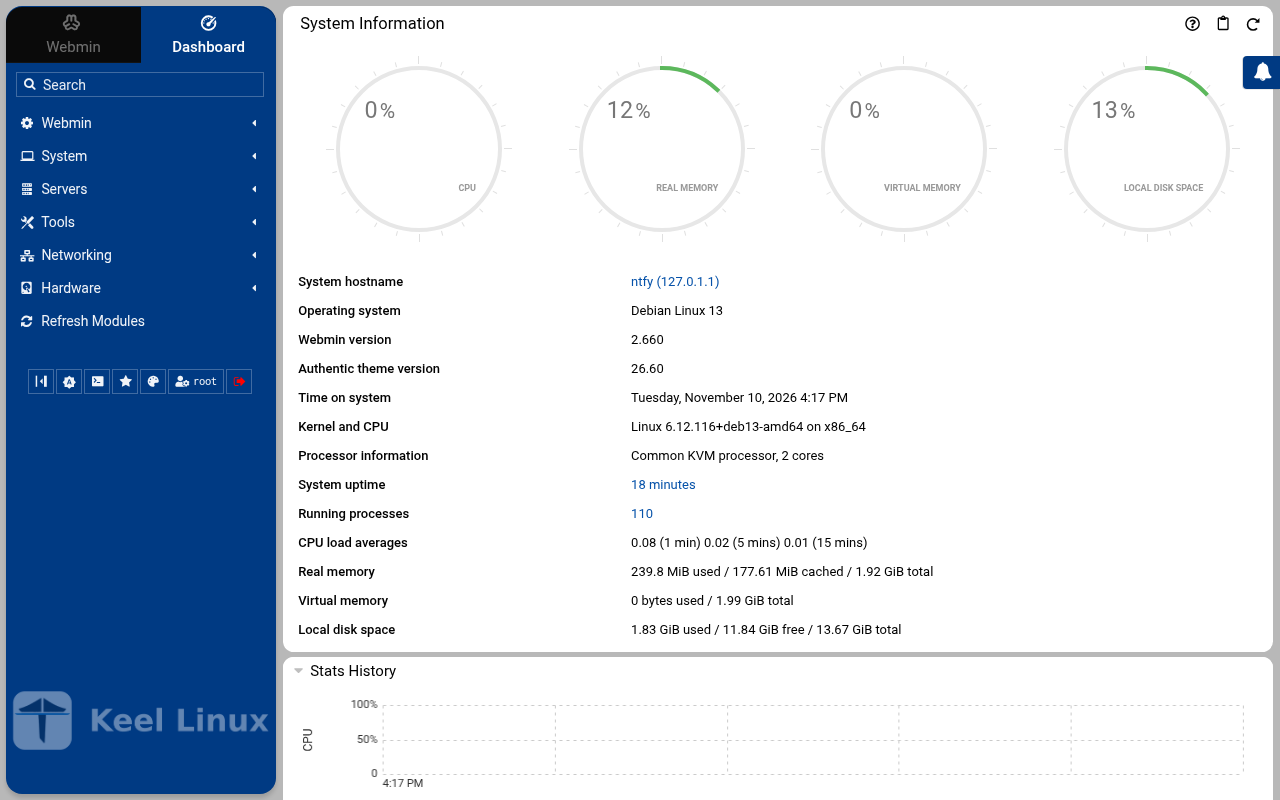
typed:
after the login: the page the login opened
Commissioning
6 passes on the sites BR1, BR2, 2026-11-10: 246 checks, all passed.
Every pass below passed every check (decision 0075). A page never shows an image that did not pass.
| Pass | Nodes | Date | Checks passed |
|---|---|---|---|
| the LXC template, answered on the console | br1 | 2026-11-10T15:54:14Z | 41 of 41 |
| the LXC template, described before the boot | br1 | 2026-11-10T16:08:14Z | 37 of 37 |
| the ISO in a virtual machine | br1 | 2026-11-10T15:54:22Z | 45 of 45 |
| the LXC template, answered on the console | br2 | 2026-11-10T15:54:18Z | 41 of 41 |
| the LXC template, described before the boot | br2 | 2026-11-10T16:08:31Z | 37 of 37 |
| the ISO in a virtual machine | br2 | 2026-11-10T15:54:23Z | 45 of 45 |