Appliances / Keel Web
Keel WebNginx of Debian 13, Coraza and Anubis
Keel release 19.0-13 · image debian-13-keel-web_19.0-13_amd64.tar.zst
Keel Web is the appliance of Keel Linux that serves the web: Nginx, Coraza (a WAF inside Nginx, with the OWASP Core Rule Set) and Anubis (proof of work, behind Nginx). It is built as a layer on Keel Core and is the base of every Keel web appliance (handbook decisions 0030, 0036 and 0041).
Install
LXC template, for Proxmox VE
debian-13-keel-web_19.0-13_amd64.tar.zst
sha256 c9851497f84af8b9d9980c8011faff2cb43dc01ebcad451e44a180dc834a9ffb
With the Keel index
keel-pve gets the signed index of the Keel templates and checks the template against it. The Templates dialog of the Proxmox web interface does not show Keel templates. Install keel-pve from the Keel archive, suite trixie-testing, as its README says. Then run these commands on the Proxmox node:
keel-pve update
keel-pve download local keel-web
With the file
- Download the template, its
.sha512and its.sha512.asc. - Check the signature. Then check the digest.
- Copy the template to
/var/lib/vz/template/cache/on the Proxmox node.
curl -fLO https://mirror.keellinux.org/images/debian-13-keel-web_19.0-13_amd64.tar.zst -O https://mirror.keellinux.org/images/debian-13-keel-web_19.0-13_amd64.tar.zst.sha512 -O https://mirror.keellinux.org/images/debian-13-keel-web_19.0-13_amd64.tar.zst.sha512.asc
curl -fLO https://archive.keellinux.org/keel-images-keyring.asc
sqv --keyring keel-images-keyring.asc debian-13-keel-web_19.0-13_amd64.tar.zst.sha512.asc debian-13-keel-web_19.0-13_amd64.tar.zst.sha512
sha512sum -c debian-13-keel-web_19.0-13_amd64.tar.zst.sha512
cp debian-13-keel-web_19.0-13_amd64.tar.zst /var/lib/vz/template/cache/
If sqv prints E71DB9C3CA6AC18075395CC3ED3A709C4F3E2F3C, the signature is good. It also prints "Missing key" for the main key of the project. This is expected.
Make the container
pct create 200 local:vztmpl/debian-13-keel-web_19.0-13_amd64.tar.zst --hostname web \
  --unprivileged 1 --features nesting=1 \
  --net0 name=eth0,bridge=vmbr0,ip6=auto
Start the container and log in on its console as root. The first boot asks its questions there.
ISO, for a virtual or a real machine
debian-13-keel-web_19.0-13_amd64.iso
sha256 abdfeffd2ec7b02527c95208255c07d13eb8b8da6f6437bd5f105f9a83b7163b
curl -fLO https://mirror.keellinux.org/images/debian-13-keel-web_19.0-13_amd64.iso -O https://mirror.keellinux.org/images/debian-13-keel-web_19.0-13_amd64.iso.sha512 -O https://mirror.keellinux.org/images/debian-13-keel-web_19.0-13_amd64.iso.sha512.asc
curl -fLO https://archive.keellinux.org/keel-images-keyring.asc
sqv --keyring keel-images-keyring.asc debian-13-keel-web_19.0-13_amd64.iso.sha512.asc debian-13-keel-web_19.0-13_amd64.iso.sha512
sha512sum -c debian-13-keel-web_19.0-13_amd64.iso.sha512
Boot the machine from the ISO and install. The first boot of the installed system asks the same questions as the template.
The first boot
The questions of the first boot, of all the modes and roles. A node asks only those of its mode and role (the guides below show each one):
- Root Password password
- Installation mode
- System Notifications
- Role of this node
- Invite a node
- Join a mesh
No password is copied between nodes: only the invite lines (decision 0076).
Services
nginx, ssh, webmin, postfix, cron, monit
Addresses the commissioning checked
https://127.0.0.1/http://127.0.0.1/https://127.0.0.1/keel-healthhttp://127.0.0.1/keel-healthhttps://127.0.0.1:12321/
Screenshots
open /
user root, the root secret
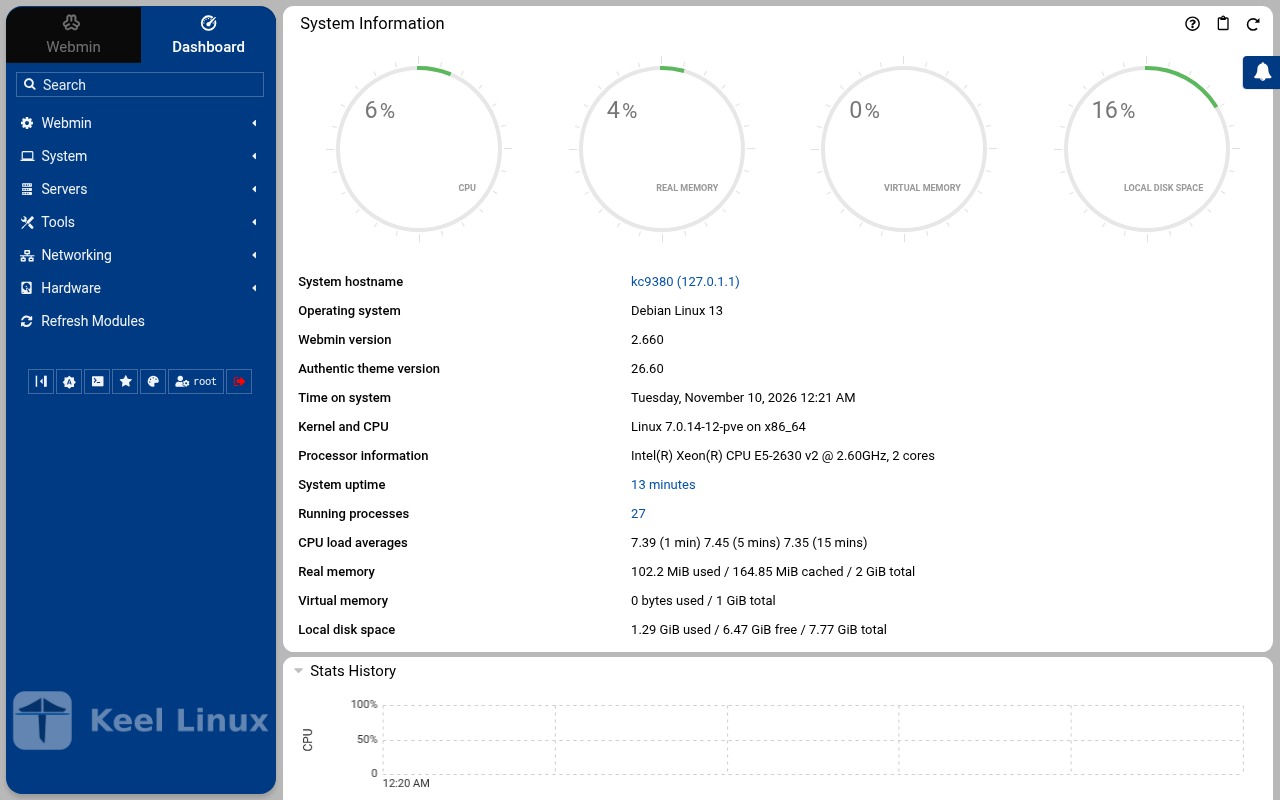
after the login: the page the login opened
Installation modes
Each column is one machine. Each row is one screen, in the order the machine showed it, with what the operator typed or chose. A secret is named, never shown.
Simple: one node
the LXC template, answered on the console (br1)
- 1
root password
the screen, as text
Connected to tty 1
Type <Ctrl+a q> to exit the console, <Ctrl+a Ctrl+a> to enter Ctrl+a itself
press Enter within 5 s to answer first-boot questions
Keel Linux Configuration Console KC9380 appliance services                                                    < Quit >         Web:https://[2804:710:d0:5:be24:11ff:fead:6360]Webmin:     https://[2804:710:d0:5:be24:11ff:fead:6360]:12321SSH/SFTP:   root@2804:710:d0:5:be24:11ff:fead:6360 (port 22) Keel Linux Configuration Console KC9380 appliance services                                  < Quit >       Web:https://[2804:710:d0:5:be24:11ff:fead:6360]Webmin:     https://[2804:710:d0:5:be24:11ff:fead:6360]:12321SSH/SFTP:   root@2804:710:d0:5:be24:11ff:fead:6360 (port 22)
Debian GNU/Linux 13 kc9380 tty1
kc9380 login: root
Password:
Keel Linux web 19.0-trixie-amd64
IPv6 Web:  https://[2804:710:d0:5:be24:11ff:fead:6360]
IPv6 SSH:  root@2804:710:d0:5:be24:11ff:fead:6360
Welcome to kc9380, Keel Linux 19.0 (Debian 13/Trixie)
System information for Tue Nov 10 00:09:24 2026 (UTC+0000)
System load:  7.94              Memory usage:  9.2%
Processes:    32                Swap usage:    0.0%
Usage of /:   11.4% of 7.78GB   Networking not configured
This system is not initialized yet: run keel-init to set it up.
For Advanced commandline config run:    confconsole
For more info see: https://github.com/Keel-Linux/confconsole
Linux kc9380 7.0.14-12-pve #1 SMP PREEMPT_DYNAMIC PMX 7.0.14-12 (2026-08-11T11:05Z) x86_64
=== Keel Linux - First boot configuration
Root Password
Please enter new password for the root account.
Choose how to set this password:
Generate  A strong random password (recommended)
Manual    Type my own password
<  OK  >Generate  A strong random password (recommended)Manual    Type my own password
Keel Linux - First boot configuration
Root Password
Please enter new password for the root account.
Password Requirements
- must be at least 8 characters long
- must contain characters from at least 3 of the
following categories: uppercase, lowercase, numbers,
symbols
<  OK  >x
typed:
(the root secret) - 2
root password
the screen, as text
********
Keel Linux - First boot configuration
Root Password
Confirm password
Password Requirements
- must be at least 8 characters long
- must contain characters from at least 3 of the
following categories: uppercase, lowercase, numbers,
symbols
<  OK  >x
typed:
(the root secret) - 3
mode
the screen, as text
********
Keel Linux - First boot configuration
kc9380.pop.coop
Domain name
xxx The name this machine is reached by, with its domain,    xx for example blog.example.org. It becomes the hostname,   xx the name /etc/hosts answers for this machine, and the    xx domain a TLS certificate is requested for in             xx confconsole.xxxx Leave the field empty to keep the name the machine has.  xxxx Fully qualified domain name:x
<Apply>x
>fqdn: /etc/keel/instance.yaml already declares the name, not written
=== Keel Linux - First boot configuration
Installation mode
How this appliance is installed (decision 0028). You choose it once.
Simple: one node. Everything is on this machine, with no mesh.
Cloud simple: two nodes, a primary and a replica on a WireGuard mesh. The data follows the primary. When the
primary stops, you promote the replica by hand.
Cloud advanced: two data nodes and a witness, three sites, etcd of three. When the primary stops, the replica
takes over by itself.
Choose the same mode on every node of the set.
Simple          one node, no mesh
Cloud simple    two nodes, failover by hand
Cloud advanced  two nodes and a witness, failover by itself
<Select>
typed:
<ret> - 4
mode
the screen, as text
Keel Linux - First boot configuration
Installation mode
<  ok  >x
/etc/keel/instance.yaml: installation.mode: simple$ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yamlapply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9380)instance.fqdn: unchanged (/etc/hosts maps kc9380 to kc9380.pop.coop)derived.monit: write /etc/keel/monit/keel-manifest.conf: 4 unit(s) and 4 probe(s) of web (mode 0600): doneoverlays.syncthing: unchanged (disabled: syncthing.service)overlays.anubis: run /usr/lib/keel/overlays/anubis/state.d/50keel-web: the overlay is disabled(/usr/lib/keel/overlays/anubis/state.d/50keel-web disabled): doneoverlays.anubis: record disabled and the hooks' digest in /var/lib/keel/overlays/anubis (mode 0644): doneoverlays.coraza: run /usr/lib/keel/overlays/coraza/state: the overlay is disabled(/usr/lib/keel/overlays/coraza/state disabled): doneoverlays.coraza: record disabled and the hooks' digest in /var/lib/keel/overlays/coraza (mode 0644): doneoverlays.vip: unchanged (disabled: keel-vip.service)overlays.crowdsec: unchanged (disabled: crowdsec.service, crowdsec-firewall-bouncer.service)overlays.etcd: unchanged (disabled: etcd.service)overlays.nginx: unchanged (enabled: nginx.service)apply --system-only: 5 change(s), 0 failedkeel apply: exit 0, the spec was applied
typed:
<ret> - 5
alert email
the screen, as text
>keelfirstboot role: no database server on this machine, so no role to record
keelfirstboot cloud: Keel Cloud is not available yet: no key is asked, and this node runs standalone. It is offered once /etc/keel/cloud-endpoint names the service.
=== Keel Linux - First boot configuration
System Notifications and Critical Security Alerts
Enable local system notifications (root@localhost) to be
forwarded to your regular inbox. Notifications include
security updates and system messages.
Email:
<Enable>        < Skip >x
typed:
admin@example.org - 6
web: site
typed:
open / - 7
web: webmin
typed:
user root, the root secret - 8
web: webmin-after
typed:
after the login: the page the login opened
the ISO in a virtual machine (br1)
- 1
installer-boot
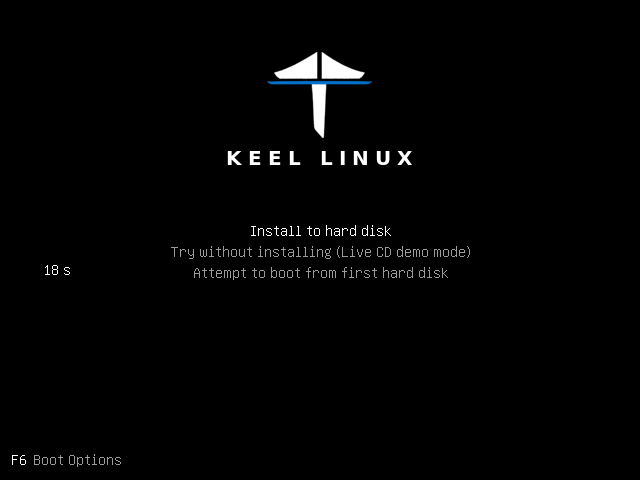
- 2
installer-boot
- 3
installer-boot
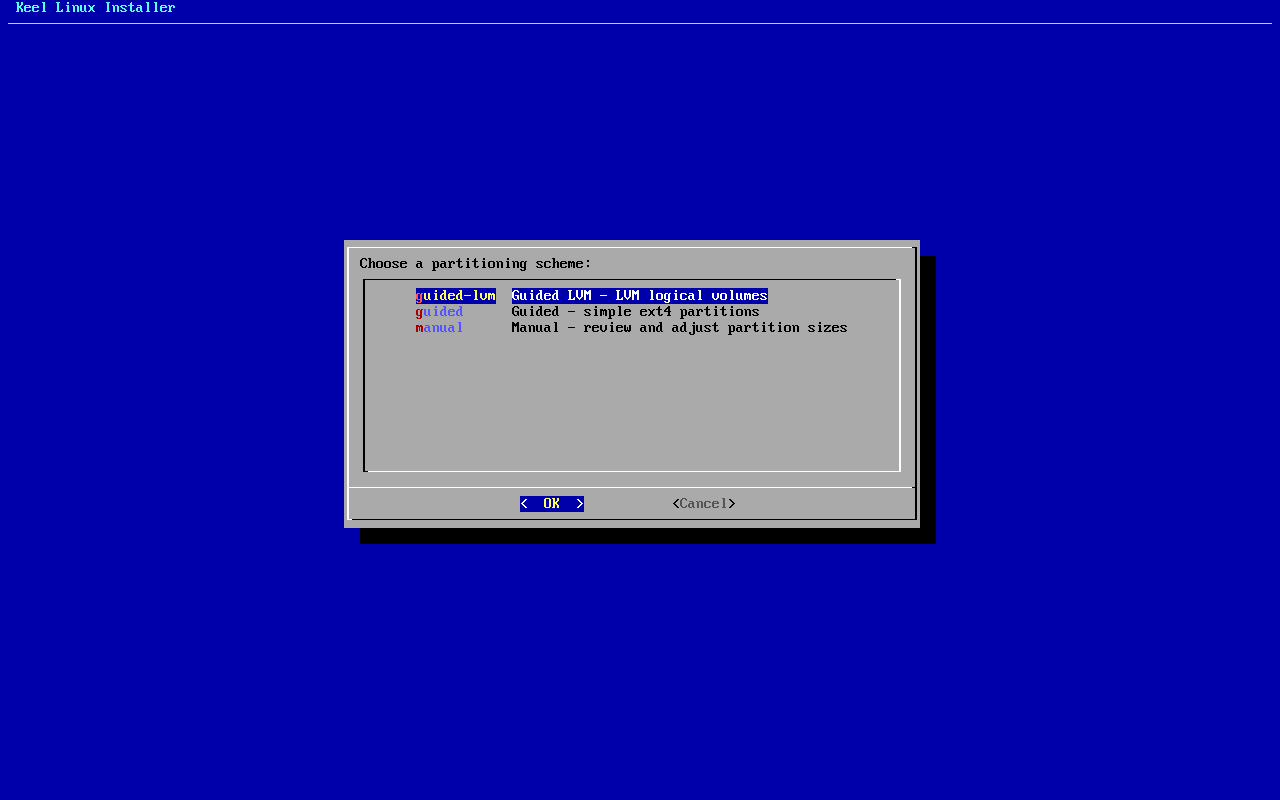
- 4
partitioning
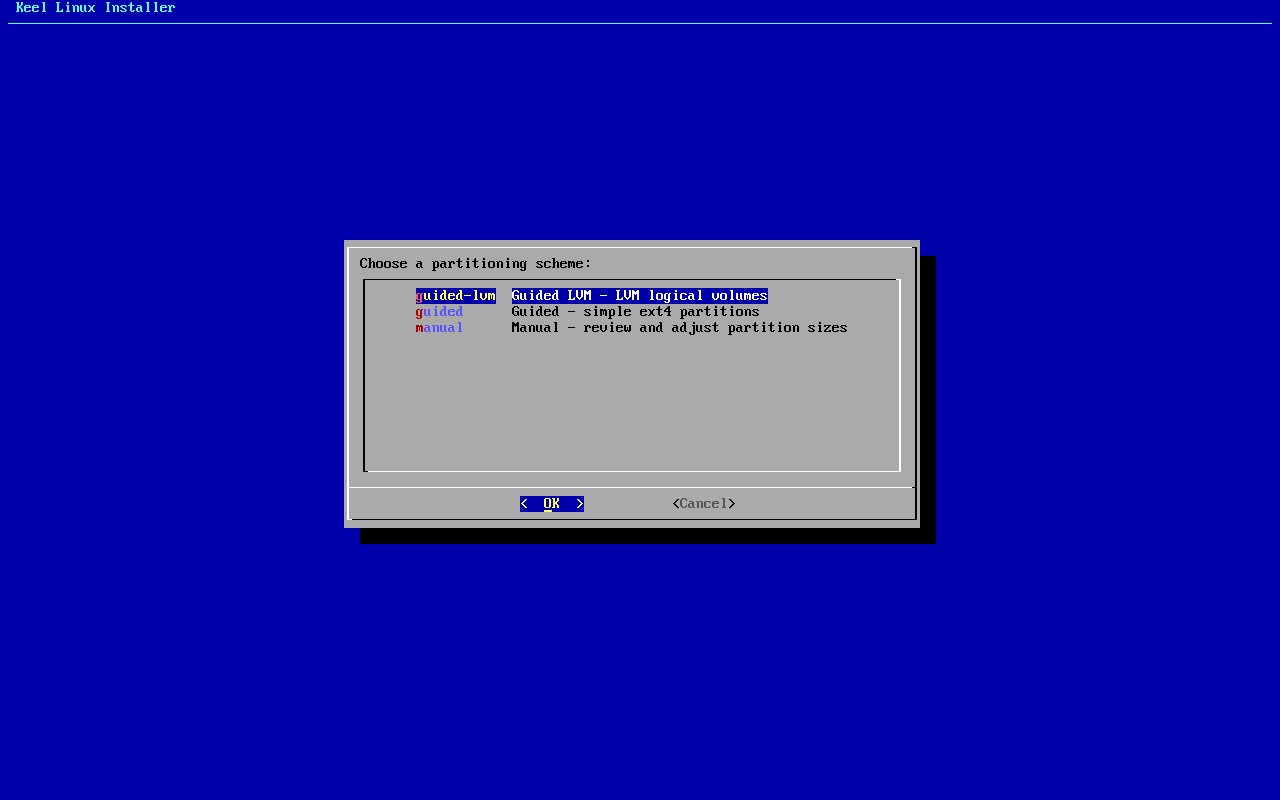
typed:
<ret> - 5
separate boot
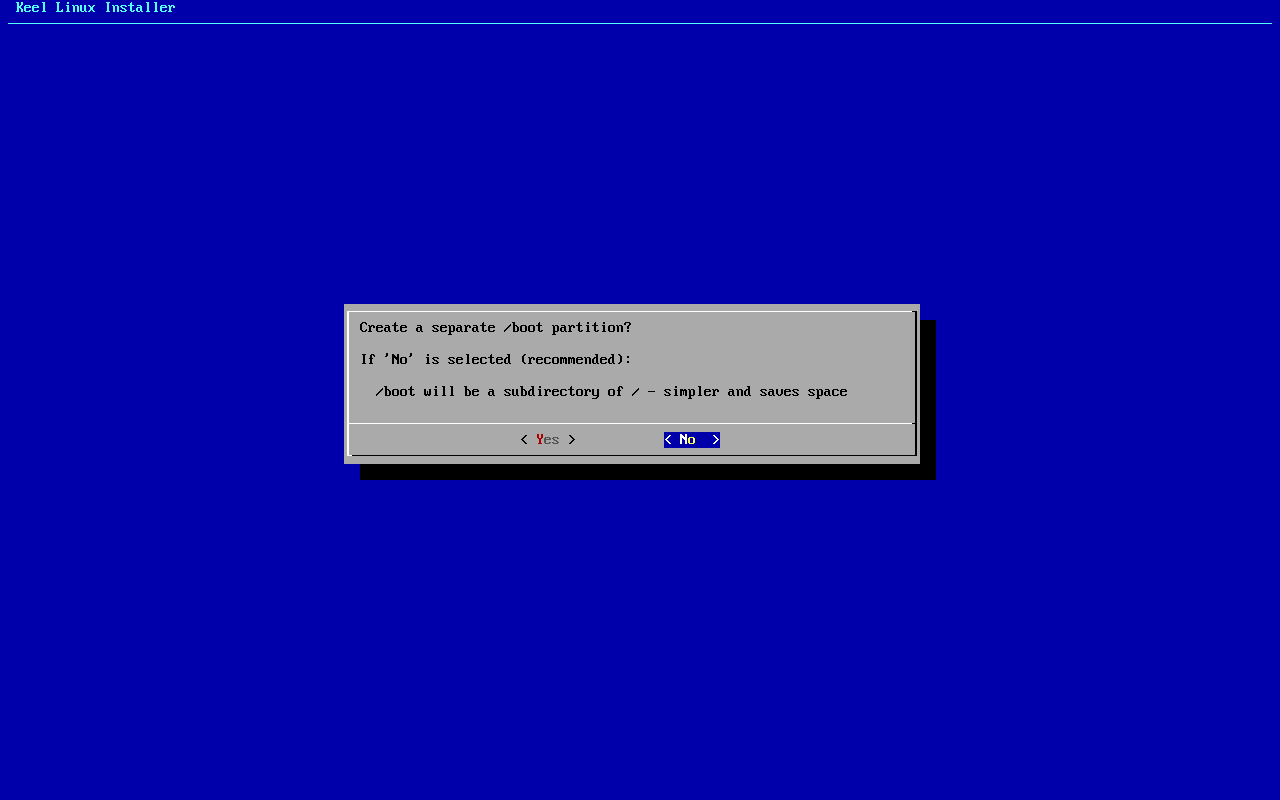
typed:
n - 6
scheme
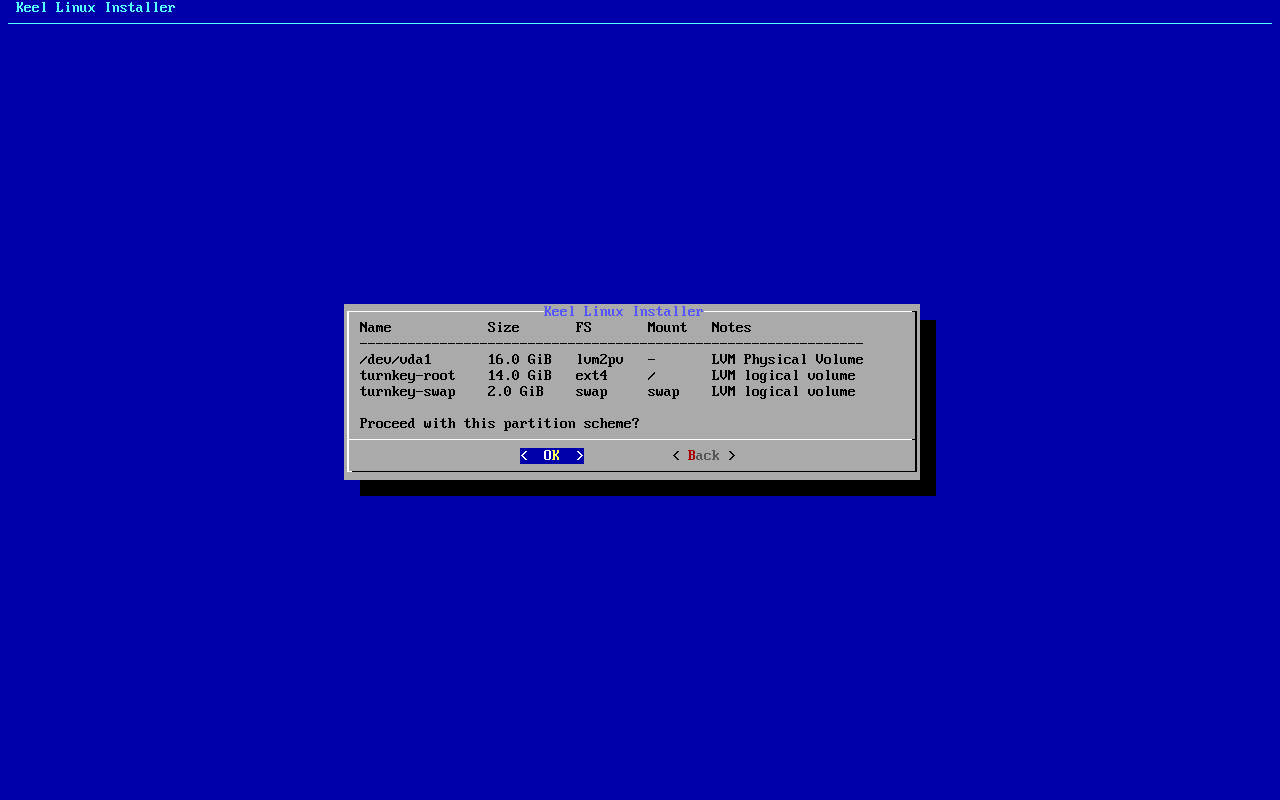
typed:
<ret> - 7
erase
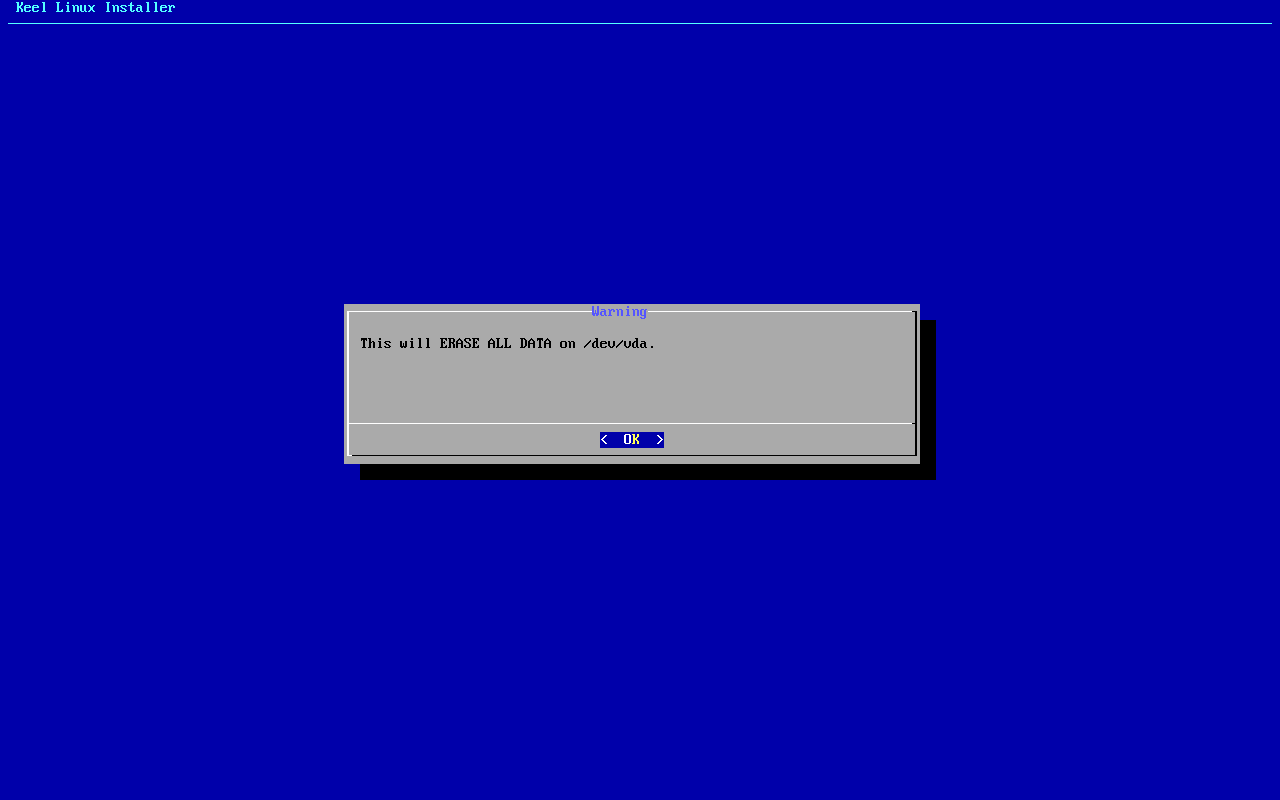
typed:
<ret> - 8
begin
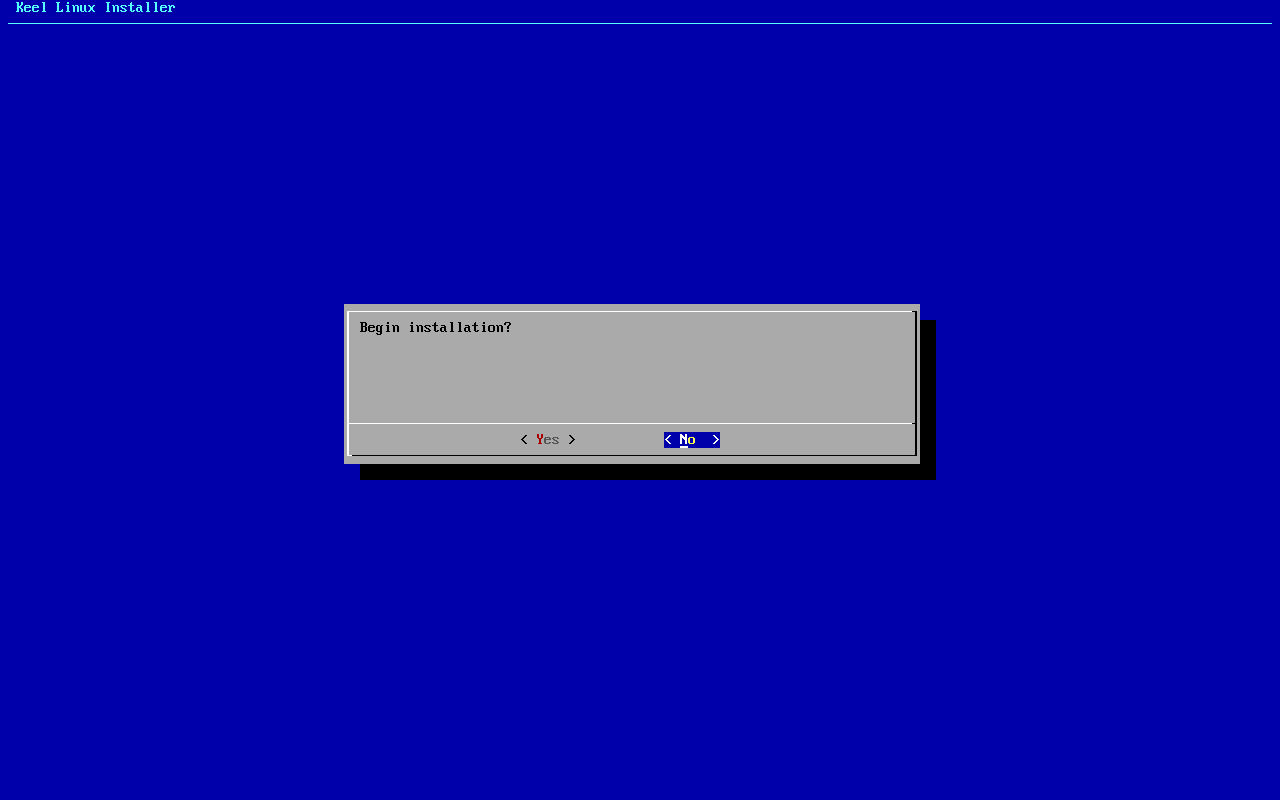
typed:
y - 9
reboot
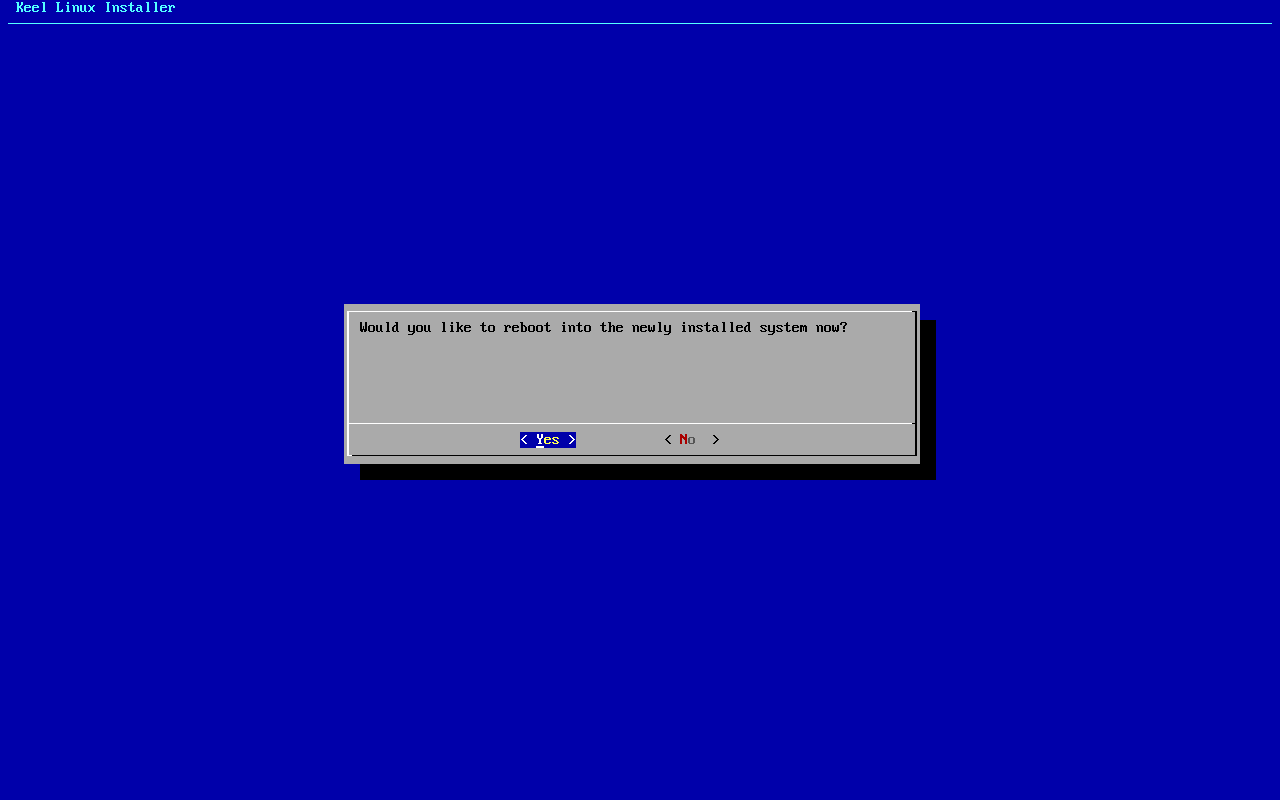
typed:
y - 10
medium
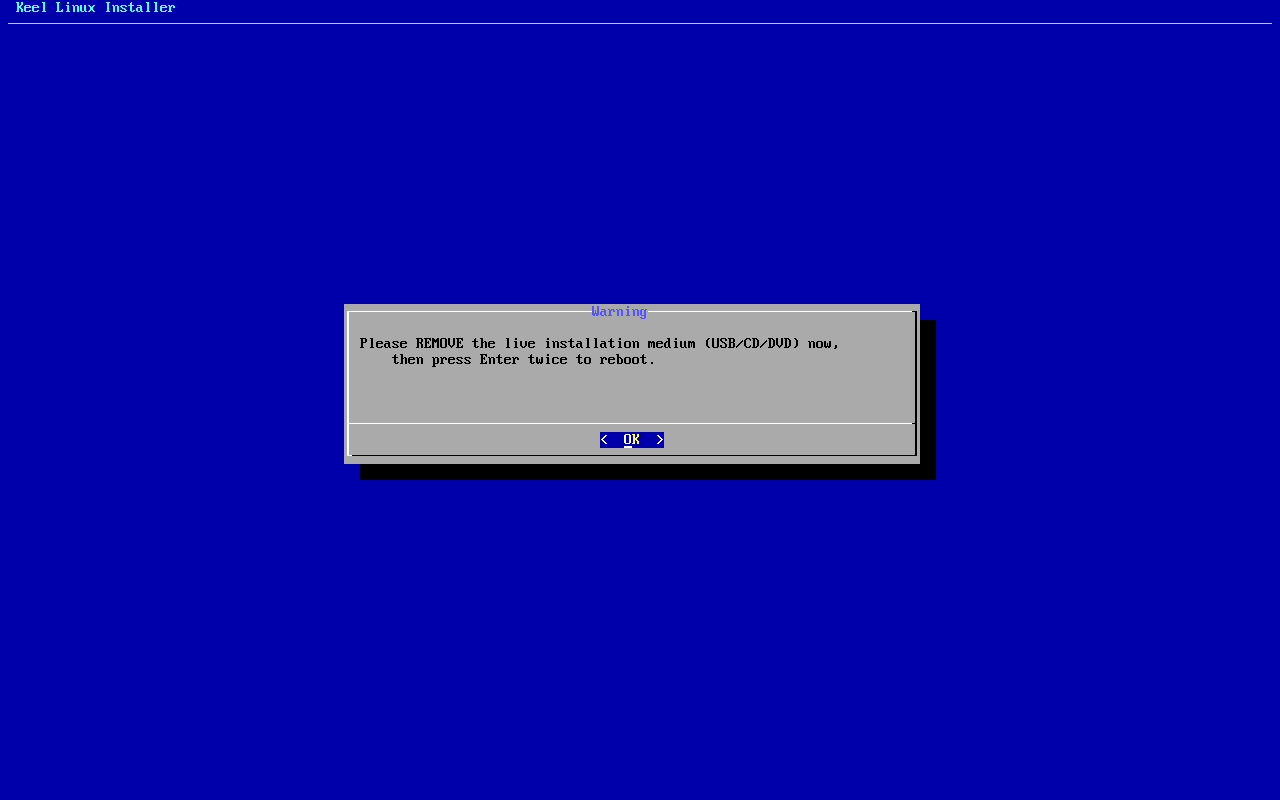
typed:
<ret><ret> - 11
root password-menu
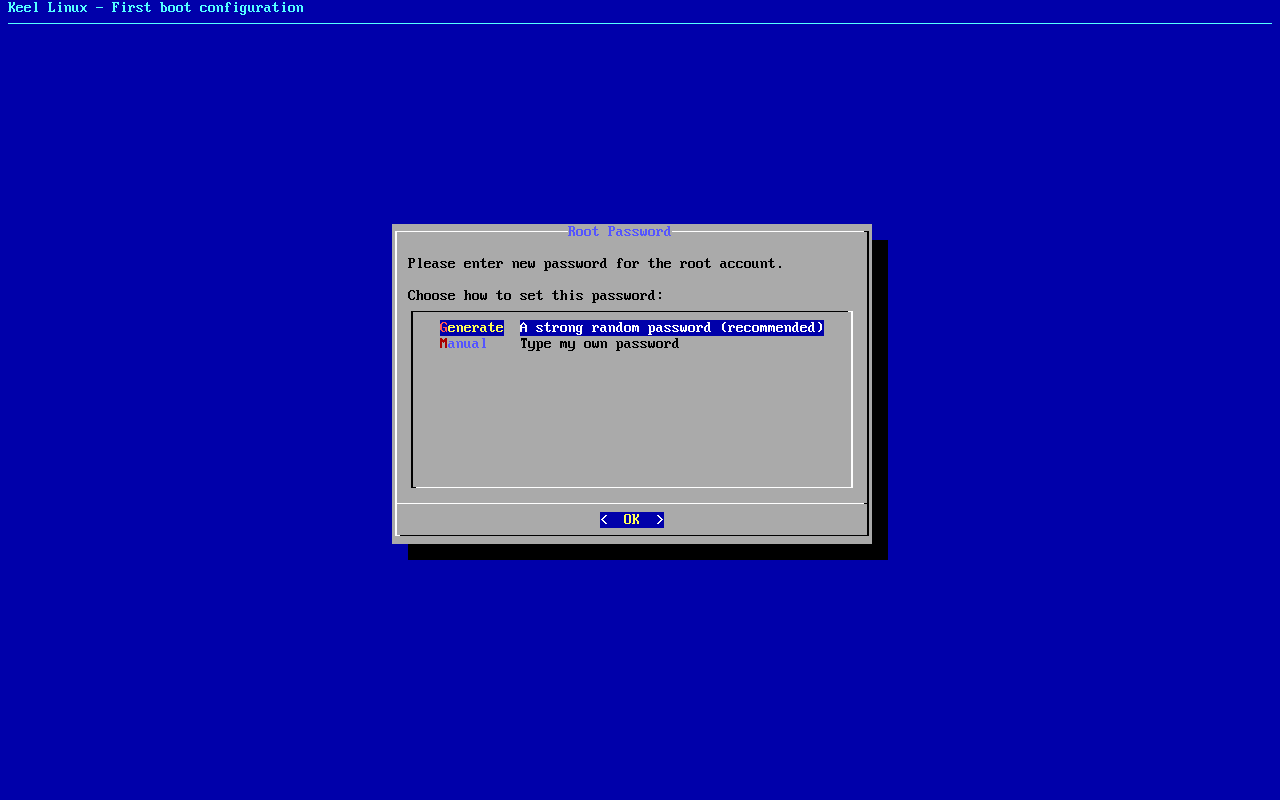
typed:
m<ret> - 12
root password
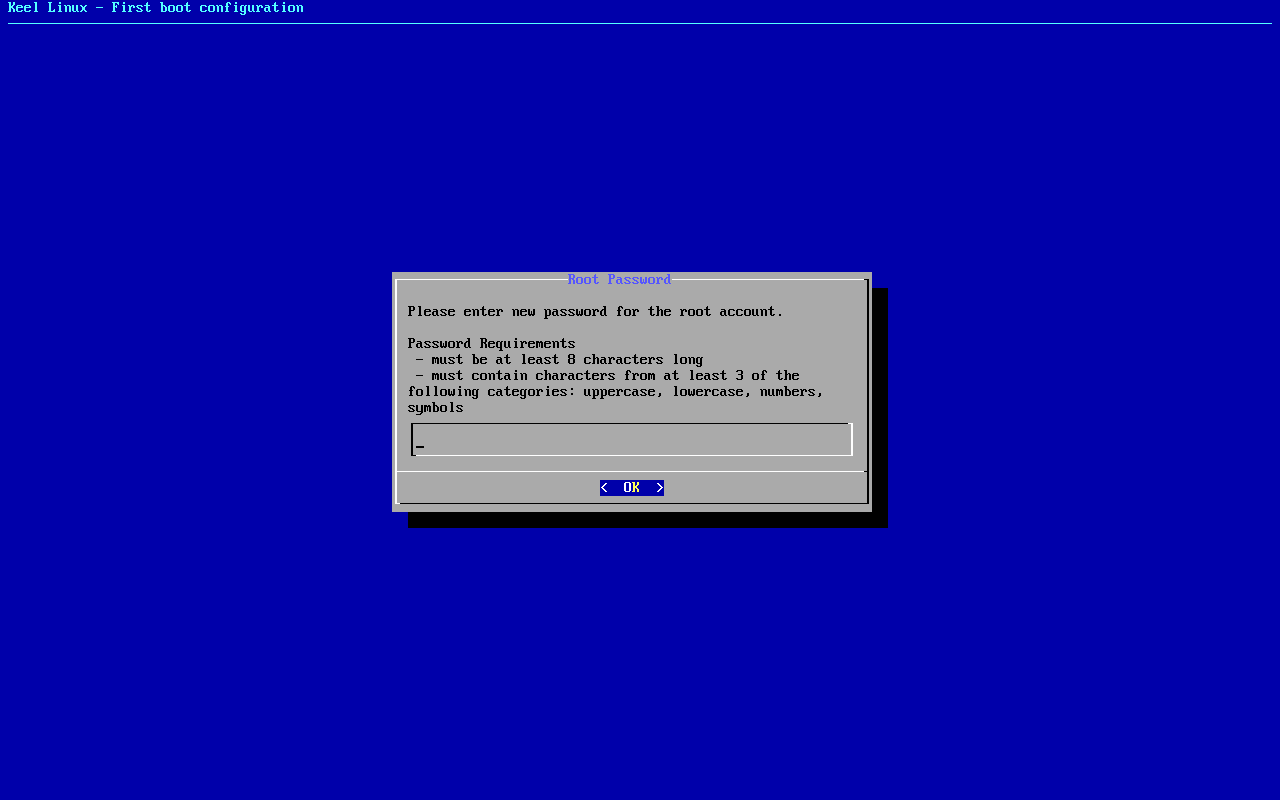
typed:
(the root secret)<ret> - 13
root password
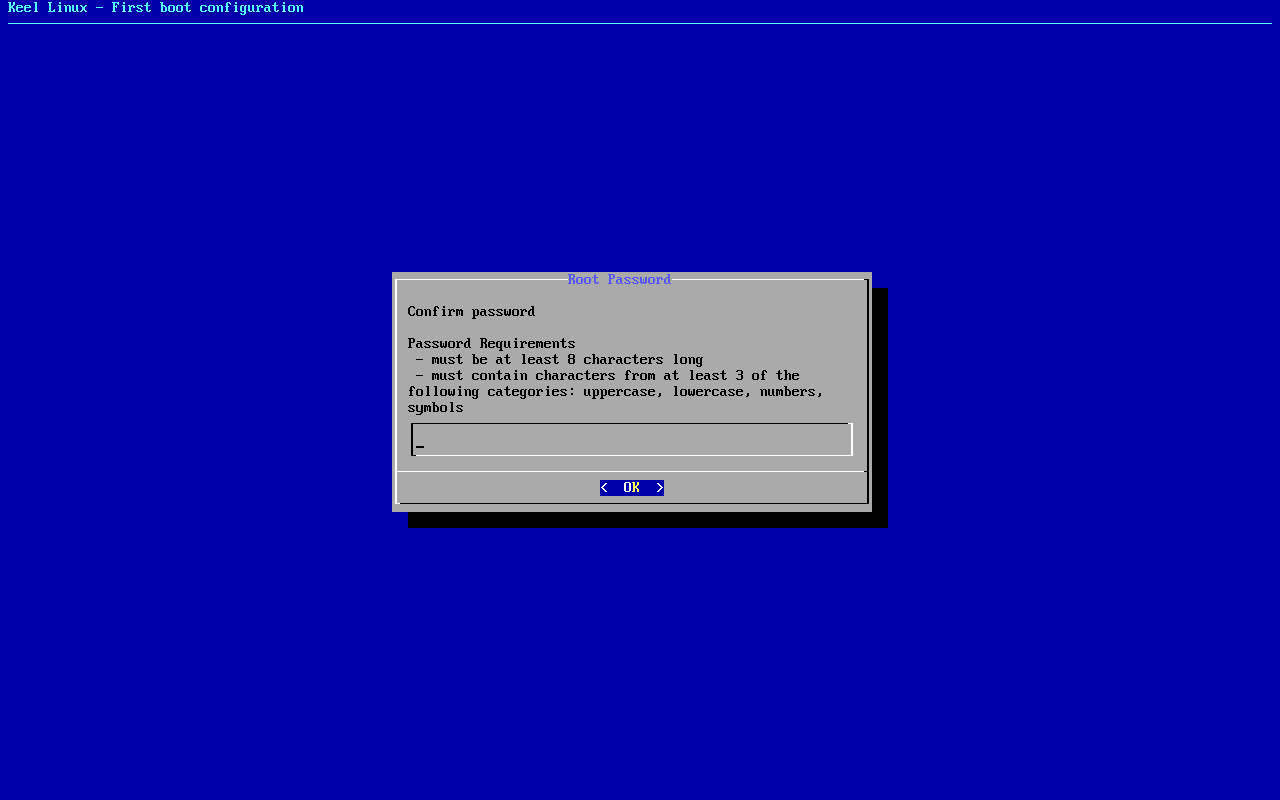
typed:
(the root secret)<ret> - 14
firstboot-screen
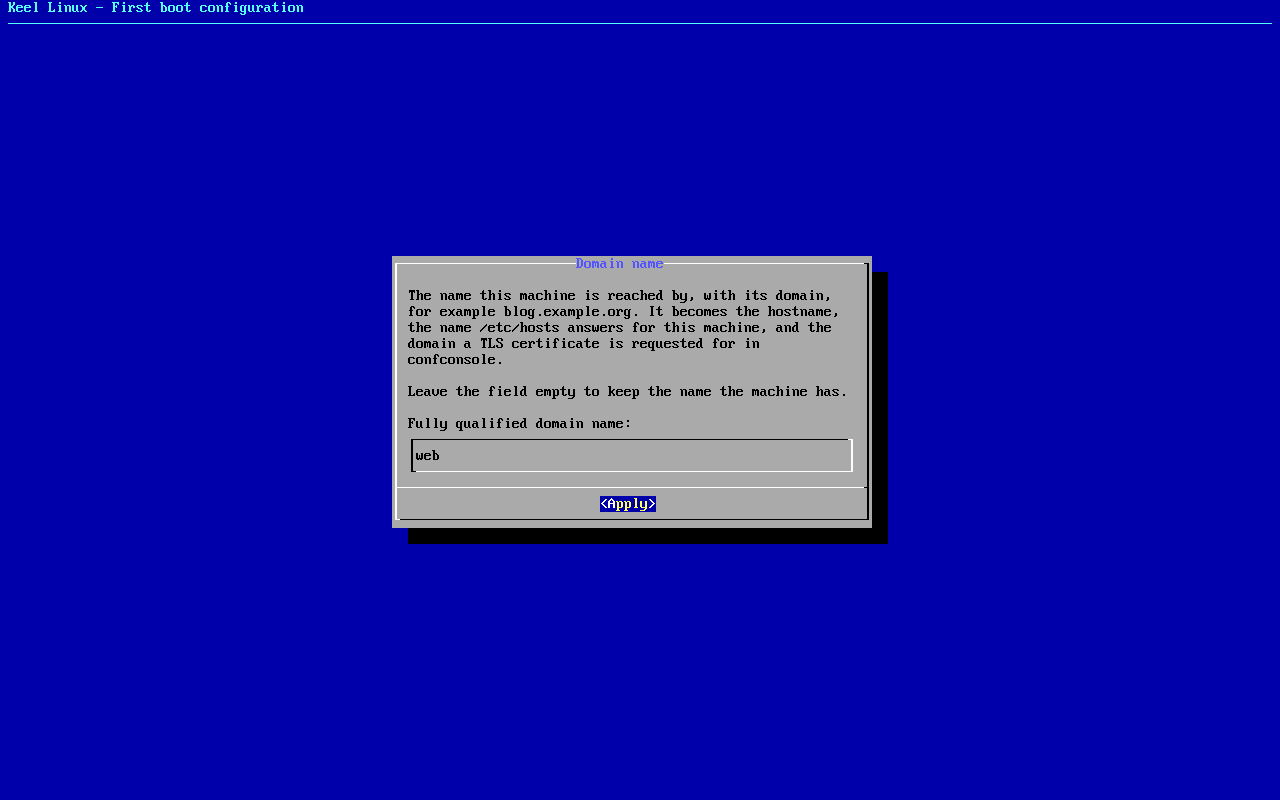
typed:
<ret> - 15
firstboot-screen
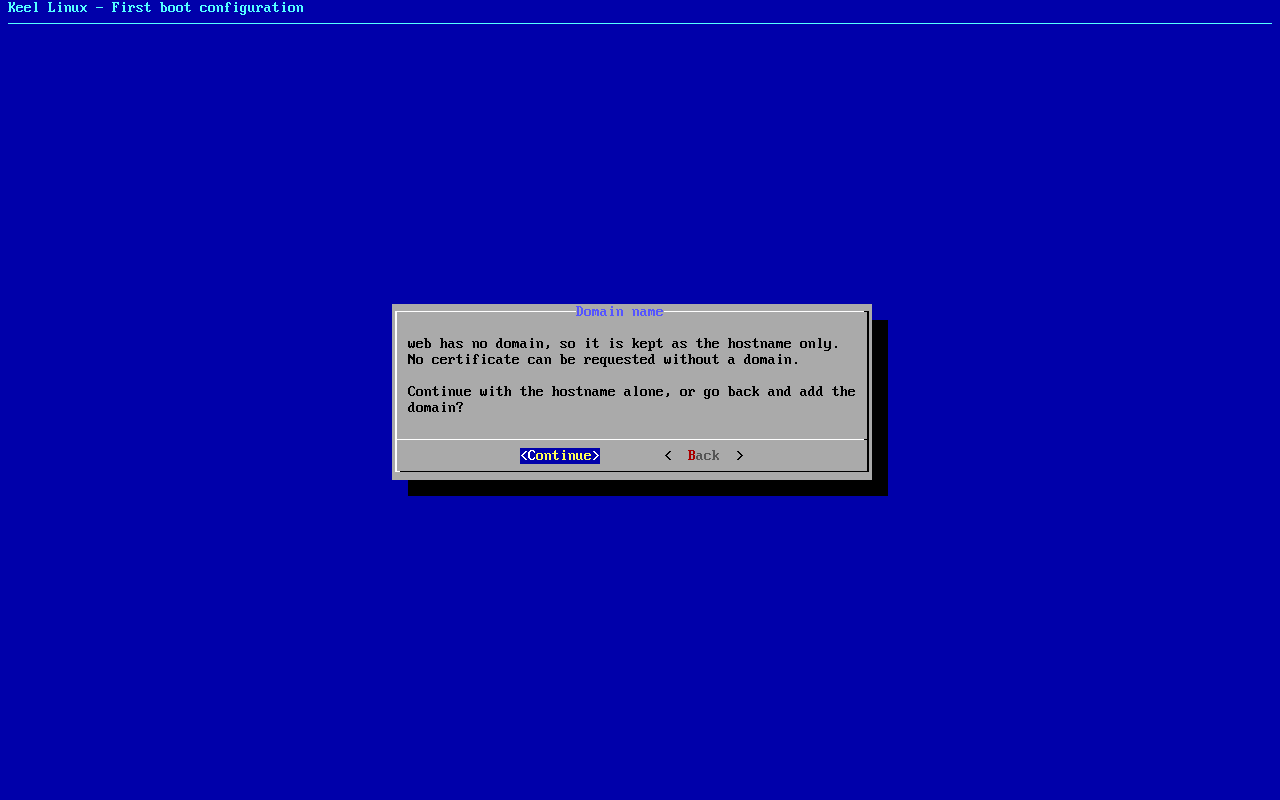
typed:
<ret> - 16
mode
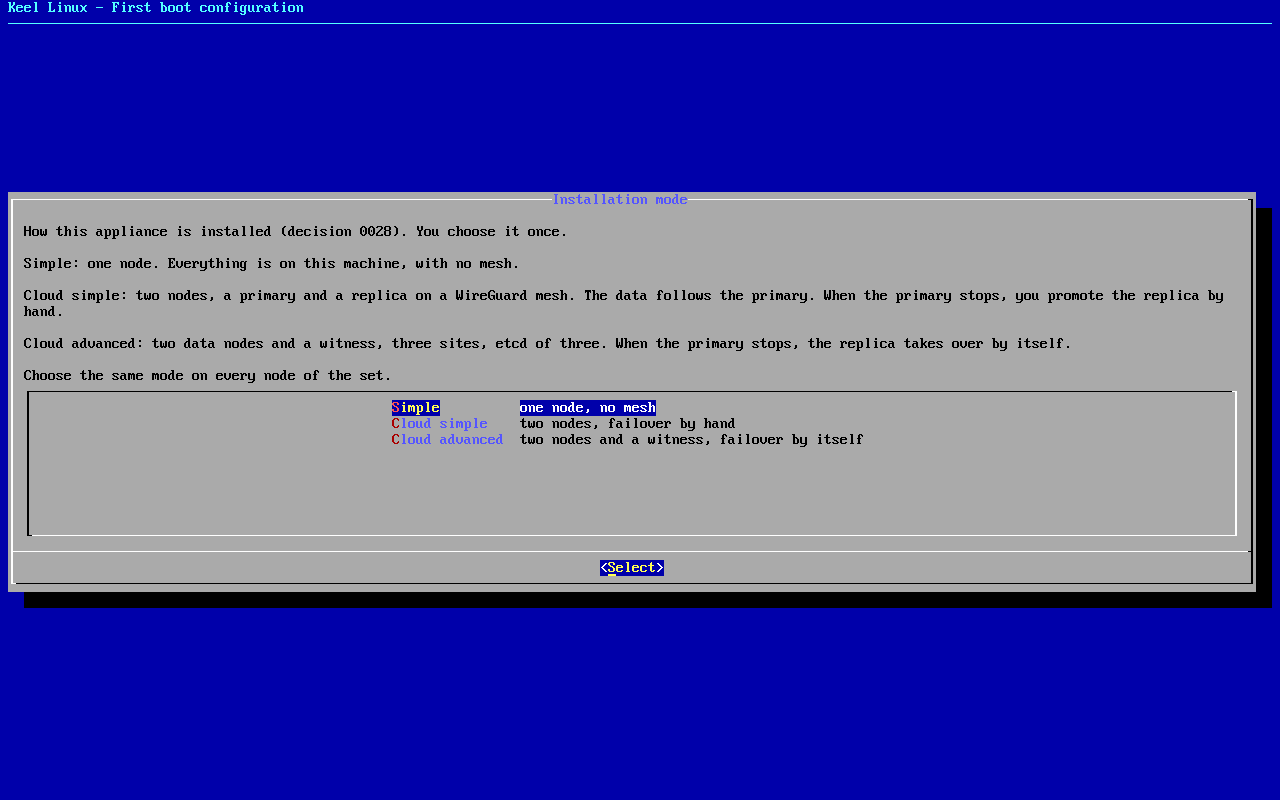
typed:
<ret> - 17
mode
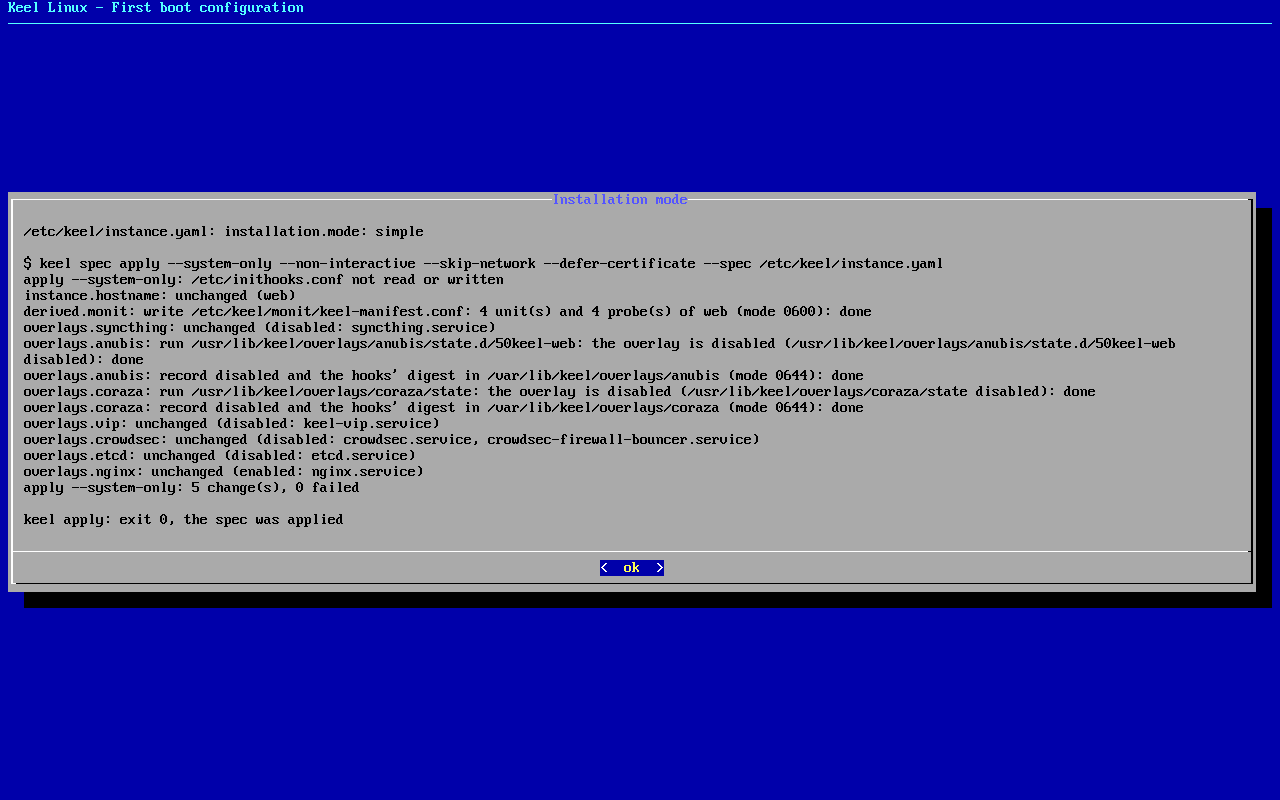
typed:
<ret> - 18
alert email
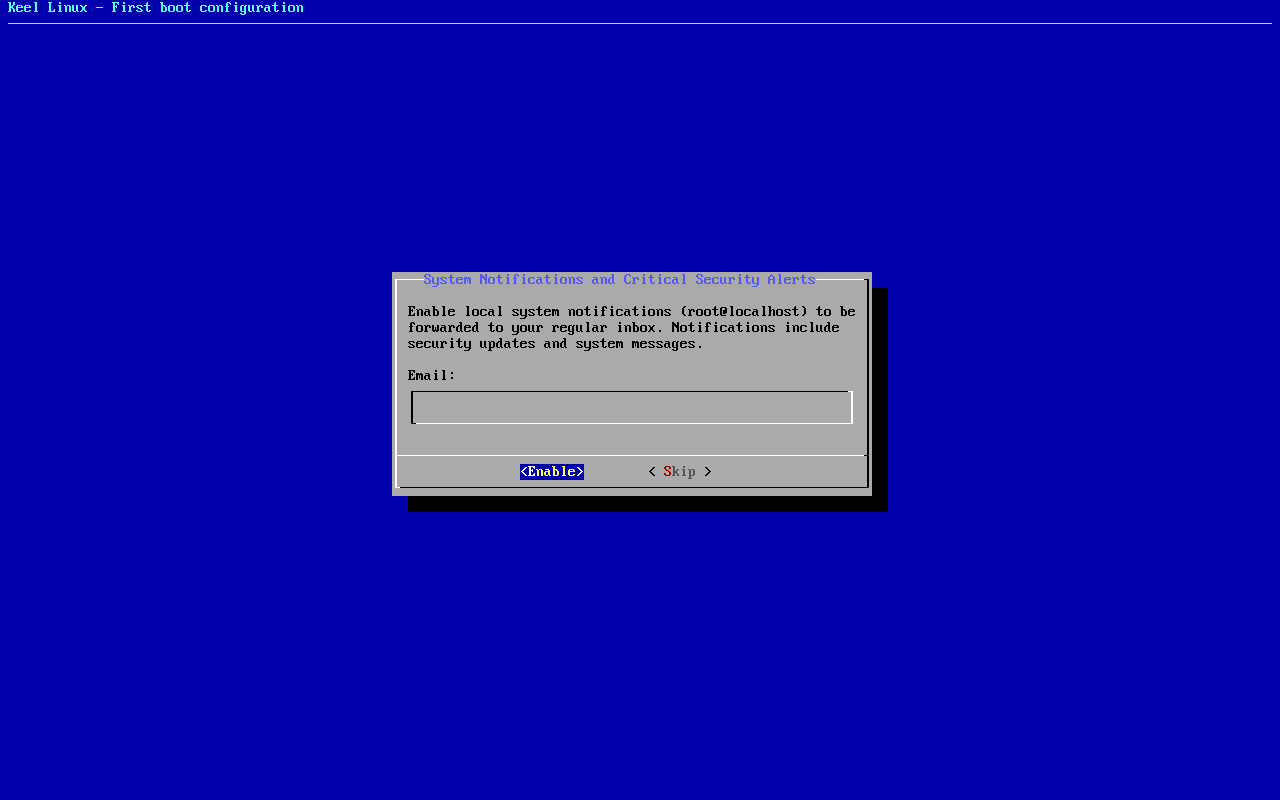
typed:
admin@example.org<ret> - 19
firstboot-screen
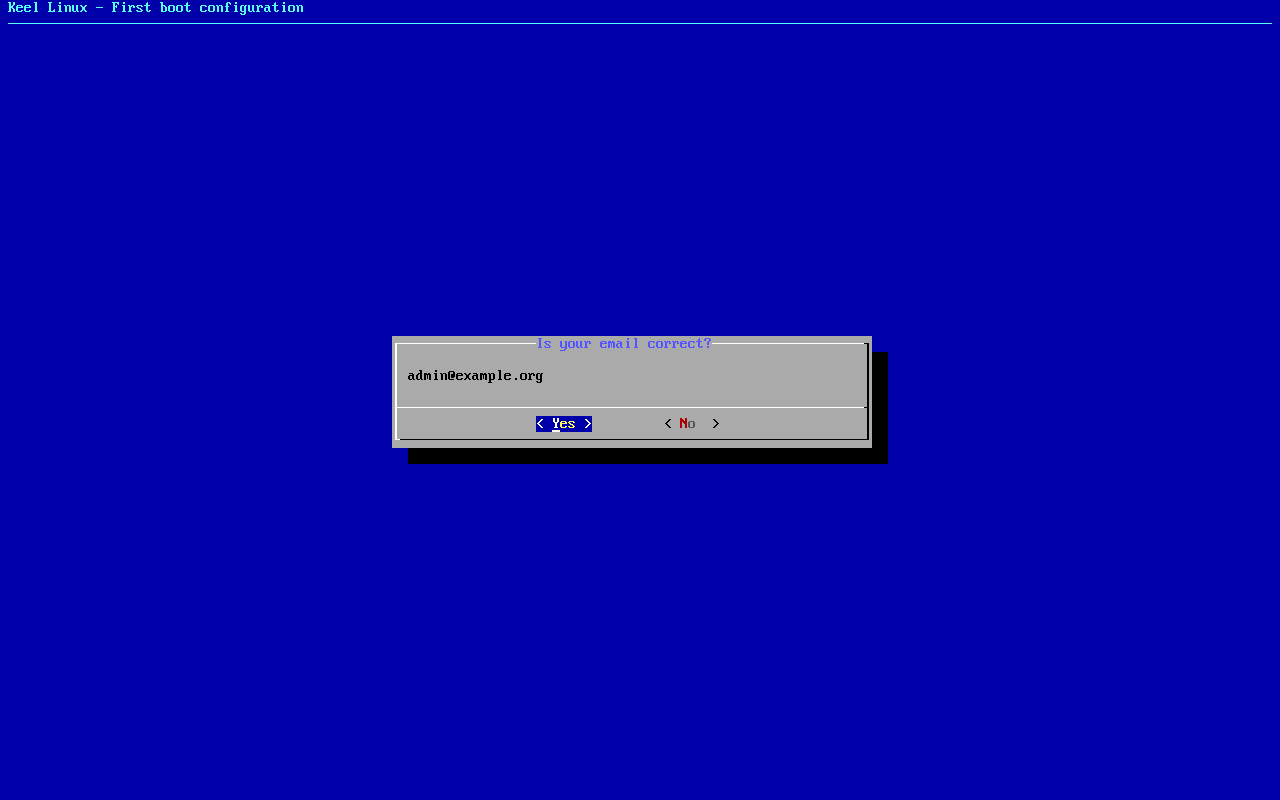
typed:
<ret> - 20
firstboot-screen
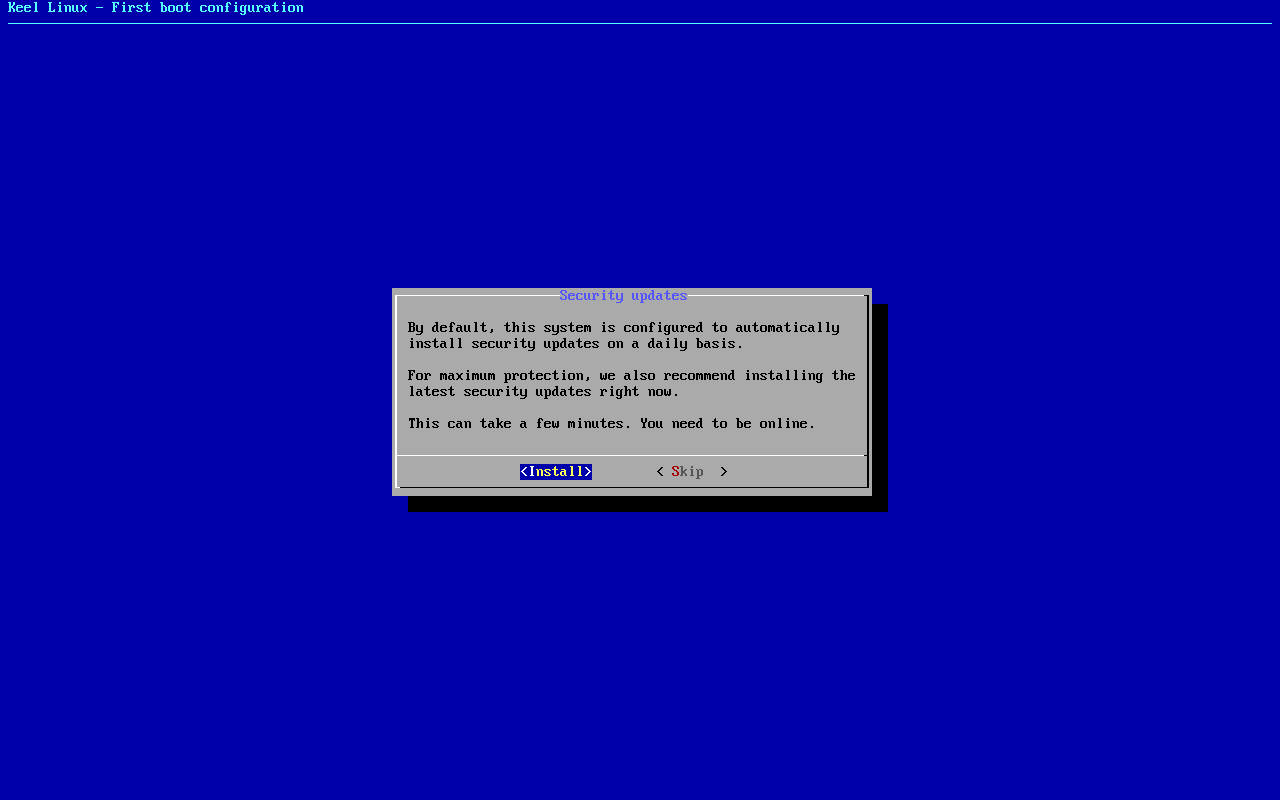
typed:
<ret> - 21
firstboot-end
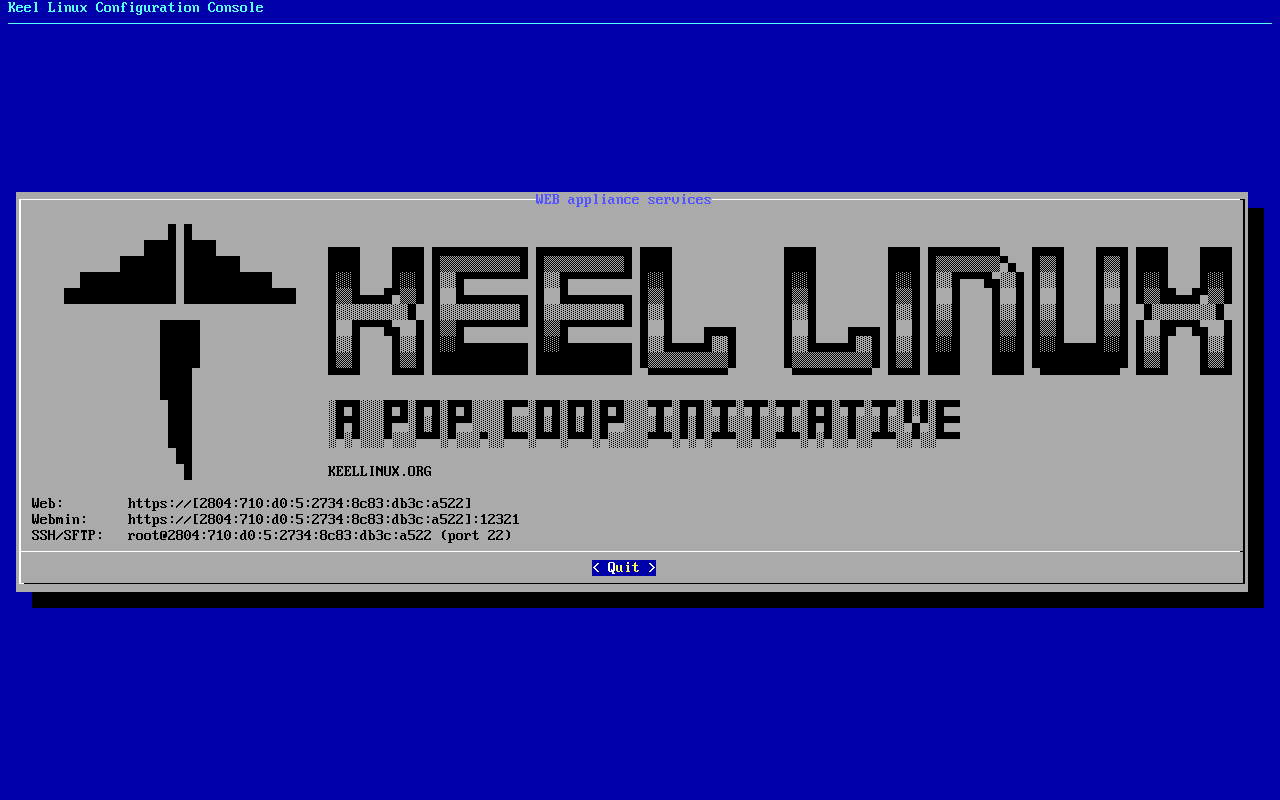
- 22
web: site
typed:
open / - 23
web: webmin
typed:
user root, the root secret - 24
web: webmin-after
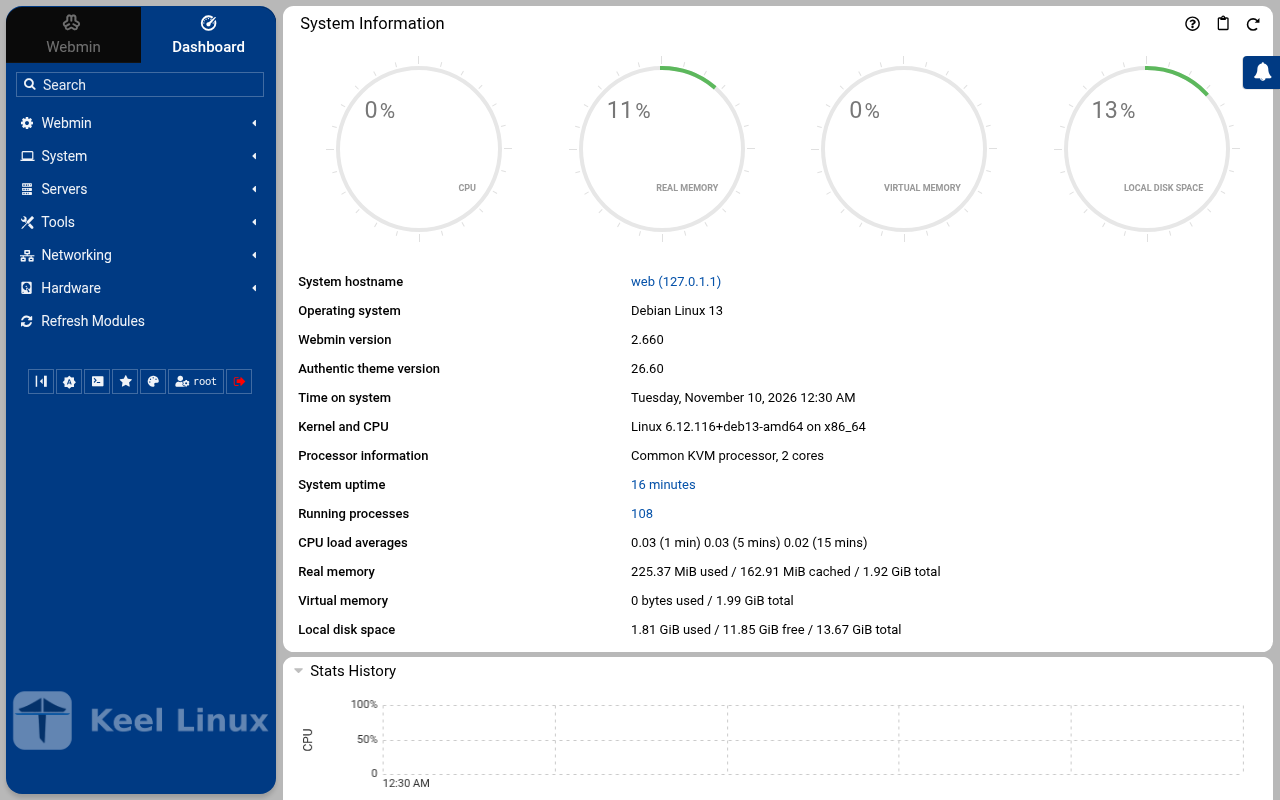
typed:
after the login: the page the login opened
Cloud simple: two nodes, failover by hand
| Step | Primary, BR1 | Replica, BR2 |
|---|---|---|
| 1 | root password the screen, as textConnected to tty 1 Type <Ctrl+a q> to exit the console, <Ctrl+a Ctrl+a> to enter Ctrl+a itself press Enter within 5 s to answer first-boot questions Keel Linux Configuration Console KC9383 appliance services < Quit > Web:https://[2804:710:d0:5:be24:11ff:fe9e:a821]Webmin: https://[2804:710:d0:5:be24:11ff:fe9e:a821]:12321SSH/SFTP: root@2804:710:d0:5:be24:11ff:fe9e:a821 (port 22) Keel Linux Configuration Console KC9383 appliance services < Quit > Web:https://[2804:710:d0:5:be24:11ff:fe9e:a821]Webmin: https://[2804:710:d0:5:be24:11ff:fe9e:a821]:12321SSH/SFTP: root@2804:710:d0:5:be24:11ff:fe9e:a821 (port 22) Debian GNU/Linux 13 kc9383 tty1 kc9383 login: root Password: Keel Linux web 19.0-trixie-amd64 IPv6 Web: https://[2804:710:d0:5:be24:11ff:fe9e:a821] IPv6 SSH: root@2804:710:d0:5:be24:11ff:fe9e:a821 Welcome to kc9383, Keel Linux 19.0 (Debian 13/Trixie) System information for Tue Nov 10 00:22:19 2026 (UTC+0000) System load: 8.44 Memory usage: 9.2% Processes: 32 Swap usage: 0.0% Usage of /: 11.4% of 7.78GB Networking not configured This system is not initialized yet: run keel-init to set it up. For Advanced commandline config run: confconsole For more info see: https://github.com/Keel-Linux/confconsole Linux kc9383 7.0.14-12-pve #1 SMP PREEMPT_DYNAMIC PMX 7.0.14-12 (2026-08-11T11:05Z) x86_64 === Keel Linux - First boot configuration Root Password Please enter new password for the root account. Choose how to set this password: Generate A strong random password (recommended) Manual Type my own password < OK >Generate A strong random password (recommended)Manual Type my own password Keel Linux - First boot configuration Root Password Please enter new password for the root account. Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: | root password the screen, as textConnected to tty 1 Type <Ctrl+a q> to exit the console, <Ctrl+a Ctrl+a> to enter Ctrl+a itself press Enter within 5 s to answer first-boot questions Keel Linux Configuration Console KC9384 appliance services < Quit > Web:https://[fd00:218:88:0:3447:e212:5767:772c]Webmin: https://[fd00:218:88:0:3447:e212:5767:772c]:12321SSH/SFTP: root@fd00:218:88:0:3447:e212:5767:772c (port 22)Web:https://10.218.88.69Webmin: https://10.218.88.69:12321SSH/SFTP: root@10.218.88.69 (port 22) Keel Linux Configuration Console KC9384 appliance services < Quit > Web:https://[fd00:218:88:0:3447:e212:5767:772c]Webmin: https://[fd00:218:88:0:3447:e212:5767:772c]:12321SSH/SFTP: root@fd00:218:88:0:3447:e212:5767:772c (port 22)Web:https://10.218.88.69Webmin: https://10.218.88.69:12321SSH/SFTP: root@10.218.88.69 (port 22) Debian GNU/Linux 13 kc9384 tty1 kc9384 login: root Password: Keel Linux web 19.0-trixie-amd64 IPv6 Web: https://[2804:7f0:9880:6c3:7b88:3225:d93:d4d2] IPv6 SSH: root@2804:7f0:9880:6c3:7b88:3225:d93:d4d2 IPv4 Web: https://10.218.88.69 IPv4 SSH: root@10.218.88.69 Welcome to kc9384, Keel Linux 19.0 (Debian 13/Trixie) System information for Tue Nov 10 00:25:02 2026 (UTC+0000) System load: 9.03 Memory usage: 6.6% Processes: 35 Swap usage: 0.0% Usage of /: 8.3% of 8.00GB IP address for eth0: 10.218.88.69 This system is not initialized yet: run keel-init to set it up. For Advanced commandline config run: confconsole For more info see: https://github.com/Keel-Linux/confconsole Linux kc9384 7.0.14-19-pve #1 SMP PREEMPT_DYNAMIC PMX 7.0.14-19 (2026-09-18T07:31Z) x86_64 === Keel Linux - First boot configuration Root Password Please enter new password for the root account. Choose how to set this password: Generate A strong random password (recommended) Manual Type my own password < OK >Generate A strong random password (recommended)Manual Type my own password Keel Linux - First boot configuration Root Password Please enter new password for the root account. Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: |
| 2 | root password the screen, as text******** Keel Linux - First boot configuration Root Password Confirm password Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: | root password the screen, as text******** Keel Linux - First boot configuration Root Password Confirm password Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: |
| 3 | mode the screen, as text******** Keel Linux - First boot configuration kc9383.pop.coop Domain name xxx The name this machine is reached by, with its domain, xx for example blog.example.org. It becomes the hostname, xx the name /etc/hosts answers for this machine, and the xx domain a TLS certificate is requested for in xx confconsole.xxxx Leave the field empty to keep the name the machine has. xxxx Fully qualified domain name:x <Apply>x >fqdn: /etc/keel/instance.yaml already declares the name, not written === Keel Linux - First boot configuration Installation mode How this appliance is installed (decision 0028). You choose it once. Simple: one node. Everything is on this machine, with no mesh. Cloud simple: two nodes, a primary and a replica on a WireGuard mesh. The data follows the primary. When the primary stops, you promote the replica by hand. Cloud advanced: two data nodes and a witness, three sites, etcd of three. When the primary stops, the replica takes over by itself. Choose the same mode on every node of the set. Simple one node, no mesh Cloud simple two nodes, failover by hand Cloud advanced two nodes and a witness, failover by itself <Select> typed: | mode the screen, as text******** Keel Linux - First boot configuration kc9384.pop.coop Domain name xxx The name this machine is reached by, with its domain, xx for example blog.example.org. It becomes the hostname, xx the name /etc/hosts answers for this machine, and the xx domain a TLS certificate is requested for in xx confconsole.xxxx Leave the field empty to keep the name the machine has. xxxx Fully qualified domain name:x <Apply>x >fqdn: /etc/keel/instance.yaml already declares the name, not written === Keel Linux - First boot configuration Installation mode How this appliance is installed (decision 0028). You choose it once. Simple: one node. Everything is on this machine, with no mesh. Cloud simple: two nodes, a primary and a replica on a WireGuard mesh. The data follows the primary. When the primary stops, you promote the replica by hand. Cloud advanced: two data nodes and a witness, three sites, etcd of three. When the primary stops, the replica takes over by itself. Choose the same mode on every node of the set. Simple one node, no mesh Cloud simple two nodes, failover by hand Cloud advanced two nodes and a witness, failover by itself <Select> typed: |
| 4 | role the screen, as textSimpleone node, no meshCloud simple two nodes, failover by hand> == Keel Linux - First boot configuration Installation mode < ok >x /etc/keel/instance.yaml: installation.mode: cloud_simple$ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yaml2026-11-10 00:22:34 INF Generating key and certificate (cn=syncthing log.pkg=syncthing)2026-11-10 00:22:34 INF Calculated device ID(device=A4K4BKS-L6MRQUL-QKKUHOP-HMU2M4G-ASVKHXJ-XFYF7BJ-OVWBUAE-VMDR7Q2 log.pkg=github)apply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9383)instance.fqdn: unchanged (/etc/hosts maps kc9383 to kc9383.pop.coop)derived.monit: crowdsec not watched: crowdsec.service starts only when /etc/crowdsec/local_api_credentials.yamlexists (ConditionPathExists)derived.monit: crowdsec-lapi not watched: its process crowdsec is not watched: crowdsec.service starts only when/etc/crowdsec/local_api_credentials.yaml exists (ConditionPathExists)derived.monit: write /etc/keel/monit/keel-manifest.conf: 7 unit(s) and 7 probe(s) of web (mode 0600): doneoverlays.vip: unchanged (disabled: keel-vip.service)overlays.etcd: unchanged (disabled: etcd.service)overlays.crowdsec: create /etc/crowdsec/online_api_credentials.yaml empty, which CrowdSec's unit needs and whichsays not registered yet (mode 0600): doneoverlays.crowdsec: register this machine with CrowdSec's local API; cscli writes the password to/etc/crowdsec/local_api_credentials.yaml (cscli --error machines add --auto --force): doneoverlays.crowdsec: register with CrowdSec's central API (cscli --error capi register): doneoverlays.crowdsec: register CrowdSec's firewall bouncer (cscli bouncers add) and write its key to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.local (mode 0600, never printed) and its name to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.id, mode: nftables: doneoverlays.crowdsec: enable crowdsec.service: the overlay is enabled (systemctl enable crowdsec.service): doneoverlays.crowdsec: start crowdsec.service (systemctl start crowdsec.service): doneoverlays.crowdsec: enable crowdsec-firewall-bouncer.service: the overlay is enabled (systemctl enablecrowdsec-firewall-bouncer.service): doneoverlays.crowdsec: start crowdsec-firewall-bouncer.service (systemctl start crowdsec-firewall-bouncer.service):done57% Keel Linux - First boot configuration Role of this node What this node is in its set of two (cloud simple). Primary: the first node. It makes the mesh and invites the replica with a line you copy to it. Replica: the second node. It joins with that line, and its data follows the primary. Primary the first node: makes the mesh, invites Replica joins the primary; its data follows it <Select> typed: | role the screen, as textSimpleone node, no meshCloud simple two nodes, failover by hand> == Keel Linux - First boot configuration Installation mode < ok >x /etc/keel/instance.yaml: installation.mode: cloud_simple$ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yaml2026-11-10 00:25:17 INF Generating key and certificate (cn=syncthing log.pkg=syncthing)2026-11-10 00:25:17 INF Calculated device ID(device=7VNVONC-UR7EIOZ-WRDUJ44-XDYYKEK-2POWVSD-GVDUGUV-MQ7U6VR-65VMGAU log.pkg=github)apply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9384)instance.fqdn: unchanged (/etc/hosts maps kc9384 to kc9384.pop.coop)derived.monit: crowdsec not watched: crowdsec.service starts only when /etc/crowdsec/local_api_credentials.yamlexists (ConditionPathExists)derived.monit: crowdsec-lapi not watched: its process crowdsec is not watched: crowdsec.service starts only when/etc/crowdsec/local_api_credentials.yaml exists (ConditionPathExists)derived.monit: write /etc/keel/monit/keel-manifest.conf: 7 unit(s) and 7 probe(s) of web (mode 0600): doneoverlays.vip: unchanged (disabled: keel-vip.service)overlays.etcd: unchanged (disabled: etcd.service)overlays.crowdsec: create /etc/crowdsec/online_api_credentials.yaml empty, which CrowdSec's unit needs and whichsays not registered yet (mode 0600): doneoverlays.crowdsec: register this machine with CrowdSec's local API; cscli writes the password to/etc/crowdsec/local_api_credentials.yaml (cscli --error machines add --auto --force): doneoverlays.crowdsec: register with CrowdSec's central API (cscli --error capi register): doneoverlays.crowdsec: register CrowdSec's firewall bouncer (cscli bouncers add) and write its key to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.local (mode 0600, never printed) and its name to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.id, mode: nftables: doneoverlays.crowdsec: enable crowdsec.service: the overlay is enabled (systemctl enable crowdsec.service): doneoverlays.crowdsec: start crowdsec.service (systemctl start crowdsec.service): doneoverlays.crowdsec: enable crowdsec-firewall-bouncer.service: the overlay is enabled (systemctl enablecrowdsec-firewall-bouncer.service): doneoverlays.crowdsec: start crowdsec-firewall-bouncer.service (systemctl start crowdsec-firewall-bouncer.service):done57% Keel Linux - First boot configuration Role of this node What this node is in its set of two (cloud simple). Primary: the first node. It makes the mesh and invites the replica with a line you copy to it. Replica: the second node. It joins with that line, and its data follows the primary. Primary the first node: makes the mesh, invites Replica joins the primary; its data follows it <Select> typed: |
| 5 | invite the screen, as textKeel Linux - First boot configuration keel mesh create: making the mesh... Keel Linux - First boot configuration Make the mesh < ok >x $ keel mesh createcreated the mesh: this node is fdaa:c9af:d83d::1/64 on wg0, WireGuard on UDP 51820keel mesh invite prints the line that joins the next nodeconfirming the new overlayconfirmed from keel mesh createthe overlay has no peer, so nothing can cross it: keel mesh create confirmed it once the routes to the gatewaysand to the operator's session were found to still leave through the uplinkwg-quick@wg0 enabled: the overlay comes back up at bootthe network change stays; the revert is cancelledmesh: this node holds the mesh's root CA, which signs the database certificates of a cloud simple pairkeel mesh: exit 0, done>Invite a node This node invites the replica (node 2) into its mesh. Copy the line below to the replica (node 2): paste it into its Join a mesh screen, or run it there as root. It can be used once, until 2026-11-10T01:23:14Z. The line carries the service address of the pair, shown below: this node writes it as its appliance.vip, and the replica takes it from the join. Nobody types it. Copy this line to the replica (node 2), on one line, as it is. It is a secret: it lets one node join this mesh. keel mesh join - <<< <invite 1> VIP: fdaa:c9af:d83d::ffff:1 Expires: 2026-11-10T01:23:14Z Press Enter to go on: typed: | join the screen, as textPrimary the first node: makes the mesh, invitesReplica joins the primary; its data follows it Keel Linux - First boot configuration Join a mesh Paste the line that Invite a node shows on the inviting node: keel mesh join - <<< keel2:... The token alone (keel2:...) is accepted too. It goes to keel on its standard input, never on a command line. < OK > <Cancel>x typed: |
| 6 | alert email the screen, as textThis node: fdaa:c9af:d83d::1/64 VIP: fdaa:c9af:d83d::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0 Keel Linux - First boot configuration Waiting for the nodes Waiting for the replica (node 2) to join with the line, checked every 5 s. Back gives a menu: Paste accept line, when the join printed one (keel mesh accept keel1a:...), or the line again. This node: fdaa:c9af:d83d::1/64 VIP: fdaa:c9af:d83d::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0 Keel Linux - First boot configuration Waiting for the nodes Waiting for the replica (node 2) to join with the line, checked every 5 s. Back gives a menu: Paste accept line, when the join printed one (keel mesh accept keel1a:...), or the line again. This node: fdaa:c9af:d83d::1/64 VIP: fdaa:c9af:d83d::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0 Keel Linux - First boot configuration Take the VIP < ok >x $ keel vip promotefdaa:c9af:d83d::61b: appliedthis node holds fdaa:c9af:d83d::ffff:1 at epoch 1, on wg0, taken by the other member of the pair; the otherpeers are told in the backgroundkeel vip: exit 0, done Keel Linux - First boot configuration Status of this node < ok >x $ keel vip statusvip fdaa:c9af:d83d::ffff:1: this node's appliance.viprole: primaryepoch 1, held by <public key> at fdaa:c9af:d83d::1carried here: yesrouted to: no peer$ keel mesh statusthis node: fdaa:c9af:d83d::1/64 on wg0, WireGuard on UDP 51820mesh identity: b09b2a8e2d0fc529b5dca9809f2f60f1public key: <public key>peers: 1<public key> fdaa:c9af:d83d::61b/128[2804:7f0:9880:6c3:7b88:3225:d93:d4d2]:51820 handshake 11 s agopending invites: 0etcd: not on this node (installation.mode cloud_simple; etcd runs on cloud advanced members only)vip fdaa:c9af:d83d::ffff:1: this node's appliance.viprole: primaryepoch 1, held by <public key> at fdaa:c9af:d83d::1carried here: yesrouted to: no peer>keelfirstboot cloud: Keel Cloud is not available yet: no key is asked, and this node runs standalone. It is offered once /etc/keel/cloud-endpoint names the service. === Keel Linux - First boot configuration System Notifications and Critical Security Alerts Enable local system notifications (root@localhost) to be forwarded to your regular inbox. Notifications include security updates and system messages. Email: <Enable> < Skip >x typed: | alert email the screen, as text<invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1>F<invite 1>FA<invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1>Q<invite 1><invite 1>Q<invite 1><invite 1>Q<invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1>g9<invite 1>9<invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1>D<invite 1>D_<invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1>>Join a mesh Join a mesh: keel joins this node to the mesh. When the inviting node cannot be reached, keel prints a line keel mesh accept keel1a:... and waits: run that line on the inviting node, or paste it into its Paste accept line screen. endpoint 2804:7f0:9880:6c3:7b88:3225:d93:d4d2, found on eth0 (--endpoint overrides it) confirming over the overlay confirmed from the inviter's answer over the overlay (invite 9aed2763bf132f7d) the overlay was tested: the inviter's answer over the overlay (invite 9aed2763bf132f7d) arrived at fdaa:c9af:d83d::61b on wg0, from fdaa:c9af:d83d::1 wg-quick@wg0 enabled: the overlay comes back up at boot the network change stays; the revert is cancelled joined the mesh: this node is fdaa:c9af:d83d::61b/64 on wg0 peer: <public key> at fdaa:c9af:d83d::1, through [2804:710:d0:5:be24:11ff:fe9e:a821]:51820 the mesh is up with 2 nodes; etcd starts when a third node joins, because 2 etcd members cannot lose one and keep a majority vip: fdaa:c9af:d83d::ffff:1, proposed by the inviter for the pair (appliance.vip on both nodes; keel mesh status --json gives it) Press Enter to go on: == Keel Linux - First boot configuration Pair with the primary < ok >x $ keel vip pair fdaa:c9af:d83d::1fdaa:c9af:d83d::ffff:1 is the VIP of <public key> and<public key>, signed by bothkeel vip: exit 0, done Keel Linux - First boot configuration Pair with the primary < ok >x $ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yamlapply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9384)instance.fqdn: unchanged (/etc/hosts maps kc9384 to kc9384.pop.coop)derived.monit: keel-vip not watched: keel-vip.service starts only when /var/lib/keel/etcd/cluster.json exists(ConditionPathExists)derived.monit: unchanged (/etc/keel/monit/keel-manifest.conf, 8 unit(s) and 8 probe(s) of web, not included)overlays.etcd: unchanged (disabled: etcd.service)overlays.crowdsec: unchanged (enabled: crowdsec.service, crowdsec-firewall-bouncer.service)overlays.vip: enable keel-vip.service: the overlay is enabled (systemctl enable keel-vip.service): doneoverlays.vip: keel-vip.service waits for etcd's cluster (cluster.json): it starts once etcd forms; without etcd,keel vip check (keel-vip-check.timer) does its work (keel#106)overlays.nginx: unchanged (enabled: nginx.service)overlays.coraza: unchanged (enabled: /usr/lib/keel/overlays/coraza/state)overlays.anubis: unchanged (enabled: anubis@keel.service, /usr/lib/keel/overlays/anubis/state.d/50keel-web)overlays.syncthing: unchanged (enabled: syncthing.service)network.overlay: not brought up in this run (--skip-network)apply --system-only: 1 change(s), 0 failedkeel apply: exit 0, the spec was applied Keel Linux - First boot configuration Status of this node < ok >x $ keel vip statusvip fdaa:c9af:d83d::ffff:1: this node's appliance.viprole: replicaepoch 1, held by <public key> at fdaa:c9af:d83d::1carried here: norouted to: <public key>$ keel mesh statusthis node: fdaa:c9af:d83d::61b/64 on wg0, WireGuard on UDP 51820mesh identity: b09b2a8e2d0fc529b5dca9809f2f60f1public key: <public key>peers: 1<public key> fdaa:c9af:d83d::1/128 [2804:710:d0:5:be24:11ff:fe9e:a821]:51820handshake 17 s agopending invites: 0etcd: not on this node (installation.mode cloud_simple; etcd runs on cloud advanced members only)vip fdaa:c9af:d83d::ffff:1: this node's appliance.viprole: replicaepoch 1, held by <public key> at fdaa:c9af:d83d::1carried here: norouted to: <public key>>keelfirstboot cloud: Keel Cloud is not available yet: no key is asked, and this node runs standalone. It is offered once /etc/keel/cloud-endpoint names the service. === Keel Linux - First boot configuration System Notifications and Critical Security Alerts Enable local system notifications (root@localhost) to be forwarded to your regular inbox. Notifications include security updates and system messages. Email: <Enable> < Skip >x typed: |
| 7 | web: site  typed: | web: site  typed: |
| 8 | web: webmin  typed: | web: webmin  typed: |
| 9 | web: webmin-after 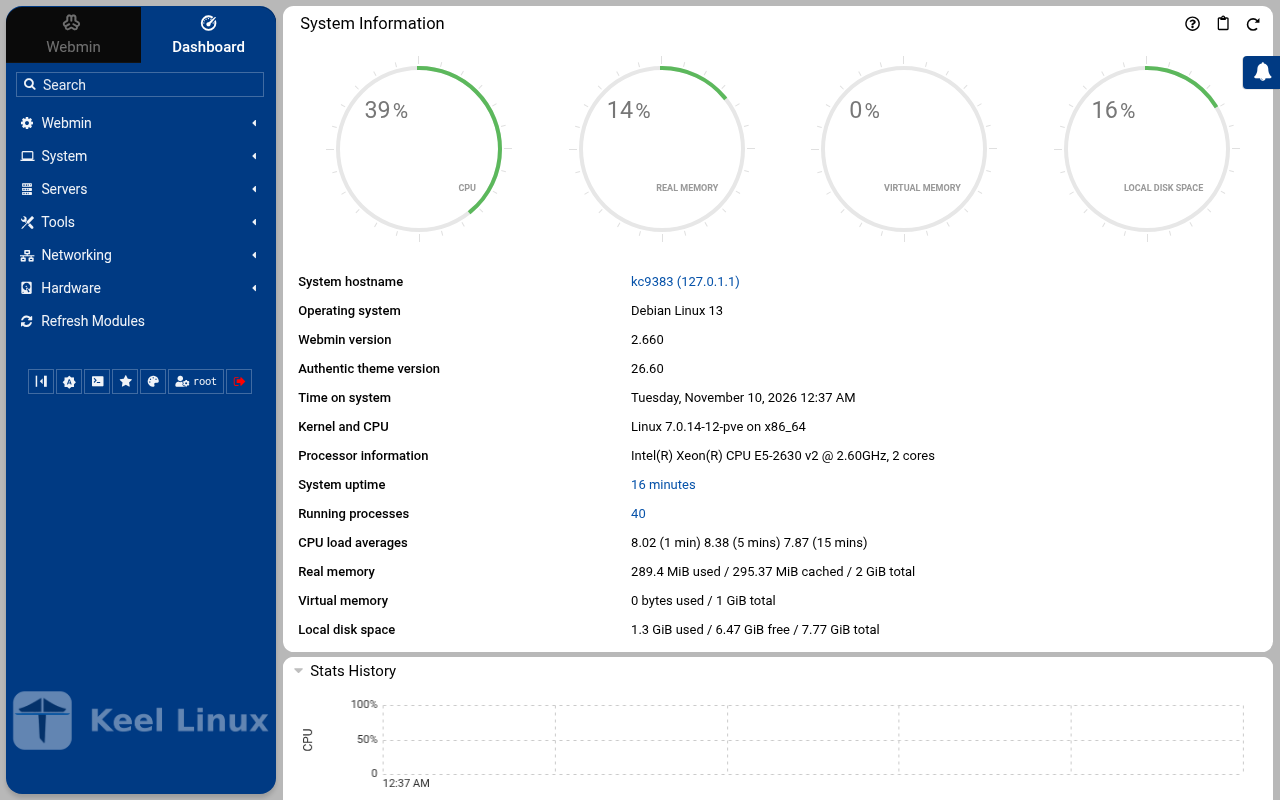 typed: | web: webmin-after 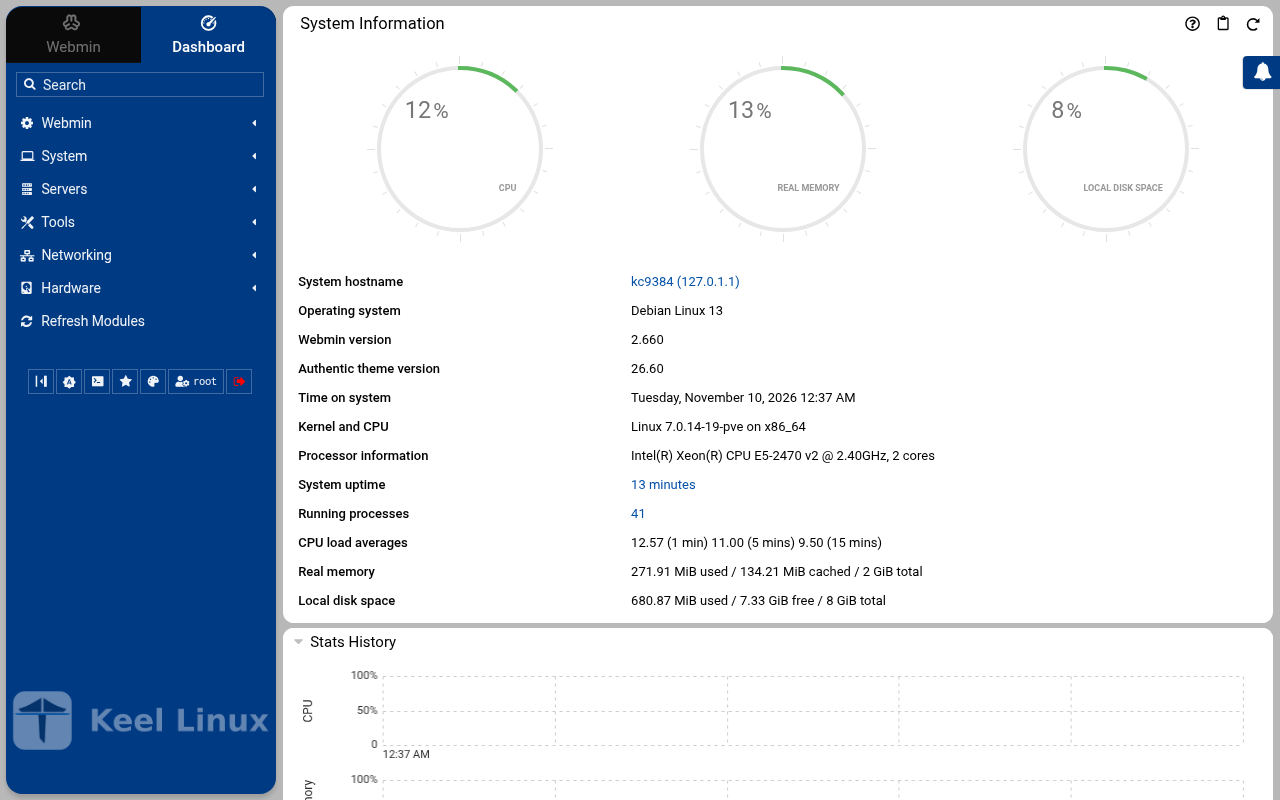 typed: |
Cloud advanced: two data nodes and a witness
| Step | Primary, BR1 | Replica, BR2 | Witness, BR1 |
|---|---|---|---|
| 1 | root password the screen, as textConnected to tty 1 Type <Ctrl+a q> to exit the console, <Ctrl+a Ctrl+a> to enter Ctrl+a itself press Enter within 5 s to answer first-boot questions Keel Linux Configuration Console KC9385 appliance services < Quit > Web:https://[2804:710:d0:5:be24:11ff:fe4e:c66d]Webmin: https://[2804:710:d0:5:be24:11ff:fe4e:c66d]:12321SSH/SFTP: root@2804:710:d0:5:be24:11ff:fe4e:c66d (port 22) Keel Linux Configuration Console KC9385 appliance services < Quit > Web:https://[2804:710:d0:5:be24:11ff:fe4e:c66d]Webmin: https://[2804:710:d0:5:be24:11ff:fe4e:c66d]:12321SSH/SFTP: root@2804:710:d0:5:be24:11ff:fe4e:c66d (port 22) Debian GNU/Linux 13 kc9385 tty1 kc9385 login: root Password: Keel Linux web 19.0-trixie-amd64 IPv6 Web: https://[2804:710:d0:5:be24:11ff:fe4e:c66d] IPv6 SSH: root@2804:710:d0:5:be24:11ff:fe4e:c66d Welcome to kc9385, Keel Linux 19.0 (Debian 13/Trixie) System information for Tue Nov 10 00:40:32 2026 (UTC+0000) System load: 7.77 Memory usage: 9.2% Processes: 32 Swap usage: 0.0% Usage of /: 11.4% of 7.78GB Networking not configured This system is not initialized yet: run keel-init to set it up. For Advanced commandline config run: confconsole For more info see: https://github.com/Keel-Linux/confconsole Linux kc9385 7.0.14-12-pve #1 SMP PREEMPT_DYNAMIC PMX 7.0.14-12 (2026-08-11T11:05Z) x86_64 === Keel Linux - First boot configuration Root Password Please enter new password for the root account. Choose how to set this password: Generate A strong random password (recommended) Manual Type my own password < OK >Generate A strong random password (recommended)Manual Type my own password Keel Linux - First boot configuration Root Password Please enter new password for the root account. Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: | root password the screen, as textConnected to tty 1 Type <Ctrl+a q> to exit the console, <Ctrl+a Ctrl+a> to enter Ctrl+a itself press Enter within 5 s to answer first-boot questions Keel Linux Configuration Console KC9386 appliance services < Quit > Web:https://[fd00:218:88:0:d7ab:3199:1b04:93b9]Webmin: https://[fd00:218:88:0:d7ab:3199:1b04:93b9]:12321SSH/SFTP: root@fd00:218:88:0:d7ab:3199:1b04:93b9 (port 22)Web:https://10.218.88.76Webmin: https://10.218.88.76:12321SSH/SFTP: root@10.218.88.76 (port 22) Keel Linux Configuration Console KC9386 appliance services < Quit > Web:https://[fd00:218:88:0:d7ab:3199:1b04:93b9]Webmin: https://[fd00:218:88:0:d7ab:3199:1b04:93b9]:12321SSH/SFTP: root@fd00:218:88:0:d7ab:3199:1b04:93b9 (port 22)Web:https://10.218.88.76Webmin: https://10.218.88.76:12321SSH/SFTP: root@10.218.88.76 (port 22) Debian GNU/Linux 13 kc9386 tty1 kc9386 login: root Password: Keel Linux web 19.0-trixie-amd64 IPv6 Web: https://[2804:7f0:9880:6c3:a3f2:6930:d841:f919] IPv6 SSH: root@2804:7f0:9880:6c3:a3f2:6930:d841:f919 IPv4 Web: https://10.218.88.76 IPv4 SSH: root@10.218.88.76 Welcome to kc9386, Keel Linux 19.0 (Debian 13/Trixie) System information for Tue Nov 10 00:43:58 2026 (UTC+0000) System load: 14.83 Memory usage: 6.6% Processes: 35 Swap usage: 0.0% Usage of /: 8.3% of 8.00GB IP address for eth0: 10.218.88.76 This system is not initialized yet: run keel-init to set it up. For Advanced commandline config run: confconsole For more info see: https://github.com/Keel-Linux/confconsole Linux kc9386 7.0.14-19-pve #1 SMP PREEMPT_DYNAMIC PMX 7.0.14-19 (2026-09-18T07:31Z) x86_64 === Keel Linux - First boot configuration Root Password Please enter new password for the root account. Choose how to set this password: Generate A strong random password (recommended) Manual Type my own password < OK >Generate A strong random password (recommended)Manual Type my own password Keel Linux - First boot configuration Root Password Please enter new password for the root account. Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: | root password the screen, as textConnected to tty 1 Type <Ctrl+a q> to exit the console, <Ctrl+a Ctrl+a> to enter Ctrl+a itself press Enter within 5 s to answer first-boot questions Keel Linux Configuration Console KC9387 appliance services < Quit > Webmin: https://[2804:710:d0:5:be24:11ff:fe45:a0c7]:12321SSH/SFTP: root@2804:710:d0:5:be24:11ff:fe45:a0c7 (port 22) Keel Linux Configuration Console KC9387 appliance services < Quit > Webmin: https://[2804:710:d0:5:be24:11ff:fe45:a0c7]:12321SSH/SFTP: root@2804:710:d0:5:be24:11ff:fe45:a0c7 (port 22) Debian GNU/Linux 13 kc9387 tty1 kc9387 login: root Password: Keel Linux core 19.0-trixie-amd64 IPv6 SSH: root@2804:710:d0:5:be24:11ff:fe45:a0c7 Welcome to kc9387, Keel Linux 19.0 (Debian 13/Trixie) System information for Tue Nov 10 00:46:14 2026 (UTC+0000) System load: 7.31 Memory usage: 8.9% Processes: 29 Swap usage: 0.0% Usage of /: 9.9% of 7.78GB Networking not configured This system is not initialized yet: run keel-init to set it up. For Advanced commandline config run: confconsole For more info see: https://github.com/Keel-Linux/confconsole Linux kc9387 7.0.14-12-pve #1 SMP PREEMPT_DYNAMIC PMX 7.0.14-12 (2026-08-11T11:05Z) x86_64 === Keel Linux - First boot configuration Root Password Please enter new password for the root account. Choose how to set this password: Generate A strong random password (recommended) Manual Type my own password < OK >Generate A strong random password (recommended)Manual Type my own password Keel Linux - First boot configuration Root Password Please enter new password for the root account. Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: |
| 2 | root password the screen, as text******** Keel Linux - First boot configuration Root Password Confirm password Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: | root password the screen, as text******** Keel Linux - First boot configuration Root Password Confirm password Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: | root password the screen, as text******** Keel Linux - First boot configuration Root Password Confirm password Password Requirements - must be at least 8 characters long - must contain characters from at least 3 of the following categories: uppercase, lowercase, numbers, symbols < OK >x typed: |
| 3 | mode the screen, as text******** Keel Linux - First boot configuration kc9385.pop.coop Domain name xxx The name this machine is reached by, with its domain, xx for example blog.example.org. It becomes the hostname, xx the name /etc/hosts answers for this machine, and the xx domain a TLS certificate is requested for in xx confconsole.xxxx Leave the field empty to keep the name the machine has. xxxx Fully qualified domain name:x <Apply>x >fqdn: /etc/keel/instance.yaml already declares the name, not written === Keel Linux - First boot configuration Installation mode How this appliance is installed (decision 0028). You choose it once. Simple: one node. Everything is on this machine, with no mesh. Cloud simple: two nodes, a primary and a replica on a WireGuard mesh. The data follows the primary. When the primary stops, you promote the replica by hand. Cloud advanced: two data nodes and a witness, three sites, etcd of three. When the primary stops, the replica takes over by itself. Choose the same mode on every node of the set. Simple one node, no mesh Cloud simple two nodes, failover by hand Cloud advanced two nodes and a witness, failover by itself <Select> typed: | mode the screen, as text******** Keel Linux - First boot configuration kc9386.pop.coop Domain name xxx The name this machine is reached by, with its domain, xx for example blog.example.org. It becomes the hostname, xx the name /etc/hosts answers for this machine, and the xx domain a TLS certificate is requested for in xx confconsole.xxxx Leave the field empty to keep the name the machine has. xxxx Fully qualified domain name:x <Apply>x >fqdn: /etc/keel/instance.yaml already declares the name, not written === Keel Linux - First boot configuration Installation mode How this appliance is installed (decision 0028). You choose it once. Simple: one node. Everything is on this machine, with no mesh. Cloud simple: two nodes, a primary and a replica on a WireGuard mesh. The data follows the primary. When the primary stops, you promote the replica by hand. Cloud advanced: two data nodes and a witness, three sites, etcd of three. When the primary stops, the replica takes over by itself. Choose the same mode on every node of the set. Simple one node, no mesh Cloud simple two nodes, failover by hand Cloud advanced two nodes and a witness, failover by itself <Select> typed: | mode the screen, as text******** Keel Linux - First boot configuration kc9387.pop.coop Domain name xxx The name this machine is reached by, with its domain, xx for example blog.example.org. It becomes the hostname, xx the name /etc/hosts answers for this machine, and the xx domain a TLS certificate is requested for in xx confconsole.xxxx Leave the field empty to keep the name the machine has. xxxx Fully qualified domain name:x <Apply>x >fqdn: /etc/keel/instance.yaml already declares the name, not written === Keel Linux - First boot configuration Installation mode How this appliance is installed (decision 0028). You choose it once. Simple: one node. Everything is on this machine, with no mesh. Cloud simple: two nodes, a primary and a replica on a WireGuard mesh. The data follows the primary. When the primary stops, you promote the replica by hand. Cloud advanced: two data nodes and a witness, three sites, etcd of three. When the primary stops, the replica takes over by itself. Choose the same mode on every node of the set. Simple one node, no mesh Cloud simple two nodes, failover by hand Cloud advanced two nodes and a witness, failover by itself <Select> typed: |
| 4 | role the screen, as textSimpleone node, no meshCloud simple two nodes, failover by handCloud simple two nodes, failover by handCloud advanced two nodes and a witness, failover by itself> == Keel Linux - First boot configuration Installation mode < ok >x /etc/keel/instance.yaml: installation.mode: cloud_advanced$ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yaml2026-11-10 00:40:46 INF Generating key and certificate (cn=syncthing log.pkg=syncthing)2026-11-10 00:40:46 INF Calculated device ID(device=V7C53RZ-MQRWST7-GC6O2VT-P3EYQRZ-MYUWTQO-PFEFCZT-RBDWZKN-7O5E5QM log.pkg=github)apply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9385)instance.fqdn: unchanged (/etc/hosts maps kc9385 to kc9385.pop.coop)derived.monit: crowdsec not watched: crowdsec.service starts only when /etc/crowdsec/local_api_credentials.yamlexists (ConditionPathExists)derived.monit: crowdsec-lapi not watched: its process crowdsec is not watched: crowdsec.service starts only when/etc/crowdsec/local_api_credentials.yaml exists (ConditionPathExists)derived.monit: write /etc/keel/monit/keel-manifest.conf: 8 unit(s) and 8 probe(s) of web (mode 0600): doneoverlays.vip: unchanged (disabled: keel-vip.service)overlays.etcd: etcd waits for its cluster: it forms at the third cloud advanced member's join, or with keel meshetcd form; nothing is started until thenoverlays.crowdsec: create /etc/crowdsec/online_api_credentials.yaml empty, which CrowdSec's unit needs and whichsays not registered yet (mode 0600): doneoverlays.crowdsec: register this machine with CrowdSec's local API; cscli writes the password to/etc/crowdsec/local_api_credentials.yaml (cscli --error machines add --auto --force): doneoverlays.crowdsec: register with CrowdSec's central API (cscli --error capi register): doneoverlays.crowdsec: register CrowdSec's firewall bouncer (cscli bouncers add) and write its key to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.local (mode 0600, never printed) and its name to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.id, mode: nftables: doneoverlays.crowdsec: enable crowdsec.service: the overlay is enabled (systemctl enable crowdsec.service): doneoverlays.crowdsec: start crowdsec.service (systemctl start crowdsec.service): doneoverlays.crowdsec: enable crowdsec-firewall-bouncer.service: the overlay is enabled (systemctl enablecrowdsec-firewall-bouncer.service): doneoverlays.crowdsec: start crowdsec-firewall-bouncer.service (systemctl start crowdsec-firewall-bouncer.service):56% Keel Linux - First boot configuration Role of this node What this node is in its set of three (cloud advanced). Primary: the first node. It makes the mesh and invites the replica, then the witness, each with a line you copy to it. Replica: the second node. It joins with the first line, and its data follows the primary. Witness: the third node, Keel Core on a third site. It joins with the second line and gives etcd its third vote. It holds no data. Primary the first node: makes the mesh, invites Replica joins the primary; its data follows it <Select> typed: | role the screen, as textSimpleone node, no meshCloud simple two nodes, failover by handCloud simple two nodes, failover by handCloud advanced two nodes and a witness, failover by itself> == Keel Linux - First boot configuration Installation mode < ok >x /etc/keel/instance.yaml: installation.mode: cloud_advanced$ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yaml2026-11-10 00:44:14 INF Generating key and certificate (cn=syncthing log.pkg=syncthing)2026-11-10 00:44:14 INF Calculated device ID(device=NZ2L2M6-SGGSM6B-LFNJMX2-U5EJAB7-ZMKRXHR-EZTU6U7-BZLLBJQ-7TQ63AA log.pkg=github)apply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9386)instance.fqdn: unchanged (/etc/hosts maps kc9386 to kc9386.pop.coop)derived.monit: crowdsec not watched: crowdsec.service starts only when /etc/crowdsec/local_api_credentials.yamlexists (ConditionPathExists)derived.monit: crowdsec-lapi not watched: its process crowdsec is not watched: crowdsec.service starts only when/etc/crowdsec/local_api_credentials.yaml exists (ConditionPathExists)derived.monit: write /etc/keel/monit/keel-manifest.conf: 8 unit(s) and 8 probe(s) of web (mode 0600): doneoverlays.vip: unchanged (disabled: keel-vip.service)overlays.etcd: etcd waits for its cluster: it forms at the third cloud advanced member's join, or with keel meshetcd form; nothing is started until thenoverlays.crowdsec: create /etc/crowdsec/online_api_credentials.yaml empty, which CrowdSec's unit needs and whichsays not registered yet (mode 0600): doneoverlays.crowdsec: register this machine with CrowdSec's local API; cscli writes the password to/etc/crowdsec/local_api_credentials.yaml (cscli --error machines add --auto --force): doneoverlays.crowdsec: register with CrowdSec's central API (cscli --error capi register): doneoverlays.crowdsec: register CrowdSec's firewall bouncer (cscli bouncers add) and write its key to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.local (mode 0600, never printed) and its name to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.id, mode: nftables: doneoverlays.crowdsec: enable crowdsec.service: the overlay is enabled (systemctl enable crowdsec.service): doneoverlays.crowdsec: start crowdsec.service (systemctl start crowdsec.service): doneoverlays.crowdsec: enable crowdsec-firewall-bouncer.service: the overlay is enabled (systemctl enablecrowdsec-firewall-bouncer.service): doneoverlays.crowdsec: start crowdsec-firewall-bouncer.service (systemctl start crowdsec-firewall-bouncer.service):56% Keel Linux - First boot configuration Role of this node What this node is in its set of three (cloud advanced). Primary: the first node. It makes the mesh and invites the replica, then the witness, each with a line you copy to it. Replica: the second node. It joins with the first line, and its data follows the primary. Witness: the third node, Keel Core on a third site. It joins with the second line and gives etcd its third vote. It holds no data. Primary the first node: makes the mesh, invites Replica joins the primary; its data follows it <Select> typed: | role the screen, as textSimpleone node, no meshCloud simple two nodes, failover by handCloud simple two nodes, failover by handCloud advanced two nodes and a witness, failover by itself> == Keel Linux - First boot configuration Installation mode < ok >x /etc/keel/instance.yaml: installation.mode: cloud_advanced$ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yamlapply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9387)instance.fqdn: unchanged (/etc/hosts maps kc9387 to kc9387.pop.coop)derived.monit: crowdsec not watched: crowdsec.service starts only when /etc/crowdsec/local_api_credentials.yamlexists (ConditionPathExists)derived.monit: crowdsec-lapi not watched: its process crowdsec is not watched: crowdsec.service starts only when/etc/crowdsec/local_api_credentials.yaml exists (ConditionPathExists)derived.monit: write /etc/keel/monit/keel-manifest.conf: 5 unit(s) and 4 probe(s) of core (mode 0600): doneoverlays.vip: unchanged (disabled: keel-vip.service)overlays.etcd: etcd waits for its cluster: it forms at the third cloud advanced member's join, or with keel meshetcd form; nothing is started until thenoverlays.crowdsec: create /etc/crowdsec/online_api_credentials.yaml empty, which CrowdSec's unit needs and whichsays not registered yet (mode 0600): doneoverlays.crowdsec: register this machine with CrowdSec's local API; cscli writes the password to/etc/crowdsec/local_api_credentials.yaml (cscli --error machines add --auto --force): doneoverlays.crowdsec: register with CrowdSec's central API (cscli --error capi register): doneoverlays.crowdsec: register CrowdSec's firewall bouncer (cscli bouncers add) and write its key to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.local (mode 0600, never printed) and its name to/etc/crowdsec/bouncers/crowdsec-firewall-bouncer.yaml.id, mode: nftables: doneoverlays.crowdsec: enable crowdsec.service: the overlay is enabled (systemctl enable crowdsec.service): doneoverlays.crowdsec: start crowdsec.service (systemctl start crowdsec.service): doneoverlays.crowdsec: enable crowdsec-firewall-bouncer.service: the overlay is enabled (systemctl enablecrowdsec-firewall-bouncer.service): doneoverlays.crowdsec: start crowdsec-firewall-bouncer.service (systemctl start crowdsec-firewall-bouncer.service):doneapply --system-only: 9 change(s), 0 failed94% Keel Linux - First boot configuration Role of this node What this node is in its set of three (cloud advanced). Primary: the first node. It makes the mesh and invites the replica, then the witness, each with a line you copy to it. Replica: the second node. It joins with the first line, and its data follows the primary. Witness: the third node, Keel Core on a third site. It joins with the second line and gives etcd its third vote. It holds no data. Primary the first node: makes the mesh, invites Replica joins the primary; its data follows it Witness Keel Core on a third site: a vote, no data <Select> typed: |
| 5 | invite the screen, as textKeel Linux - First boot configuration keel mesh create: making the mesh... Keel Linux - First boot configuration Make the mesh < ok >x $ keel mesh createcreated the mesh: this node is fd81:3784:c324::1/64 on wg0, WireGuard on UDP 51820keel mesh invite prints the line that joins the next nodeconfirming the new overlayconfirmed from keel mesh createthe overlay has no peer, so nothing can cross it: keel mesh create confirmed it once the routes to the gatewaysand to the operator's session were found to still leave through the uplinkwg-quick@wg0 enabled: the overlay comes back up at bootthe network change stays; the revert is cancelledetcd: this node holds the mesh's root CA; etcd forms when the third cloud advanced member joinskeel mesh: exit 0, done>Invite a node This node invites the replica (node 2) into its mesh. Copy the line below to the replica (node 2): paste it into its Join a mesh screen, or run it there as root. It can be used once, until 2026-11-10T01:41:26Z. The line carries the service address of the pair, shown below: this node writes it as its appliance.vip, and the replica takes it from the join. Nobody types it. Copy this line to the replica (node 2), on one line, as it is. It is a secret: it lets one node join this mesh. keel mesh join - <<< <invite 1> VIP: fd81:3784:c324::ffff:1 Expires: 2026-11-10T01:41:26Z Press Enter to go on: typed: | join the screen, as textPrimary the first node: makes the mesh, invitesReplica joins the primary; its data follows it Keel Linux - First boot configuration Join a mesh Paste the line that Invite a node shows on the inviting node: keel mesh join - <<< keel2:... The token alone (keel2:...) is accepted too. It goes to keel on its standard input, never on a command line. < OK > <Cancel>x typed: | join the screen, as textPrimary the first node: makes the mesh, invitesWitness Keel Core on a third site: a vote, no data Keel Linux - First boot configuration Join a mesh Paste the line that Invite a node shows on the inviting node: keel mesh join - <<< keel2:... The token alone (keel2:...) is accepted too. It goes to keel on its standard input, never on a command line. typed: |
| 6 | invite2 the screen, as text4 3 2 1 0 Keel Linux - First boot configuration Waiting for the nodes Waiting for the replica (node 2) to join with the line, checked every 5 s. Back gives a menu: Paste accept line, when the join printed one (keel mesh accept keel1a:...), or the line again. This node: fd81:3784:c324::1/64 etcd: not_formed, voters 0 VIP: fd81:3784:c324::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0 Keel Linux - First boot configuration Waiting for the nodes Waiting for the replica (node 2) to join with the line, checked every 5 s. Back gives a menu: Paste accept line, when the join printed one (keel mesh accept keel1a:...), or the line again. This node: fd81:3784:c324::1/64 etcd: not_formed, voters 0 VIP: fd81:3784:c324::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0 Keel Linux - First boot configuration Waiting for the nodes Waiting for the replica (node 2) to join with the line, checked every 5 s. Back gives a menu: Paste accept line, when the join printed one (keel mesh accept keel1a:...), or the line again. This node: fd81:3784:c324::1/64 etcd: not_formed, voters 0 VIP: fd81:3784:c324::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0>Invite a node This node invites the witness (node 3, Keel Core) into its mesh. Copy the line below to the witness (node 3, Keel Core): paste it into its Join a mesh screen, or run it there as root. It can be used once, until 2026-11-10T01:44:45Z. The line carries the service address of the pair, shown below: this node writes it as its appliance.vip, and the replica takes it from the join. Nobody types it. Copy this line to the witness (node 3, Keel Core), on one line, as it is. It is a secret: it lets one node join this mesh. keel mesh join - <<< <invite 1><invite 2><invite 1><invite 1><invite 2><invite 1> VIP: fd81:3784:c324::ffff:1 Expires: 2026-11-10T01:44:45Z Press Enter to go on: typed: | alert email the screen, as textWaiting for the nodes Waiting for etcd to have 3 voters: the primary, the replica and the witness. etcd forms when the third node joins. This node: fd81:3784:c324::af97/64 Member: fd81:3784:c324::1, reached etcd: not_formed, voters 0 VIP: fd81:3784:c324::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0 Keel Linux - First boot configuration Waiting for the nodes Waiting for etcd to have 3 voters: the primary, the replica and the witness. etcd forms when the third node joins. This node: fd81:3784:c324::af97/64 Member: fd81:3784:c324::1, reached etcd: not_formed, voters 0 VIP: fd81:3784:c324::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0> == Keel Linux - First boot configuration Pair with the primary < ok >x $ keel vip pair fd81:3784:c324::1fd81:3784:c324::ffff:1 is the VIP of <public key> and<public key>, signed by bothetcd: fd81:3784:c324::ffff:1: its pair's role is grantedkeel vip: exit 0, done Keel Linux - First boot configuration Pair with the primary < ok >x $ keel spec apply --system-only --non-interactive --skip-network --defer-certificate --spec/etc/keel/instance.yamlapply --system-only: /etc/inithooks.conf not read or writteninstance.hostname: unchanged (kc9386)instance.fqdn: unchanged (/etc/hosts maps kc9386 to kc9386.pop.coop)derived.monit: write /etc/keel/monit/keel-manifest.conf: 10 unit(s) and 9 probe(s) of web (mode 0600): doneoverlays.etcd: unchanged (enabled: etcd.service)overlays.crowdsec: unchanged (enabled: crowdsec.service, crowdsec-firewall-bouncer.service)overlays.vip: enable keel-vip.service: the overlay is enabled (systemctl enable keel-vip.service): doneoverlays.vip: start keel-vip.service: queue it: its job runs after etcd.service, which is ready only when amajority of its cluster runs, and this run does not wait for that majority (systemctl start --no-blockkeel-vip.service): doneoverlays.nginx: unchanged (enabled: nginx.service)overlays.coraza: unchanged (enabled: /usr/lib/keel/overlays/coraza/state)overlays.anubis: unchanged (enabled: anubis@keel.service, /usr/lib/keel/overlays/anubis/state.d/50keel-web)overlays.syncthing: unchanged (enabled: syncthing.service)network.overlay: not brought up in this run (--skip-network)apply --system-only: 3 change(s), 0 failedkeel apply: exit 0, the spec was applied Keel Linux - First boot configuration Status of this node < ok >x $ keel vip statusvip fd81:3784:c324::ffff:1: this node's appliance.viprole: replicaepoch 1, held by <public key> at fd81:3784:c324::1carried here: norouted to: <public key>$ keel mesh statusthis node: fd81:3784:c324::af97/64 on wg0, WireGuard on UDP 51820mesh identity: ad146bc71818aa43cfdda944d7c2839bpublic key: <public key>peers: 2<public key> fd81:3784:c324::1/128 [2804:710:d0:5:be24:11ff:fe4e:c66d]:51820handshake 26 s ago<public key> fd81:3784:c324::1522/128[2804:710:d0:5:be24:11ff:fe45:a0c7]:51820 handshake 15 s agopending invites: 0etcd: 3 voter(s), 0 learner(s)keel-fd81-3784-c324--1 fd81:3784:c324::1 voter healthykeel-fd81-3784-c324--1522 fd81:3784:c324::1522 voter healthykeel-fd81-3784-c324--af97 fd81:3784:c324::af97 voter healthyleader: keel-fd81-3784-c324--1etcd: this member's certificate expires 2026-12-10 00:44 UTCvip fd81:3784:c324::ffff:1: this node's appliance.viprole: replicaepoch 1, held by <public key> at fd81:3784:c324::1carried here: norouted to: <public key>>keelfirstboot cloud: Keel Cloud is not available yet: no key is asked, and this node runs standalone. It is offered once /etc/keel/cloud-endpoint names the service. === Keel Linux - First boot configuration System Notifications and Critical Security Alerts Enable local system notifications (root@localhost) to be forwarded to your regular inbox. Notifications include security updates and system messages. Email: <Enable> < Skip >x typed: | alert email the screen, as text< OK > <Cancel>x <invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1>w<invite 1>wU<invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 1><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2>F<invite 2>FA<invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1>V<invite 2><invite 1>VI<invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1>DJ<invite 1><invite 1>J<invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2>Iq<invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2>Iq<invite 1><invite 2>q<invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 1><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 1><invite 2><invite 1><invite 2><invite 2><invite 2>D<invite 2>D_<invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2><invite 2>>Join a mesh Join a mesh: keel joins this node to the mesh. When the inviting node cannot be reached, keel prints a line keel mesh accept keel1a:... and waits: run that line on the inviting node, or paste it into its Paste accept line screen. endpoint 2804:710:d0:5:be24:11ff:fe45:a0c7, found on eth0 (--endpoint overrides it) confirming over the overlay confirmed from the inviter's answer over the overlay (invite a91b76d8e2788b1d) the overlay was tested: the inviter's answer over the overlay (invite a91b76d8e2788b1d) arrived at fd81:3784:c324::1522 on wg0, from fd81:3784:c324::1 wg-quick@wg0 enabled: the overlay comes back up at boot the network change stays; the revert is cancelled joined the mesh: this node is fd81:3784:c324::1522/64 on wg0 peer: <public key> at fd81:3784:c324::1, through [2804:710:d0:5:be24:11ff:fe4e:c66d]:51820 the mesh has 3 nodes: this node has them all as peers, and the inviter announces this node to the 1 other(s) over the overlay (one offline now learns of it at its next keel mesh sync) etcd: this node forms with 2 other member(s) vip: fd81:3784:c324::ffff:1, proposed by the inviter for the pair (appliance.vip on both nodes; keel mesh status --json gives it) Press Enter to go on: == Keel Linux - First boot configuration Status of this node < ok >x $ keel mesh statusthis node: fd81:3784:c324::1522/64 on wg0, WireGuard on UDP 51820mesh identity: ad146bc71818aa43cfdda944d7c2839bpublic key: <public key>peers: 2<public key> fd81:3784:c324::1/128 [2804:710:d0:5:be24:11ff:fe4e:c66d]:51820handshake 13 s ago<public key> fd81:3784:c324::af97/128[2804:7f0:9880:6c3:a3f2:6930:d841:f919]:51820 handshake 1 s agopending invites: 0etcd: 3 voter(s), 0 learner(s)keel-fd81-3784-c324--1 fd81:3784:c324::1 voter healthykeel-fd81-3784-c324--1522 fd81:3784:c324::1522 voter healthykeel-fd81-3784-c324--af97 fd81:3784:c324::af97 voter healthyleader: keel-fd81-3784-c324--1etcd: this member's certificate expires 2026-12-10 00:46 UTCvip: none (this node declares no appliance.vip and routes no other pair's)>keelfirstboot cloud: Keel Cloud is not available yet: no key is asked, and this node runs standalone. It is offered once /etc/keel/cloud-endpoint names the service. === Keel Linux - First boot configuration System Notifications and Critical Security Alerts Enable local system notifications (root@localhost) to be forwarded to your regular inbox. Notifications include security updates and system messages. Email: <Enable> < Skip >x typed: |
| 7 | alert email the screen, as text4 3 2 1 0 Keel Linux - First boot configuration Waiting for the nodes Waiting for the witness (node 3, Keel Core) to join with the line, checked every 5 s. Back gives a menu: Paste accept line, when the join printed one (keel mesh accept keel1a:...), or the line again. This node: fd81:3784:c324::1/64 Member: fd81:3784:c324::af97, reached etcd: not_formed, voters 0 VIP: fd81:3784:c324::ffff:1, holder none yet 5 <Select> < Back >x 4 3 2 1 0> == Keel Linux - First boot configuration Take the VIP Waiting for the replica to pair with this node (keel vip pair on the replica). Then this node applies its description and takes the VIP. If the replica says it paired and nothing moves here, choose Back and Take it now. This node: fd81:3784:c324::1/64 Member: fd81:3784:c324::af97, reached Member: fd81:3784:c324::1522, reached e Vx 5 <Select> < Back >x Keel Linux - First boot configuration Take the VIP < ok >x $ keel vip promotethis node holds fd81:3784:c324::ffff:1 at epoch 1, by etcd's lease 1023339398898542398the peers are told in the backgroundvip fd81:3784:c324::ffff:1: fd81:3784:c324::1522: appliedvip fd81:3784:c324::ffff:1: fd81:3784:c324::af97: appliedkeel vip: exit 0, done Keel Linux - First boot configuration Status of this node < ok >x $ keel vip statusvip fd81:3784:c324::ffff:1: this node's appliance.viprole: primaryepoch 1, held by <public key> at fd81:3784:c324::1etcd lease 1023339398898542398carried here: yesrouted to: no peer$ keel mesh statusthis node: fd81:3784:c324::1/64 on wg0, WireGuard on UDP 51820mesh identity: ad146bc71818aa43cfdda944d7c2839bpublic key: <public key>peers: 2<public key> fd81:3784:c324::af97/128[2804:7f0:9880:6c3:a3f2:6930:d841:f919]:51820 handshake 22 s ago<public key> fd81:3784:c324::1522/128[2804:710:d0:5:be24:11ff:fe45:a0c7]:51820 handshake 23 s agopending invites: 0etcd: 3 voter(s), 0 learner(s)keel-fd81-3784-c324--1 fd81:3784:c324::1 voter healthykeel-fd81-3784-c324--1522 fd81:3784:c324::1522 voter healthykeel-fd81-3784-c324--af97 fd81:3784:c324::af97 voter healthyleader: keel-fd81-3784-c324--1etcd: this member's certificate expires 2026-12-10 00:41 UTCvip fd81:3784:c324::ffff:1: this node's appliance.viprole: primaryepoch 1, held by <public key> at fd81:3784:c324::1etcd lease 1023339398898542398carried here: yesrouted to: no peer>keelfirstboot cloud: Keel Cloud is not available yet: no key is asked, and this node runs standalone. It is offered once /etc/keel/cloud-endpoint names the service. === Keel Linux - First boot configuration System Notifications and Critical Security Alerts Enable local system notifications (root@localhost) to be forwarded to your regular inbox. Notifications include security updates and system messages. Email: <Enable> < Skip >x typed: | web: site  typed: | web: webmin  typed: |
| 8 | web: site  typed: | web: webmin 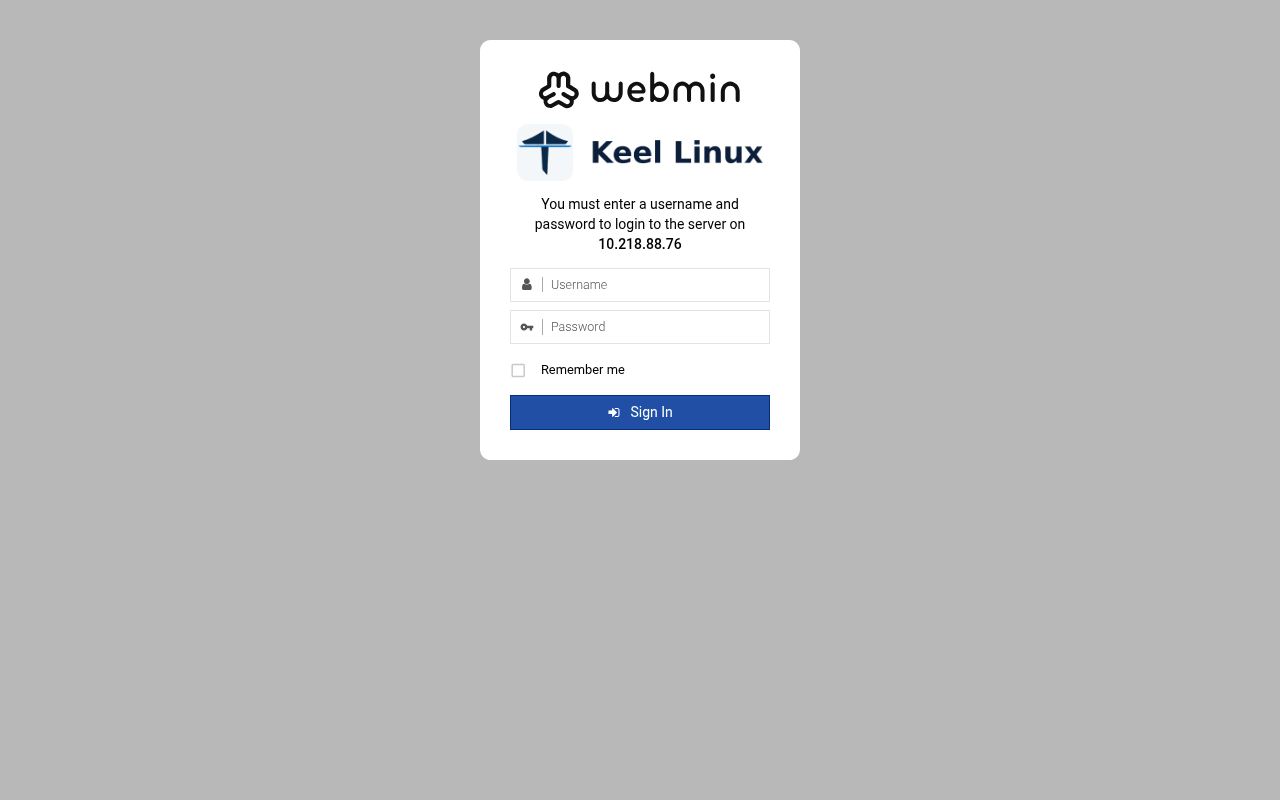 typed: | web: webmin-after 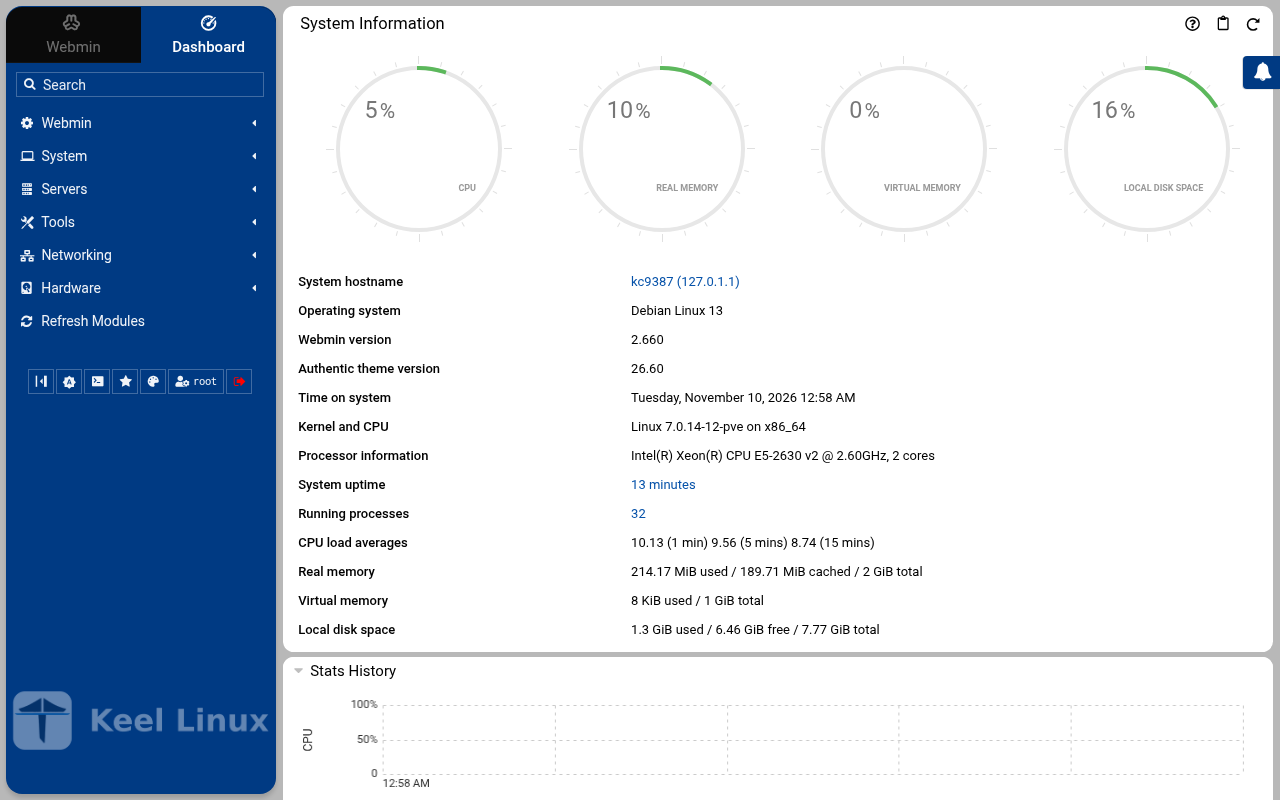 typed: |
| 9 | web: webmin 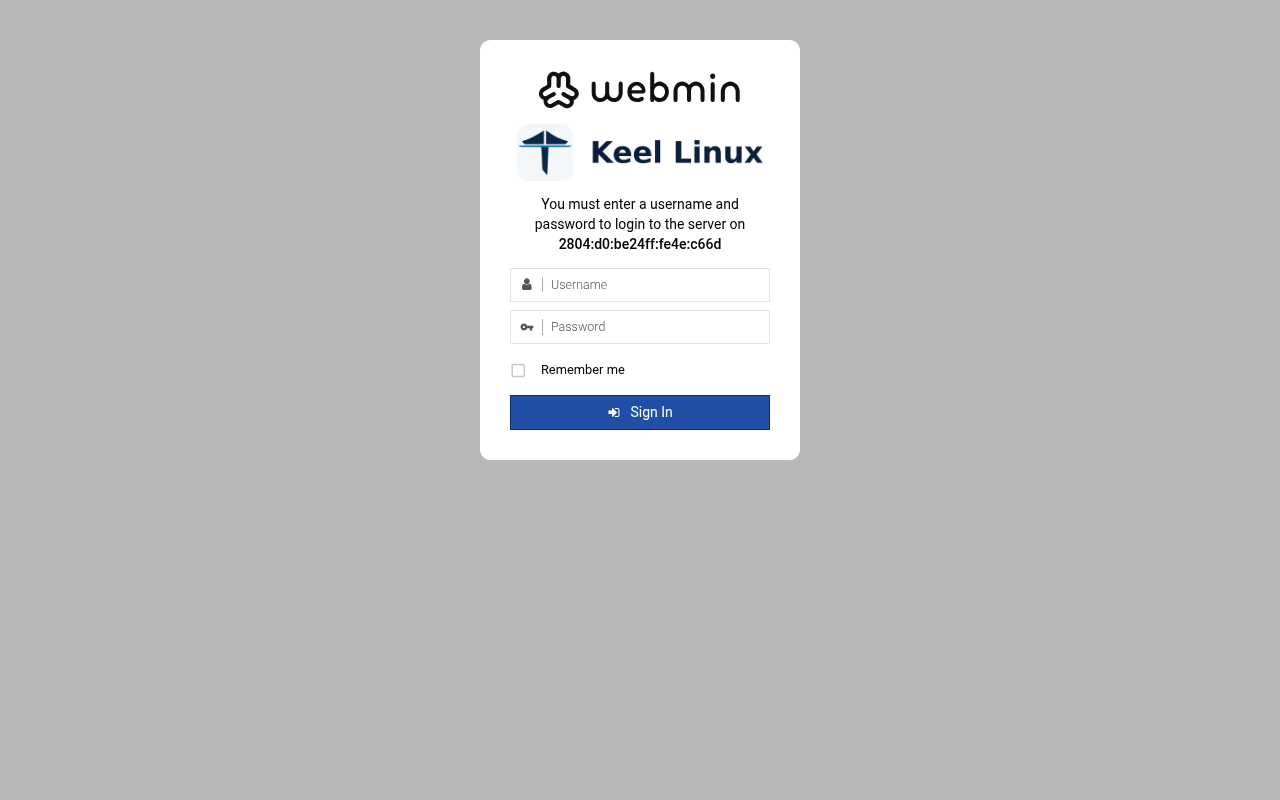 typed: | web: webmin-after 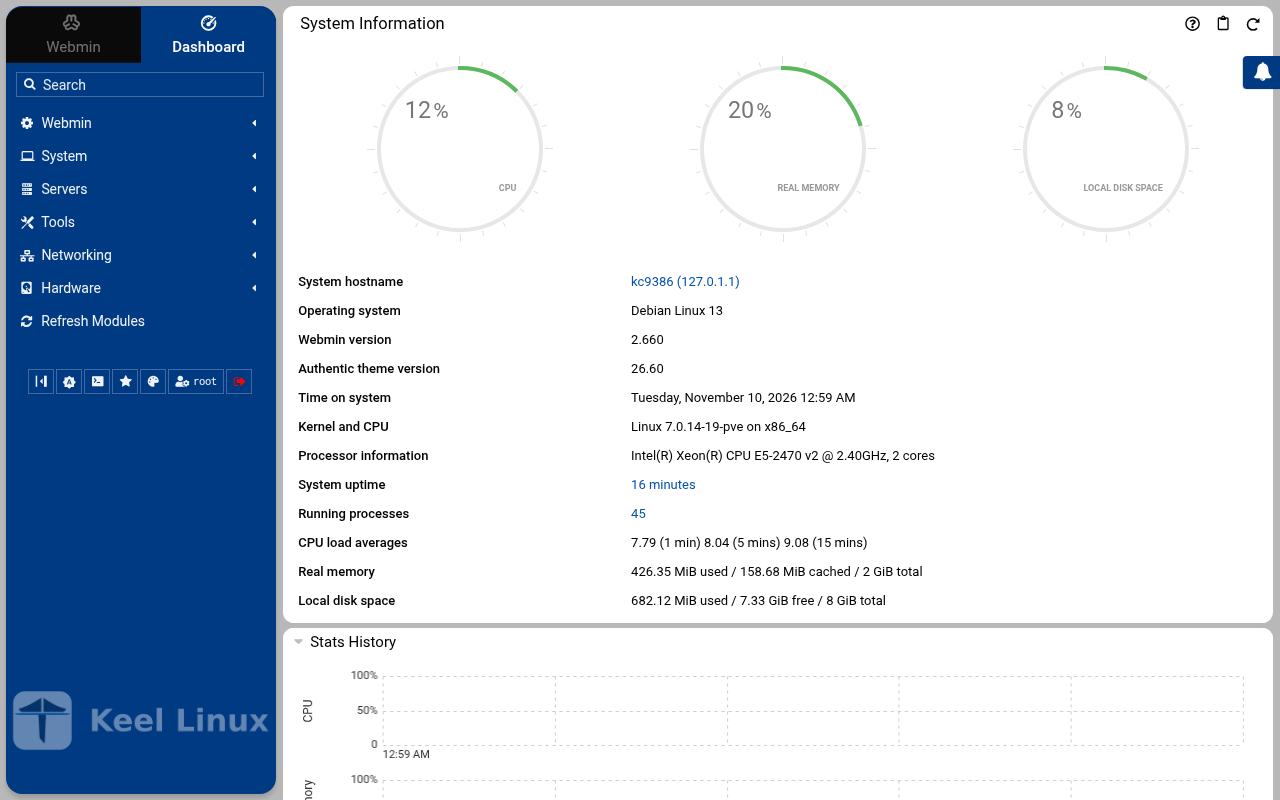 typed: | |
| 10 | web: webmin-after 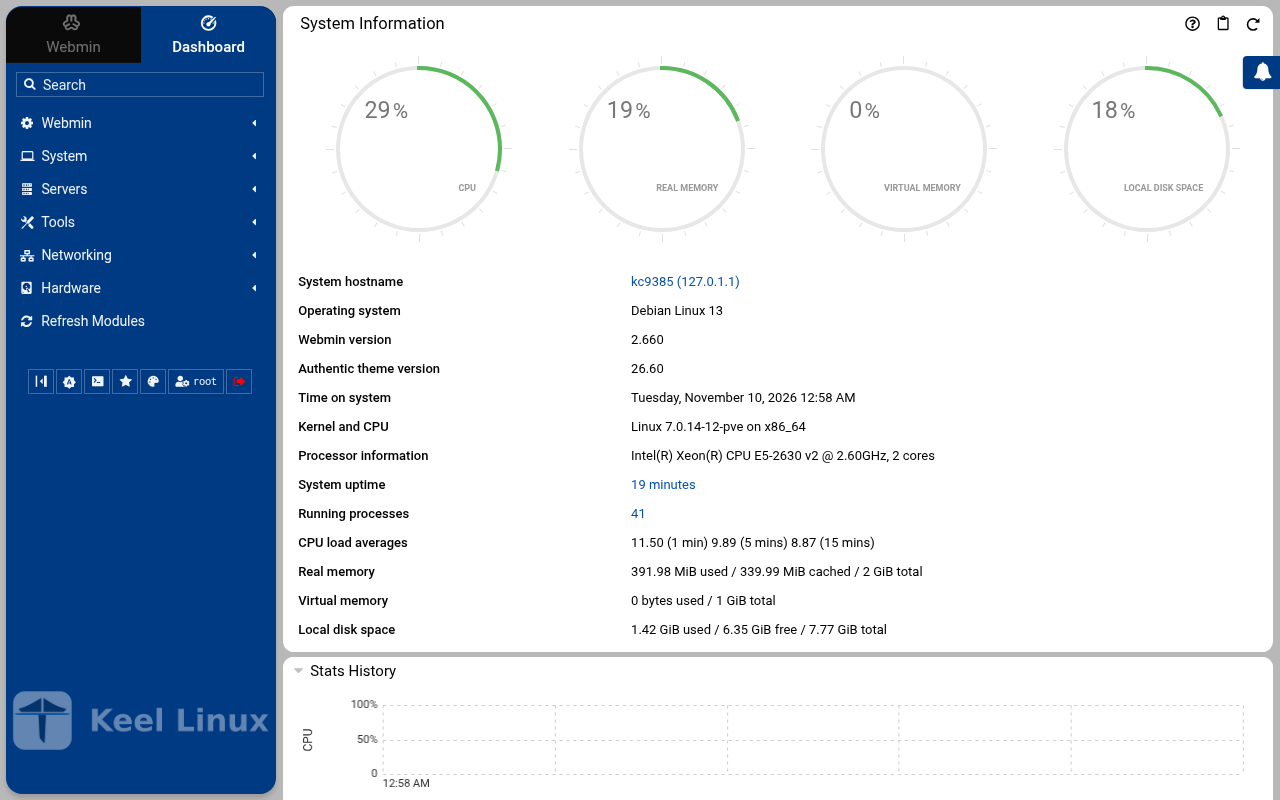 typed: |
Commissioning
8 passes on the sites BR1, BR2, 2026-11-10: 482 checks, all passed.
Every pass below passed every check (decision 0075). A page never shows an image that did not pass.
| Pass | Nodes | Date | Checks passed |
|---|---|---|---|
| the LXC template, answered on the console | br1 | 2026-11-10T00:07:47Z | 27 of 27 |
| the LXC template, described before the boot | br1 | 2026-11-10T00:21:26Z | 24 of 24 |
| the ISO in a virtual machine | br1 | 2026-11-10T00:08:59Z | 31 of 31 |
| the LXC template, answered on the console | br2 | 2026-11-10T00:08:58Z | 27 of 27 |
| the LXC template, described before the boot | br2 | 2026-11-10T00:22:49Z | 24 of 24 |
| the ISO in a virtual machine | br2 | 2026-11-10T00:12:24Z | 31 of 31 |
| Cloud simple: two nodes, failover by hand | primary br1, replica br2 | 2026-11-10T00:20:43Z | 131 of 131 |
| Cloud advanced: two data nodes and a witness | primary br1, replica br2, witness br1 | 2026-11-10T00:38:54Z | 187 of 187 |